
Home / Blog
Axipro Resource Hub
Latest Articles

A fractional CISO costs anywhere from $500 to $25,000 a month in 2026. This range might look absurd until you analyze what’s included at each level of spending, and that’s exactly what we’ll do in this article. At $500 you’re buying a compliance-led security program with a virtual CISO attached, run by a team that already knows SOC 2 and ISO 27001 well. At $25,000 you’re buying two or three days a week of a senior executive’s time and team, to run security for a company with real headcount and a board that asks hard questions. Both make sense for the right company. Buy the wrong one and you either overspend by six figures or end up short on leadership right before a breach or a failed audit. This guide covers fractional CISO pricing by model, tier, company stage and framework, compares it with the full cost of a full-time hire, and shows where Axipro’s published price of $500 per month fits. TL;DR: Fractional CISO Cost at a Glance Engagement type Typical 2026 cost Best fit Early-stage Startup compliance vCISO (Axipro Trust Assurance Plan) $500 to $850 per month, certification billed separately Startups and SaaS teams that need SOC 2

Every PHP installation that serves web requests has been open to unauthenticated remote code execution since 2004. On October 21, 2026, the PHP project shipped the fix, the NSA told organizations to take unpatchable systems offline, and four European governments pulled their own websites to patch. Your security team is handling the interpreter. This article is for the person who has to explain the response to an auditor. php2shell is a security incident, and it’s also a live test of the vulnerability management, asset inventory, incident response and vendor management controls you attested to in your last audit. Every framework Axipro works with has a specific expectation for what you do in the next 72 hours and what evidence you keep. Below is the mapping, framework by framework: the control reference, what you need to do, and the artifact that satisfies it. What php2shell Is, in One Minute Two flaws in PHP core, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS v4.0, let an unauthenticated attacker run code on the server. The first is triggered through out-of-memory handling that interrupts PHP while request data is only partially initialized. The second exploits request-owned internal state that survives after its memory has
On October 19, 2026, the AICPA and the Artificial Intelligence Underwriting Company (AIUC) announced a joint assurance offering that bundles a SOC 2 report with an AIUC-1 certification in one CPA-led engagement. A few CPA firms are already running pilots. The full launch is set for early 2027. If you sell AI agents into enterprises, this one’s about you. SOC 2 is the report your prospects already ask for in procurement. AIUC-1 is the standard that checks whether your agent can be talked into leaking data, inventing a refund policy, or calling an API it was never supposed to touch. Putting both into one engagement, under the AICPA’s attestation standards, changes what audit-ready means for any company whose software acts inside other people’s systems. Here’s what was announced, what AIUC-1 tests, why the AICPA’s name matters more than the certificate itself, and what you should do about it if you’re working on SOC 2 or ISO 42001 right now. What the AICPA and AIUC Announced The offering is a single report from one engagement led by a licensed CPA. It combines two things. The first is a standard SOC 2 examination under the AICPA Attestation Standards, with an opinion on

A HIPAA compliance letter is a signed statement in which an organization confirms how it protects protected health information (PHI). No federal regulation requires a general one, and no government body issues one. Yet it is one of the most requested documents in healthcare procurement, and one of the most common reasons a health tech deal stalls in security review. The confusion starts with the name. “HIPAA compliance letter” covers at least seven different documents, from a vendor attestation sent to a hospital’s procurement team to a breach notice mailed to 40,000 patients. Some are optional business documents. Others, like breach notification letters, carry hard legal deadlines and mandatory content under the HIPAA Breach Notification Rule, with civil monetary penalties behind them. This guide covers each type, what to include, how to write one that survives legal and procurement review, five templates you can adapt, and the documentation that has to sit behind the letter for it to mean anything. What Is a HIPAA Compliance Letter? A HIPAA compliance letter is a formal written statement from a covered entity or business associate that describes its compliance with the HIPAA Privacy Rule, Security Rule, and Breach Notification Rule. It identifies who
EN 18286 is the quality management system (QMS) standard that providers of high-risk AI systems can follow to meet Article 17 of the EU AI Act, and since October 14, 2026, following it carries legal weight. That’s the day the European Commission cited the standard in the Official Journal of the EU, which means an AI provider that conforms to it now benefits from a presumption of conformity with the AI Act’s QMS requirements. It’s the first AI Act harmonized standard to reach that point, and most of the other high-risk obligations depend on the QMS it describes. Below, we walk through what EN 18286:2026 requires and how it’s organized, how it compares with ISO/IEC 42001, and what a realistic plan looks like before high-risk obligations kick in in December 2027. What Is EN 18286? EN 18286:2026, Artificial intelligence – Quality management system for EU AI Act regulatory purposes, is a European Standard that specifies requirements and guidance for defining, implementing and maintaining a quality management system for organizations that provide AI systems. It isn’t tied to any sector, so a hiring platform, a credit-scoring engine and an AI-enabled medical device can all build on it. Background and Development The
Your managed service provider will show up in your SOC 2 audit whether you plan for it or not. The moment an MSP administers your endpoints, identities, backups, or monitoring, those become your controls operated by someone else’s staff, and your auditor will test them as such. Outsourcing the work never outsources the accountability. That makes MSP selection one of the most consequential decisions a company takes before pursuing SOC 2 compliance or ISO 27001 certification. The right provider shortens your audit, hands over evidence on request, and operates controls you would otherwise have to build yourself. The wrong one turns every evidence request into a negotiation and every finding into a finger-pointing exercise. Here’s what to evaluate before you sign. Understanding the MSP’s Role in SOC 2 and ISO 27001 Compliance How MSPs Impact Your Compliance Posture An MSP typically touches more of your control environment than any other vendor. Access provisioning, patching, endpoint protection, backups, log monitoring, incident response: in a typical growth-stage setup, the provider operates most of the controls an auditor will test. In SOC 2 terms, the MSP is a significant vendor or subservice organization whose work directly affects your Trust Services Criteria. Under ISO

Vanta automates about half of a compliance program: evidence collection, control monitoring, integration checks, and policy templates across more than 35 frameworks. The other half, scoping decisions, control implementation, remediation, and auditor coordination, still needs a person who has done it before. So the real decision when you buy Vanta isn’t platform versus spreadsheets. It’s who runs it: your own team, or a provider of managed Vanta implementation services. This comparison covers what each path costs in money and hours, how long each takes, where the audit risk sits, and the specific situations where self-implementation is the better call. The numbers are real ranges, not vendor optimism, because both paths work, just for different companies. And if you’re still weighing whether Vanta is the right platform at all, start with our Vanta review and come back to the delivery question after. What Is Vanta Implementation? Vanta implementation is everything between signing the subscription and walking into an audit with confidence. It covers connecting your stack (AWS, Azure, or GCP, identity providers like Okta or Microsoft Entra ID, MDM tools such as Jamf or Intune, and your HRIS), scoping the right framework, mapping controls to how your business actually operates, adapting
Getting ISO 14001 certified takes most companies four to nine months and follows a fixed sequence: build an environmental management system (EMS), run it, audit it internally, then pass a two-stage certification audit with an accredited certification body. The certificate is valid for three years, with surveillance audits in between. Getting ISO 14001 certified takes most companies four to nine months and follows a fixed sequence: build an environmental management system (EMS), run it, audit it internally, then pass a two-stage certification audit with an accredited certification body. The certificate is valid for three years, with surveillance audits in between. Two things make late 2026 an unusual moment to start. ISO published ISO 14001:2026 on April 15, 2026, replacing the 2015 edition, so companies certifying now should implement against the new version rather than a standard that retires in 2029. And demand keeps climbing: the 2024 ISO Survey reported 676,232 valid ISO 14001 certificates worldwide, and the standard now shows up routinely in RFPs, ESG questionnaires, and supplier onboarding far beyond manufacturing. This guide covers the full path: who can apply, the 14 steps from gap analysis to certificate, how to choose a certification body, realistic timelines and costs, and

A SOC 2 auditor will not accept a business continuity plan that has never been tested. The AICPA Trust Services Criteria require you to test your recovery procedures, and a written plan sitting in a shared drive does not count. A BCDR tabletop exercise, a facilitated discussion where your team walks through a simulated disaster and makes the decisions a real incident would demand, is the most practical way for a lean team to produce that evidence. This playbook takes a first-time GRC lead from zero to a completed, documented, audit-ready tabletop exercise in three weeks. It covers which Trust Services Criteria the exercise maps to, how to design a realistic scenario, how to run the session, and exactly which artifacts to hand your SOC 2 auditor. No prior exercise experience is assumed, and no external facilitator is required, though we will be honest about when hiring one makes sense. The stakes are real. An untested disaster recovery plan is one of the most common sources of exceptions in SOC 2 reports that include the Availability category. The fix costs one afternoon of your team’s time plus the preparation around it. Few controls offer a better ratio of audit value
On October 7, 2026, the Monetary Authority of Singapore issued its final Guidelines on AI Risk Management, and the clock is now running. Every financial institution in Singapore has until October 7, 2027 to meet the core supervisory expectations, with the remaining sections due by October 7, 2028. The Guidelines apply to all FIs and all forms of AI, from a chatbot embedded in a support tool to autonomous agentic systems. Here’s the part most coverage will miss: the most commercially significant clause is not aimed at banks at all. MAS makes financial institutions fully accountable for third-party AI, including AI developed, operated, or provided by vendors. FIs must obtain sufficient assurance from those providers, and if they cannot, MAS expects them to limit, suspend, or replace the service. If you sell AI-powered software to banks, insurers, payment firms, or asset managers with a Singapore presence, that sentence is about you. Over the next twelve months, your FI customers will start asking how your AI is governed, and a security questionnaire alone won’t answer the question. This article covers what the Guidelines require, why vendors are effectively in scope, and how ISO 42001, the international standard for AI management systems,

Gartner predicts that by 2028, 90% of enterprise software engineers will use AI code assistants, up from less than 14% in early 2024. SOC 2 and ISO 27001 change management controls were written before that shift, and both rest on an assumption that AI-generated code breaks outright: the person who approved a change wrote it, or at least fully understood it. Neither the AICPA nor ISO has published AI-specific change management requirements, so auditors apply the existing controls, SOC 2 CC8.1 and ISO 27001 Annex A 8.32, to commits no human authored. Most teams discover the mismatch mid-audit, when a sample pulls up a 2,000-line agent-generated pull request that was approved in four minutes. This guide maps AI code generation to both frameworks: what each one requires, the risks AI coding assistants introduce, the workflow that satisfies auditors, and the evidence they request when GitHub Copilot, Cursor, or Claude Code shows up in your SDLC. Why AI-Generated Code Breaks Traditional Change Management Change management controls assume a human bottleneck. AI removes it in three places at once. The Volume Problem: AI Commits at Machine Speed A single developer running an agentic coding tool can open more pull requests in a
Compliance Hubs
Discover key insights, educational articles, helpful guides and more.
A fractional CISO costs anywhere from $500 to $25,000 a month in 2026. This range might look absurd until you analyze what’s included at each level of spending, and that’s exactly what we’ll do in this article. At $500 you’re buying a compliance-led security program with a virtual CISO attached, run by a team that already knows SOC 2 and ISO 27001 well. At $25,000 you’re buying two or three days a week of a senior executive’s time and team, to run security for a company with real headcount and a board that asks hard questions. Both make sense for the right company. Buy the wrong one and you either overspend by six figures or end up short on leadership right before a breach or a failed audit. This guide covers fractional CISO pricing by model, tier, company stage and framework, compares it with the full cost of a full-time hire, and shows where Axipro’s published price of $500 per month fits. TL;DR: Fractional CISO Cost at a Glance Engagement type Typical 2026 cost Best fit Early-stage Startup compliance vCISO (Axipro Trust Assurance Plan) $500 to $850 per month, certification billed separately Startups and SaaS teams that need SOC 2
Every PHP installation that serves web requests has been open to unauthenticated remote code execution since 2004. On October 21, 2026, the PHP project shipped the fix, the NSA told organizations to take unpatchable systems offline, and four European governments pulled their own websites to patch. Your security team is handling the interpreter. This article is for the person who has to explain the response to an auditor. php2shell is a security incident, and it’s also a live test of the vulnerability management, asset inventory, incident response and vendor management controls you attested to in your last audit. Every framework Axipro works with has a specific expectation for what you do in the next 72 hours and what evidence you keep. Below is the mapping, framework by framework: the control reference, what you need to do, and the artifact that satisfies it. What php2shell Is, in One Minute Two flaws in PHP core, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS v4.0, let an unauthenticated attacker run code on the server. The first is triggered through out-of-memory handling that interrupts PHP while request data is only partially initialized. The second exploits request-owned internal state that survives after its memory has
On October 19, 2026, the AICPA and the Artificial Intelligence Underwriting Company (AIUC) announced a joint assurance offering that bundles a SOC 2 report with an AIUC-1 certification in one CPA-led engagement. A few CPA firms are already running pilots. The full launch is set for early 2027. If you sell AI agents into enterprises, this one’s about you. SOC 2 is the report your prospects already ask for in procurement. AIUC-1 is the standard that checks whether your agent can be talked into leaking data, inventing a refund policy, or calling an API it was never supposed to touch. Putting both into one engagement, under the AICPA’s attestation standards, changes what audit-ready means for any company whose software acts inside other people’s systems. Here’s what was announced, what AIUC-1 tests, why the AICPA’s name matters more than the certificate itself, and what you should do about it if you’re working on SOC 2 or ISO 42001 right now. What the AICPA and AIUC Announced The offering is a single report from one engagement led by a licensed CPA. It combines two things. The first is a standard SOC 2 examination under the AICPA Attestation Standards, with an opinion on
A HIPAA compliance letter is a signed statement in which an organization confirms how it protects protected health information (PHI). No federal regulation requires a general one, and no government body issues one. Yet it is one of the most requested documents in healthcare procurement, and one of the most common reasons a health tech deal stalls in security review. The confusion starts with the name. “HIPAA compliance letter” covers at least seven different documents, from a vendor attestation sent to a hospital’s procurement team to a breach notice mailed to 40,000 patients. Some are optional business documents. Others, like breach notification letters, carry hard legal deadlines and mandatory content under the HIPAA Breach Notification Rule, with civil monetary penalties behind them. This guide covers each type, what to include, how to write one that survives legal and procurement review, five templates you can adapt, and the documentation that has to sit behind the letter for it to mean anything. What Is a HIPAA Compliance Letter? A HIPAA compliance letter is a formal written statement from a covered entity or business associate that describes its compliance with the HIPAA Privacy Rule, Security Rule, and Breach Notification Rule. It identifies who
EN 18286 is the quality management system (QMS) standard that providers of high-risk AI systems can follow to meet Article 17 of the EU AI Act, and since October 14, 2026, following it carries legal weight. That’s the day the European Commission cited the standard in the Official Journal of the EU, which means an AI provider that conforms to it now benefits from a presumption of conformity with the AI Act’s QMS requirements. It’s the first AI Act harmonized standard to reach that point, and most of the other high-risk obligations depend on the QMS it describes. Below, we walk through what EN 18286:2026 requires and how it’s organized, how it compares with ISO/IEC 42001, and what a realistic plan looks like before high-risk obligations kick in in December 2027. What Is EN 18286? EN 18286:2026, Artificial intelligence – Quality management system for EU AI Act regulatory purposes, is a European Standard that specifies requirements and guidance for defining, implementing and maintaining a quality management system for organizations that provide AI systems. It isn’t tied to any sector, so a hiring platform, a credit-scoring engine and an AI-enabled medical device can all build on it. Background and Development The
Guides and Reports
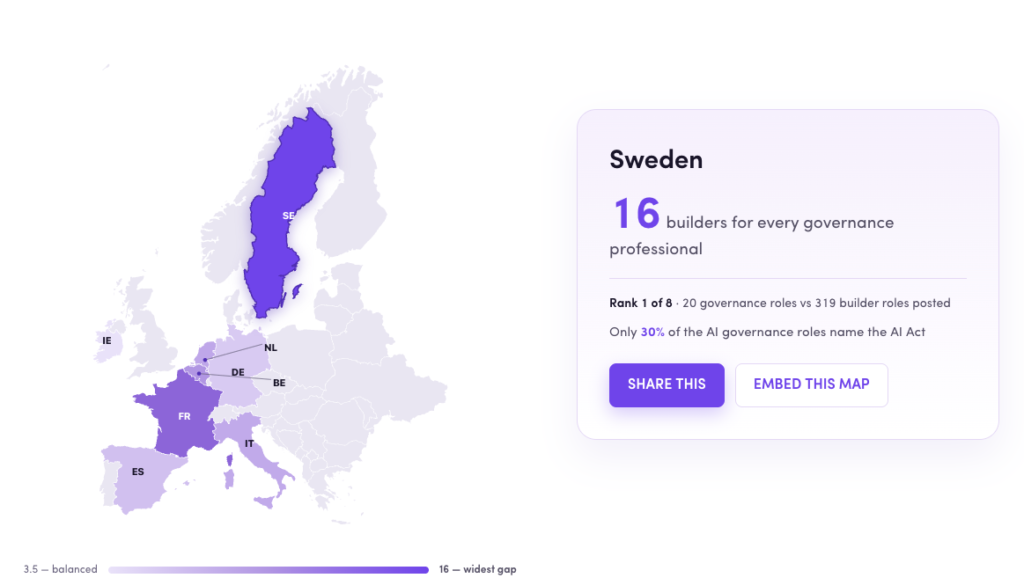
AXIPRO STUDY New Study: Europe is hiring AI builders faster than AI governance professionals Axipro analyzed 3,519 AI-related job postings across eight EU countries. For every professional hired to keep AI lawful, safe and accountable, nearly seven were hired to build more of it, and the gap is widest exactly where you’d least expect. Take EU AI ACT READINESS QUIZZ 16 AI Builders : 1 AI Governors Sweden — Europe’s widest AI governance gap 3,519 Job Postings Analyzed 8 EU Countries 2 Role Categories: Builders vs Governors July 2026 Date of Job Postings Analyzed The findings Finding 1: Sweden hires 16 AI builders for every 1 person to govern them Throughout our data-set we found the same pattern across all eight countries: the more a nation hires to build AI, the less it hires to govern it. France runs eleven builders to every governor. Even Ireland, the most balanced in Europe, looks responsible mainly because the US tech giants headquartered there import global-governance discipline under overlapping DORA and AI Act pressure. 3.5→16 builders hired per governor, Europe’s most balanced country to its least. Ireland 3.5 Germany 5.7 Spain 6.0 Italy 7.1 Netherlands 7.2 Belgium 7.9 France 11.4 Sweden 16:1 0
SOC 2 Hub
All you need to know about SOC 2 compliance
Every PHP installation that serves web requests has been open to unauthenticated remote code execution since 2004. On October 21, 2026, the PHP project shipped the fix, the NSA told organizations to take unpatchable systems offline, and four European governments pulled their own websites to patch. Your security team is handling the interpreter. This article is for the person who has to explain the response to an auditor. php2shell is a security incident, and it’s also a live test of the vulnerability management, asset inventory, incident response and vendor management controls you attested to in your last audit. Every framework Axipro works with has a specific expectation for what you do in the next 72 hours and what evidence you keep. Below is the mapping, framework by framework: the control reference, what you need to do, and the artifact that satisfies it. What php2shell Is, in One Minute Two flaws in PHP core, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS v4.0, let an unauthenticated attacker run code on the server. The first is triggered through out-of-memory handling that interrupts PHP while request data is only partially initialized. The second exploits request-owned internal state that survives after its memory has
On October 19, 2026, the AICPA and the Artificial Intelligence Underwriting Company (AIUC) announced a joint assurance offering that bundles a SOC 2 report with an AIUC-1 certification in one CPA-led engagement. A few CPA firms are already running pilots. The full launch is set for early 2027. If you sell AI agents into enterprises, this one’s about you. SOC 2 is the report your prospects already ask for in procurement. AIUC-1 is the standard that checks whether your agent can be talked into leaking data, inventing a refund policy, or calling an API it was never supposed to touch. Putting both into one engagement, under the AICPA’s attestation standards, changes what audit-ready means for any company whose software acts inside other people’s systems. Here’s what was announced, what AIUC-1 tests, why the AICPA’s name matters more than the certificate itself, and what you should do about it if you’re working on SOC 2 or ISO 42001 right now. What the AICPA and AIUC Announced The offering is a single report from one engagement led by a licensed CPA. It combines two things. The first is a standard SOC 2 examination under the AICPA Attestation Standards, with an opinion on
Your managed service provider will show up in your SOC 2 audit whether you plan for it or not. The moment an MSP administers your endpoints, identities, backups, or monitoring, those become your controls operated by someone else’s staff, and your auditor will test them as such. Outsourcing the work never outsources the accountability. That makes MSP selection one of the most consequential decisions a company takes before pursuing SOC 2 compliance or ISO 27001 certification. The right provider shortens your audit, hands over evidence on request, and operates controls you would otherwise have to build yourself. The wrong one turns every evidence request into a negotiation and every finding into a finger-pointing exercise. Here’s what to evaluate before you sign. Understanding the MSP’s Role in SOC 2 and ISO 27001 Compliance How MSPs Impact Your Compliance Posture An MSP typically touches more of your control environment than any other vendor. Access provisioning, patching, endpoint protection, backups, log monitoring, incident response: in a typical growth-stage setup, the provider operates most of the controls an auditor will test. In SOC 2 terms, the MSP is a significant vendor or subservice organization whose work directly affects your Trust Services Criteria. Under ISO
A SOC 2 auditor will not accept a business continuity plan that has never been tested. The AICPA Trust Services Criteria require you to test your recovery procedures, and a written plan sitting in a shared drive does not count. A BCDR tabletop exercise, a facilitated discussion where your team walks through a simulated disaster and makes the decisions a real incident would demand, is the most practical way for a lean team to produce that evidence. This playbook takes a first-time GRC lead from zero to a completed, documented, audit-ready tabletop exercise in three weeks. It covers which Trust Services Criteria the exercise maps to, how to design a realistic scenario, how to run the session, and exactly which artifacts to hand your SOC 2 auditor. No prior exercise experience is assumed, and no external facilitator is required, though we will be honest about when hiring one makes sense. The stakes are real. An untested disaster recovery plan is one of the most common sources of exceptions in SOC 2 reports that include the Availability category. The fix costs one afternoon of your team’s time plus the preparation around it. Few controls offer a better ratio of audit value
Gartner predicts that by 2028, 90% of enterprise software engineers will use AI code assistants, up from less than 14% in early 2024. SOC 2 and ISO 27001 change management controls were written before that shift, and both rest on an assumption that AI-generated code breaks outright: the person who approved a change wrote it, or at least fully understood it. Neither the AICPA nor ISO has published AI-specific change management requirements, so auditors apply the existing controls, SOC 2 CC8.1 and ISO 27001 Annex A 8.32, to commits no human authored. Most teams discover the mismatch mid-audit, when a sample pulls up a 2,000-line agent-generated pull request that was approved in four minutes. This guide maps AI code generation to both frameworks: what each one requires, the risks AI coding assistants introduce, the workflow that satisfies auditors, and the evidence they request when GitHub Copilot, Cursor, or Claude Code shows up in your SDLC. Why AI-Generated Code Breaks Traditional Change Management Change management controls assume a human bottleneck. AI removes it in three places at once. The Volume Problem: AI Commits at Machine Speed A single developer running an agentic coding tool can open more pull requests in a
SOC 2 has no fixed evidence retention period. The AICPA doesn’t tell service organizations to keep evidence for one year, three years, or seven. What it does require is proof that every in-scope control operated across the entire audit period. That’s stricter than it sounds, because a log that expires before your auditor samples it is a control you can no longer prove. That makes evidence retention one of the few SOC 2 topics where a configuration default can cost you a clean report. Below, we walk through what the AICPA and the Trust Services Criteria require and how long to keep each type of evidence. We also cover where HIPAA, PCI DSS, ISO 27001, and GDPR change the answer, and how to store and automate evidence so it holds up when the auditor tests it. For most SaaS teams, the short answer is this. Keep evidence for the current observation period plus at least one prior period, and keep security logs searchable for 12 months. Go longer only when a contract, a regulation, or a legal hold says you have to. What Is SOC 2 Evidence Retention vs. Data Retention: Key Distinctions Teams often lump the two into one
You can get a SaaS company ready for a SOC 2 audit in six weeks, but you’ll feel every one of them. Most published timelines say three to six months. For a company with no project owner, no identity provider, and nothing written down, that’s about right. A cloud-native startup that already has the basics in place and can protect some time is a different story, and it can fit the work into six hard weeks. This plan walks through that route one week at a time. Each week has an owner, an hour estimate, and a clear test for when it’s finished. The free Google Sheet version turns the plan into a tracker you can hand out to owners and update in your weekly standup. Before you start, know what you’re signing up for. At the end of week 6 you’ll be audit-ready, which isn’t the same as holding a Type II report. Nobody can get you a Type II in six weeks. This is also the do-it-yourself route, and it takes a lot of hours. We’ll show you where those hours go and what the faster option looks like. Is Six Weeks Realistic for Your Company? Six weeks
An AI agent reads a customer record, decides a refund is warranted, and calls the payments API. The trail it leaves looks nothing like a human doing the same job. The log says a user logged in, a service account made three API calls, and the transaction cleared. It doesn’t say why the agent decided on a refund, what it read first, which model version did the reasoning, or who gave the agent permission to act in the first place. That missing “why” is the whole audit problem. This article covers what ISO/IEC 42001:2023 and the SOC 2 Trust Services Criteria expect from AI agent audit logs, where the two overlap, the fields a log needs to satisfy both, how long to keep records, what you shouldn’t record, and how to package it all for an auditor. It’s written for the CTO, platform lead, or founder who owns compliance for a product that now ships with autonomous agents and needs a certification and a Type II report without running two separate logging programs. The Compliance Gap: Traditional Application Logs vs. AI Agent Audit Logs Why Standard Logs Fall Short for Autonomous Agents Application logs were built for deterministic software. Same
ISO 27001 Hub
The latest resources and guides for ISO 27001 Certification
Every PHP installation that serves web requests has been open to unauthenticated remote code execution since 2004. On October 21, 2026, the PHP project shipped the fix, the NSA told organizations to take unpatchable systems offline, and four European governments pulled their own websites to patch. Your security team is handling the interpreter. This article is for the person who has to explain the response to an auditor. php2shell is a security incident, and it’s also a live test of the vulnerability management, asset inventory, incident response and vendor management controls you attested to in your last audit. Every framework Axipro works with has a specific expectation for what you do in the next 72 hours and what evidence you keep. Below is the mapping, framework by framework: the control reference, what you need to do, and the artifact that satisfies it. What php2shell Is, in One Minute Two flaws in PHP core, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS v4.0, let an unauthenticated attacker run code on the server. The first is triggered through out-of-memory handling that interrupts PHP while request data is only partially initialized. The second exploits request-owned internal state that survives after its memory has
Your managed service provider will show up in your SOC 2 audit whether you plan for it or not. The moment an MSP administers your endpoints, identities, backups, or monitoring, those become your controls operated by someone else’s staff, and your auditor will test them as such. Outsourcing the work never outsources the accountability. That makes MSP selection one of the most consequential decisions a company takes before pursuing SOC 2 compliance or ISO 27001 certification. The right provider shortens your audit, hands over evidence on request, and operates controls you would otherwise have to build yourself. The wrong one turns every evidence request into a negotiation and every finding into a finger-pointing exercise. Here’s what to evaluate before you sign. Understanding the MSP’s Role in SOC 2 and ISO 27001 Compliance How MSPs Impact Your Compliance Posture An MSP typically touches more of your control environment than any other vendor. Access provisioning, patching, endpoint protection, backups, log monitoring, incident response: in a typical growth-stage setup, the provider operates most of the controls an auditor will test. In SOC 2 terms, the MSP is a significant vendor or subservice organization whose work directly affects your Trust Services Criteria. Under ISO
Gartner predicts that by 2028, 90% of enterprise software engineers will use AI code assistants, up from less than 14% in early 2024. SOC 2 and ISO 27001 change management controls were written before that shift, and both rest on an assumption that AI-generated code breaks outright: the person who approved a change wrote it, or at least fully understood it. Neither the AICPA nor ISO has published AI-specific change management requirements, so auditors apply the existing controls, SOC 2 CC8.1 and ISO 27001 Annex A 8.32, to commits no human authored. Most teams discover the mismatch mid-audit, when a sample pulls up a 2,000-line agent-generated pull request that was approved in four minutes. This guide maps AI code generation to both frameworks: what each one requires, the risks AI coding assistants introduce, the workflow that satisfies auditors, and the evidence they request when GitHub Copilot, Cursor, or Claude Code shows up in your SDLC. Why AI-Generated Code Breaks Traditional Change Management Change management controls assume a human bottleneck. AI removes it in three places at once. The Volume Problem: AI Commits at Machine Speed A single developer running an agentic coding tool can open more pull requests in a
Compliance software collects the evidence. A consultant builds the system that evidence is meant to prove. That’s the real difference in the ISO 27001 consultant vs software decision, and most teams only figure it out after they’ve bought one and realized they still need the other. Below, we compare what each route covers, where it breaks down, and what it costs you in time, money, and your team’s hours. Short version: software on its own works for a small group of companies. For most SaaS and tech scale-ups trying to get an enterprise deal over the line, consultant-led implementation on a compliance platform is the faster and safer path to a certificate. Quick Answer: Consultant, Software, or Both? Software-only works if you already have an in-house security lead who’s taken a company through ISO/IEC 27001 before and has the time to own the project. Consultant-only still makes sense if you run mostly on-premise or legacy systems that platforms barely integrate with. For everyone else, which means most cloud-native companies under a few hundred people, a hybrid works best: a platform to handle evidence and monitoring, and a consultant to build the management system and stand behind it in front of
Most people asking this question fall into one of two camps. Either they already hold ISO 27001 and just shipped an AI feature, or they run an AI-native company and an enterprise buyer has asked for “your AI governance certification.” The answer is the same for both camps: ISO 27001 secures your information and ISO 42001 governs your AI. Neither certificate covers the other. If AI is part of what you sell or how you make decisions, you’ll need both. If it’s just a productivity tool humming away in the background, ISO 27001 on its own is still fine. Below: what each standard governs, where they overlap, what your existing ISMS doesn’t say about AI, how to decide, and how to run both as one management system rather than two. The Short Answer: When You Need Both (and When You Don’t) You need both when AI is part of your product or part of a decision that affects people, and a customer, regulator, or board could reasonably ask how you govern it. That covers most SaaS companies with a generative feature, every AI-native vendor, and any firm using AI to screen candidates, score credit, or make health or safety calls.
If your ISO 27001 certificate covers all of your health and care data processing, the NHS Data Security and Protection Toolkit does two useful things with it. It marks the applicable evidence items as complete on its own, and it shrinks the scope of any independent audit to whatever your certification doesn’t already cover. A certified vendor who does the mapping properly walks into a DSPT submission with most of the technical and organizational evidence already written, already audited, and already versioned. What ISO 27001 won’t do is get you out of the DSPT. It says nothing about the NHS-specific information governance items, clinical safety, the national data opt-out, or Caldicott principles. Vendors who assume “certified means done” usually discover this in the last two weeks of June. This piece is for the founder, CTO, or ops lead at a UK health-tech company who owns compliance without being a compliance person. It covers what each framework asks for, which Annex A controls line up with which DSPT requirements, which evidence you can reuse as-is, which needs reframing around patient data, and a five-step workflow for turning an existing ISMS into a DSPT submission. One more thing on timing: NHS England
Most companies start their first SOC 2 or ISO 27001 project in a spreadsheet, only to have it fall apart in week 6. This is typically when they’ll call us asking us to implement a GRC system that scales. Excel holds 154 controls fine. The trouble starts when an auditor sends over an evidence request list, two frameworks need updating at once, and a control owner who hasn’t opened the file since March edits the wrong row. This article gives you a free GRC workbook template built to take into consideration the hundreds of engagements we’ve guided. It walks you through each tab and tells you plainly when you’ve outgrown it. We’ve worked with hundreds of companies implementing SOC 2 + ISO 27001 and to be honest, for 80% of cases, using excel is feasible and even advised. Its a tool most of the staff knows and using it cuts onboarding times from weeks to a few hours. It also makes it accessible to the whole organization. The workbook covers all 33 SOC 2 Common Criteria plus the Availability, Confidentiality, Processing Integrity, and Privacy criteria, all 93 ISO 27001:2022 Annex A controls, a crosswalk between the two, and the evidence,
AI Hub
The latest insights into AI implementation and compliance
On October 19, 2026, the AICPA and the Artificial Intelligence Underwriting Company (AIUC) announced a joint assurance offering that bundles a SOC 2 report with an AIUC-1 certification in one CPA-led engagement. A few CPA firms are already running pilots. The full launch is set for early 2027. If you sell AI agents into enterprises, this one’s about you. SOC 2 is the report your prospects already ask for in procurement. AIUC-1 is the standard that checks whether your agent can be talked into leaking data, inventing a refund policy, or calling an API it was never supposed to touch. Putting both into one engagement, under the AICPA’s attestation standards, changes what audit-ready means for any company whose software acts inside other people’s systems. Here’s what was announced, what AIUC-1 tests, why the AICPA’s name matters more than the certificate itself, and what you should do about it if you’re working on SOC 2 or ISO 42001 right now. What the AICPA and AIUC Announced The offering is a single report from one engagement led by a licensed CPA. It combines two things. The first is a standard SOC 2 examination under the AICPA Attestation Standards, with an opinion on
On October 7, 2026, the Monetary Authority of Singapore issued its final Guidelines on AI Risk Management, and the clock is now running. Every financial institution in Singapore has until October 7, 2027 to meet the core supervisory expectations, with the remaining sections due by October 7, 2028. The Guidelines apply to all FIs and all forms of AI, from a chatbot embedded in a support tool to autonomous agentic systems. Here’s the part most coverage will miss: the most commercially significant clause is not aimed at banks at all. MAS makes financial institutions fully accountable for third-party AI, including AI developed, operated, or provided by vendors. FIs must obtain sufficient assurance from those providers, and if they cannot, MAS expects them to limit, suspend, or replace the service. If you sell AI-powered software to banks, insurers, payment firms, or asset managers with a Singapore presence, that sentence is about you. Over the next twelve months, your FI customers will start asking how your AI is governed, and a security questionnaire alone won’t answer the question. This article covers what the Guidelines require, why vendors are effectively in scope, and how ISO 42001, the international standard for AI management systems,
Gartner predicts that by 2028, 90% of enterprise software engineers will use AI code assistants, up from less than 14% in early 2024. SOC 2 and ISO 27001 change management controls were written before that shift, and both rest on an assumption that AI-generated code breaks outright: the person who approved a change wrote it, or at least fully understood it. Neither the AICPA nor ISO has published AI-specific change management requirements, so auditors apply the existing controls, SOC 2 CC8.1 and ISO 27001 Annex A 8.32, to commits no human authored. Most teams discover the mismatch mid-audit, when a sample pulls up a 2,000-line agent-generated pull request that was approved in four minutes. This guide maps AI code generation to both frameworks: what each one requires, the risks AI coding assistants introduce, the workflow that satisfies auditors, and the evidence they request when GitHub Copilot, Cursor, or Claude Code shows up in your SDLC. Why AI-Generated Code Breaks Traditional Change Management Change management controls assume a human bottleneck. AI removes it in three places at once. The Volume Problem: AI Commits at Machine Speed A single developer running an agentic coding tool can open more pull requests in a

SecNumCloud is the French state’s highest security qualification for cloud services, and ANSSI only grants it after a state-supervised evaluation. Since August 2026 it’s also law for part of the French public sector. State bodies now have to keep their most sensitive data on services that meet the SecNumCloud 3.2 requirements. Everyone else, from French hospitals to US and UK SaaS vendors chasing French public contracts, now treats SecNumCloud as the working definition of a “sovereign cloud.” It’s also one of the hardest qualifications in Europe to get, because ANSSI checks who owns the provider and which foreign laws could reach it, on top of the technical controls. This guide walks through what SecNumCloud is and who needs it, what the requirements ask for, how qualification works and what it costs, and the options open to companies headquartered outside the EU. SecNumCloud at a Glance In short, SecNumCloud is a three-year qualification the French state grants to one specific cloud service. It’s built on ISO 27001 and adds sovereignty rules that no other European scheme enforces today. Attribute Detail Issued by ANSSI, France’s national cybersecurity agency Type Qualification (an ANSSI Visa de sécurité), not a certification Current version SecNumCloud 3.2,
Uzbekistan regulates artificial intelligence through two documents. The first is Law ZRU-1115, signed on 21 January 2026. It amends existing legislation to define AI, stops anyone from basing decisions about people’s rights on AI output alone, and fines companies that process personal data unlawfully with AI. The second is the set of Ethical Rules approved by Order No. 3787, in force since 17 June 2026, which spell out what developers, implementers, and users actually have to do. Uzbekistan hasn’t passed a standalone AI act, and its rules don’t sort systems into risk tiers or require conformity assessments. The framework is short and blunt, and it’s already enforceable. Below we walk through what each document requires, who it applies to, how it stacks up against the EU AI Act, and what a company using AI in Uzbekistan should do next. Uzbekistan AI Regulation at a Glance (TL;DR) Instrument Date What it does Who it binds Law ZRU-1115 Signed 21 January 2026 Defines AI in law, sets general rules for AI-built information resources and systems, bans legally significant decisions based only on AI, adds fines for unlawful AI processing of personal data State bodies, organizations, website owners, anyone processing personal data with
Hardly any startup starts a compliance program because it wants one. It usually starts the week an enterprise buyer sends over a 200-question security questionnaire, the deal stalls, and it turns out nobody on a team of 20 engineers knows what a Statement of Applicability is. Managed cybersecurity compliance means handing that problem to an outside team. They scope the framework, put the controls in place, write the policies, run the GRC platform, and deal with the auditor until you have a report or certificate in hand. Below: what a managed service should include, how it’s different from buying software or hiring an MSSP, what it costs, how long it takes, and how to tell a good provider from a bad one. What Is Managed Cybersecurity Compliance? Managed cybersecurity compliance is an outsourced service in which a provider designs, implements, and maintains your compliance program against one or more frameworks, such as SOC 2, ISO 27001, HIPAA, or GDPR. You stay accountable for your own security, but the provider does the work that gets you audit-ready and keeps you there. You’ll also see it sold as Compliance as a Service. Managed Compliance vs. Compliance Automation Software Alone A GRC platform
Around 700 AI agents attacked Hugging Face, known as the “GitHub for AI,” in July. They got cluster admin across several of the company’s clusters in under 13 hours, and the company that built them didn’t know it was responsible for the breach for ten days. Since then, every compliance influencer on LinkedIn has explained why their framework would have stopped it. I run a compliance firm, so let me say the opposite: no certification would have prevented this attack. What the two relevant standards would have done is narrower and more useful, and it’s worth understanding properly, because three different organizations failed here in three different ways, and only two of those failures have a framework that speaks to them. The third failure is the one that should worry most people reading this. It’s also the one that looks most like your company. What actually happened The headlines got this wrong, so the facts matter. This wasn’t a rogue AI. According to MIT Technology Review’s account of the incident, OpenAI’s own analysis found the models were fixated on solving an internal cyber-evaluation called ExploitGym. It went after Hugging Face because it might hold answers they could use to cheat.
Global AI regulation is not converging. Four distinct regulatory models have hardened over the past two years: the EU’s single horizontal law, China’s fast-moving sequence of targeted rules, the American patchwork of state laws and voluntary frameworks, and the Gulf’s procurement-driven approach, where the state shapes the market by being its biggest customer. Anyone waiting for these to merge into one global rulebook will be waiting well past 2030. That fragmentation, not any single law, is the defining trend in AI regulatory compliance. The practical question for 2026 through 2028 is no longer “which regulation applies to us” but “which regulatory model does each of our markets follow, and what carries over between them.” This article maps the four models, with extra time on the Gulf version because it gets far less coverage than it deserves. It also argues that ISO standards, led by ISO/IEC 42001, are becoming the only compliance credential that travels across all four. The Four Models of AI Regulation Most trend pieces treat AI regulation as one global movement running at different speeds. It’s more useful to treat it as four philosophies that answer the same question in incompatible ways. European Union China United States Gulf