SOC 2 is not a certification, and no auditor will ever hand you a SOC 2 certificate. What you receive at the end of the audit is an attestation report: a detailed document, often 60 to 100 pages long, in which a licensed CPA firm expresses a professional opinion on your controls. That distinction sounds like pedantry until a prospect’s security team asks to see your “certificate” and you have nothing that looks like one. This article explains exactly what a SOC 2 report is, what it contains, how it differs from an ISO 27001 certificate, and how to talk about your SOC 2 status without misrepresenting it.
Is SOC 2 a Certification or a Report?
The Common Misconception About “SOC 2 Certification”
Search volume tells the story: far more people look for “SOC 2 certification” than for “SOC 2 attestation,” and sales teams, procurement questionnaires, and even some auditors use the certification shorthand daily. The misconception is understandable. Every other major framework in the compliance stack, from ISO 27001 to PCI DSS, ends in something that looks like a pass. SOC 2 does not work that way, and treating it as if it does leads to awkward conversations during vendor due diligence.
Why SOC 2 Is Technically an Attestation, Not a Certification
A certification is a binary judgment issued by an accredited body: you meet the standard, or you do not. SOC 2 sits under the AICPA’s attestation standards, primarily SSAE 18 and its later amendments (SSAE 21 updated the relevant examination sections), specifically AT-C section 105 and AT-C section 205. Under those standards, an independent service auditor examines your controls and reports an opinion on them. Nobody “passes.” The auditor attests to what they found, in writing, with evidence. The output is a report, and the report is the entire deliverable.
Understanding the SOC 2 Attestation Model
What Is an Attestation Engagement?
An attestation engagement is a formal examination in which a practitioner evaluates subject matter prepared by another party against defined criteria, then issues a written conclusion. In SOC 2, the subject matter is your system and its controls, the criteria are the AICPA’s Trust Services Criteria (Security, Availability, Processing Integrity, Confidentiality, and Privacy), and the party preparing the subject matter is you, the service organization. Security is the only mandatory category; the other four are scoped in based on your service commitments.
The Role of the AICPA and Licensed CPA Firms
The AICPA (American Institute of Certified Public Accountants) owns the SOC framework and the attestation standards behind it, but it does not perform audits and does not issue anything to your company. Only a licensed CPA firm can conduct a SOC 2 examination and sign the resulting opinion. That licensing requirement is the quality mechanism: the firm’s professional liability, independence rules, and peer review obligations stand behind the report. In practice, this means the assurance you get is only as strong as the auditor’s reputation and independence posture, which is why enterprise buyers often look at who signed the report almost as carefully as they look at what it says.
How Attestation Differs from Certification and Accreditation
The three terms describe different assurance models.
- Certification means an accredited certification body confirms conformity with a standard and issues a certificate, as happens with ISO 27001.
- Accreditation is one level up: it is the process by which national bodies, such as those coordinated through the International Accreditation Forum, authorize those certification bodies to certify in the first place.
- Attestation involves no certificate and no accreditation chain. A CPA firm examines evidence and expresses an opinion under professional standards. The credibility comes from the auditor’s license and independence, not from a badge.
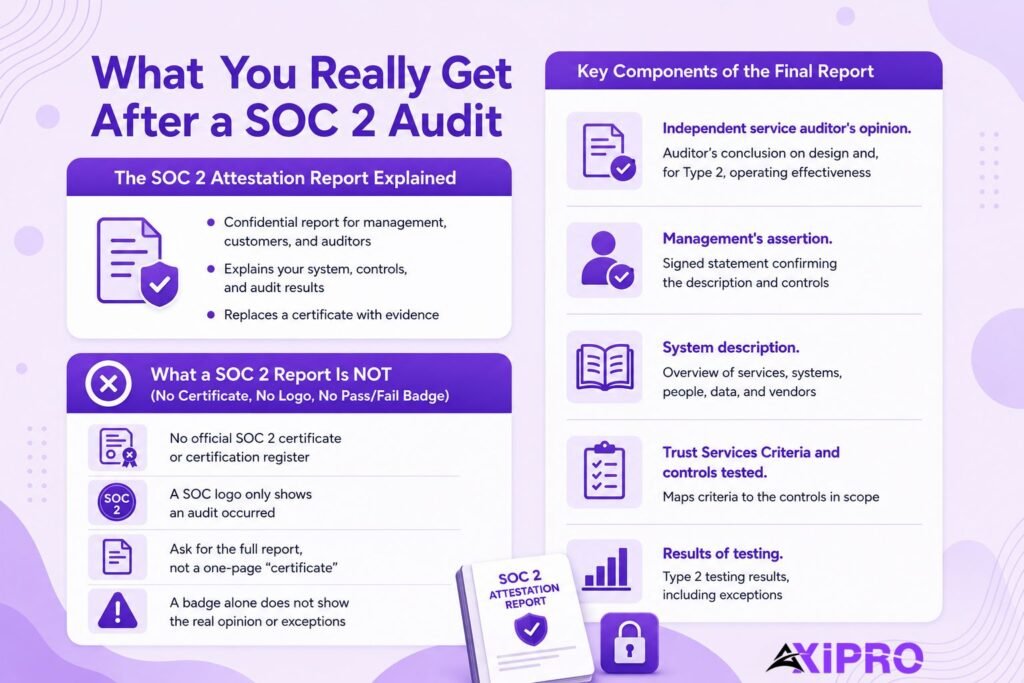
What You Actually Receive After a SOC 2 Audit
The SOC 2 Attestation Report Explained
The deliverable is a confidential, restricted-use document addressed to your management and intended for your customers, their auditors, and other informed parties. It is dense by design. A prospect’s risk team reads it to understand what your system does, which controls you operate, how the auditor tested them, and what the auditor found. It replaces a certificate with something far more useful: evidence.
Key Components of the Final Report
Independent service auditor’s opinion. The first section, usually two to three pages, states the auditor’s formal conclusion on whether your system description is fairly presented and whether your controls were suitably designed (and, for Type 2, operating effectively). This is the section report readers check first.
Management’s assertion. A signed statement in which your leadership formally asserts that the system description is accurate and that controls meet the applicable criteria. SSAE 18 made this management assertion a mandatory element, which means responsibility for the description sits with you, not the auditor.
System description. The longest narrative section was prepared by management against the AICPA’s SOC 2 description criteria. It covers the services provided, infrastructure, software, people, data, processes, subservice organizations, and complementary user entity controls.
Trust Services Criteria and controls tested. A mapping of each in-scope criterion to the specific controls you operate. This is where scoping decisions become visible: a report covering Security only looks very different from one covering all five categories.
Results of testing. For Type 2 reports, a control-by-control table showing the tests the auditor performed and the results, including any exceptions. Sophisticated readers spend most of their time here, because exceptions and the auditor’s response to them reveal more than the opinion page does.
What a SOC 2 Report Is NOT (No Certificate, No Logo, No Pass/Fail Badge)
There is no official SOC 2 certificate, no numbered credential, and no register of “certified” companies you can be listed in. The AICPA licenses a standard SOC logo that service organizations may display for a limited time after report issuance, but the logo confirms only that an examination took place. It says nothing about the opinion inside. Anyone selling you a “SOC 2 certificate” as a standalone artifact is selling something the framework does not produce.
Important: If a vendor shows you a one-page SOC 2 “certificate” during due diligence, treat it as a red flag, not a shortcut. Ask for the full report under NDA and read the opinion and the exceptions table. A certificate-style summary with no underlying report is meaningless, and a real report reduced to a badge may be hiding a qualified opinion.
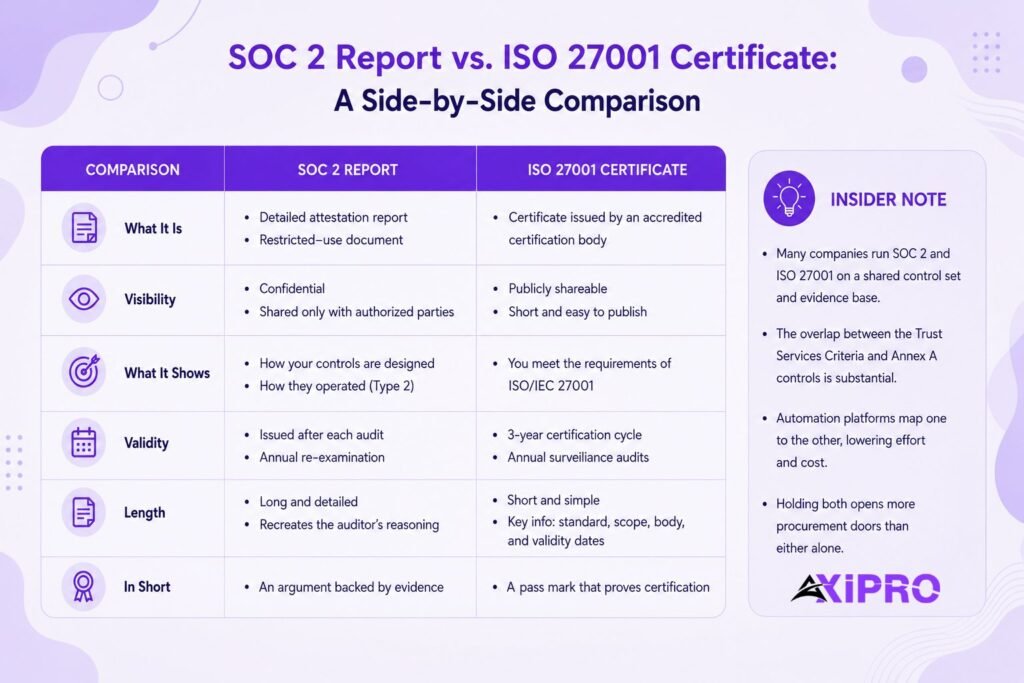
SOC 2 Report vs. ISO 27001 Certificate: A Side-by-Side Comparison
The confusion between attestation and certification usually resolves the moment you place the two deliverables side by side. ISO/IEC 27001 produces a certificate issued by an accredited certification body on a three-year cycle with annual surveillance audits. SOC 2 produces a detailed, restricted report that is reissued following a fresh examination every year. The ISO 27001 certificate is a short public document that names the standard, the scope, the certification body, and the validity dates; the SOC 2 report is a long confidential document that lets a reader recreate the auditor’s reasoning. One is a pass mark; the other is an argument.
Insider Note: Companies selling into both the US and EMEA increasingly run the two programs on a shared control set and evidence base. The overlap between the Trust Services Criteria and Annex A controls is substantial, and compliance automation platforms map one to the other. The marginal cost of the second framework is far lower than the first, and holding both closes more procurement doors than either alone.
Types of SOC 2 Reports You Can Receive
SOC 2 Type 1 Report: Point-in-Time Deliverable
A Type 1 report evaluates whether your controls were suitably designed as of a single specified date. It answers “were the right controls in place on that day,” not “did they work overtime.” Type 1 is typically a first-audit stepping stone that satisfies early customer requests while you accumulate the operating history that a Type 2 requires.
SOC 2 Type 2 Report: Period-of-Time Deliverable
A Type 2 report adds operating effectiveness: the auditor tests whether controls actually functioned throughout a defined review period, commonly three to twelve months. This is the report enterprise buyers mean when they ask for “your SOC 2.” A first Type 2 often covers a shorter window (three or six months) so the report exists sooner, with subsequent examinations settling into an annual twelve-month rhythm.
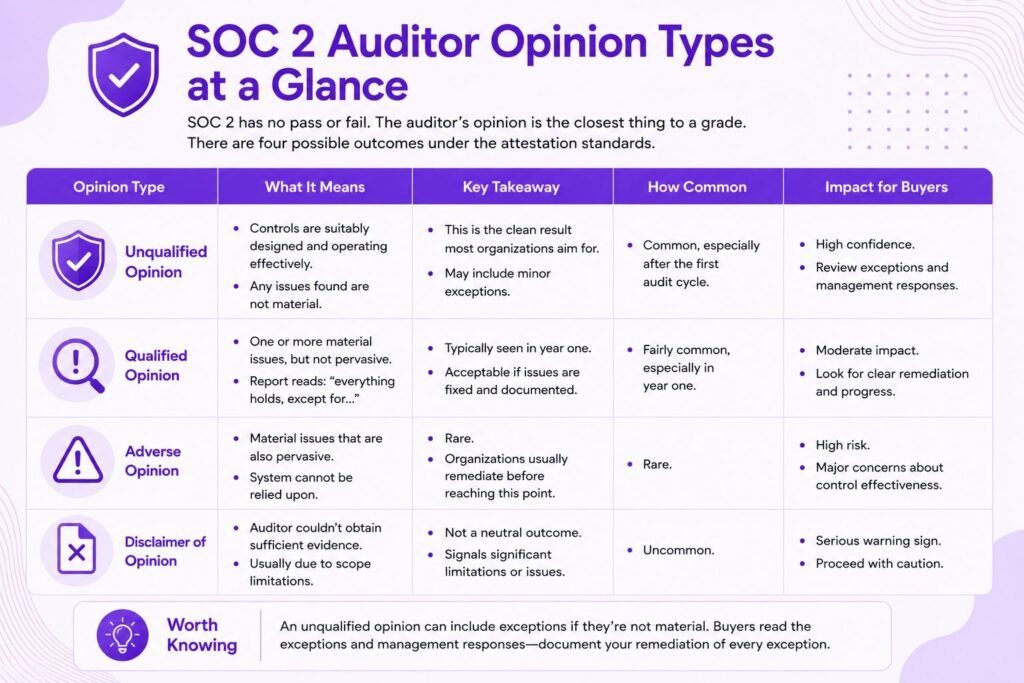
Types of Auditor Opinions in Your SOC 2 Report
Because SOC 2 has no pass or fail, the auditor’s opinion is the closest thing to a grade, and there are four possible outcomes defined under the attestation standards.
Unqualified Opinion
The clean result, and the one every service organization wants. The auditor concludes that the description is fairly presented and that controls were suitably designed and operating effectively. An unqualified opinion can still contain individual test exceptions; the auditor simply judged them immaterial to the overall conclusion, often because compensating controls held.
Qualified Opinion
The auditor found one or more material problems, but they were not pervasive. The report reads as “everything holds, except for the following.” Qualified opinions are more common than most first-timers expect, particularly in year one, and a well-remediated qualification is survivable in sales conversations if you can show what you fixed.
Adverse Opinion
Material problems that are also pervasive. The auditor is telling report readers that they cannot rely on the system as described. Adverse opinions are rare in practice because organizations heading toward one usually pause the engagement and remediate rather than take the report.
Disclaimer of Opinion
The auditor could not obtain sufficient evidence to form any opinion at all, usually because of scope limitations imposed by the organization. A disclaimer is not neutral; experienced report readers treat it as a serious warning sign.
Worth Knowing: An Unqualified Opinion
An unqualified opinion with disclosed exceptions is normal and defensible. Under the attestation standards, an exception only forces a qualification when the auditor judges the resulting misstatement material, and it only becomes adverse when material and pervasive. Savvy buyers read the exceptions table and management's responses, not just the opinion page, so document your remediation of every exception in the report itself where possible.
How to Use Your SOC 2 Report After the Audit
Sharing the Report with Customers and Prospects
The report is your primary trust asset in enterprise sales. Most organizations distribute it through a trust center or a controlled request process, gate it behind an NDA, and log who received which version. Proactively offering the report during security review shortens procurement cycles far more than any badge does.
NDA Requirements and Distribution Restrictions
SOC 2 is a restricted-use report. It contains your system architecture, control inventory, and test results, which are precisely the information you do not want circulating freely. Standard practice is to share it only under a non-disclosure agreement, either a standing mutual NDA or a click-through acknowledgment in a trust portal, and to watermark distributed copies. Given the volume of third-party breach reporting in the Verizon Data Breach Investigations Report and similar studies, treating the report as sensitive intellectual property is not paranoia; it is the same care your customers apply to yours.
Using SOC 2 Reports in Vendor Due Diligence
On the receiving side, the report is a working document for vendor risk management. Reviewers map the vendor’s in-scope criteria to their own risk requirements, check the opinion, read the exceptions, and verify the complementary user entity controls, the items the vendor’s assurance depends on you performing. A clean opinion with unimplemented user entity controls on your side still leaves you exposed.
Leveraging a SOC 3 Report for Public Marketing
If you want something you can publish, that is what SOC 3 exists for. A SOC 3 is a general-use summary derived from the same SOC 2 Type 2 examination, containing management’s assertion and the auditor’s opinion but stripped of the detailed system description and test results. You can post it on your website without an NDA, which makes it the legitimate public-facing counterpart to the restricted SOC 2 report.
How Long Your SOC 2 Report Remains Valid
The 12-Month Reporting Period
Strictly speaking, a SOC 2 report never expires; nothing in the attestation standards stamps a validity date on it. The market imposes one anyway. Buyers and their auditors treat a report as current for roughly twelve months from the end of the review period, after which they ask for a fresh one, and the AICPA limits use of its SOC logo to a defined window after issuance. The practical consequence is an annual audit cycle.
Bridge Letters Between Audit Cycles
A bridge letter (or gap letter) covers the interval between the end of your last report period and the issuance of the next report. Management, not the auditor, signs it, asserting that no material changes to the control environment occurred during the gap. Bridge letters conventionally cover no more than about three months and carry no independent assurance, so they buy time between reports rather than replacing one.
Pro Tip: Bridge Letter Template
Draft your bridge letter template before you need it, and time your review period so it ends a quarter before your customers' most common fiscal year-end. Most gap-letter fire drills happen because the report period was chosen for the auditor's convenience rather than the customers' audit calendars, and a badly timed period guarantees a bridge letter request every single year.
Why the “Certification” Language Persists in the Market
The shorthand survives because it is useful. “We are SOC 2 certified” fits on a slide; “we received an unqualified SOC 2 Type 2 attestation report” does not. Compliance vendors also optimize their content for what people actually search, which reinforces the loop. And since ISO 27001, PCI DSS, and most other frameworks genuinely are certifications, buyers pattern-match SOC 2 into the same mental category. The terminology is technically wrong but commercially sticky, and it is not going away.
How to Communicate SOC 2 Status Accurately to Stakeholders
Accurate phrasing is simple once you have it. Say your organization completed a SOC 2 Type 2 examination or received an unqualified SOC 2 Type 2 report, and name the trust services categories in scope. Avoid “certified,” “accredited,” and any invented badge. In contracts and security questionnaires, precision matters more: misdescribing an attestation as a certification in a signed document can create representations you cannot support, and general counsel teams increasingly flag this in redlines.
The Bottom Line
SOC 2 delivers a report, not a certificate: an independent CPA firm’s written opinion on your system description and controls, backed by documented testing. Understanding the attestation model tells you what to expect after the audit (an opinion, an assertion, a system description, and test results), how it differs from an ISO 27001 certificate, how long the market will treat it as current, and how to share it safely. Get the language right, and the deliverable becomes exactly what it was designed to be: the most detailed trust document your company produces.
Frequently Asked Questions
Can I say my company is "SOC 2 certified"?
You should not, strictly speaking. SOC 2 is an attestation, so the accurate phrasing is that you completed a SOC 2 examination and received a report. The shorthand is widespread and rarely challenged in casual conversation, but avoid it in contracts, questionnaires, and anything legally binding.
Is there an official SOC 2 certificate or badge?
No certificate exists. The AICPA offers a standard logo that service organizations can display for a limited period after an examination, but it confirms only that an examination occurred, not what opinion resulted.
Who issues the SOC 2 report?
A licensed CPA firm acting as the independent service auditor. The AICPA sets the standards but issues nothing to individual companies.
How often do I need to renew my SOC 2 report?
Annually, by market convention. Reports have no formal expiry, but customers treat them as stale roughly twelve months after the end of the review period, so most organizations run a continuous yearly examination cycle.
Can I fail a SOC 2 audit?
Not in the pass/fail sense. You always receive a report; the variable is the opinion inside it. A qualified, adverse, or disclaimer opinion signals problems of increasing severity, and an unqualified opinion is the outcome buyers expect.
Is a SOC 2 report public?
No. It is a restricted-use document shared under NDA with customers, prospects, and their auditors. If you need a publicly distributable version, obtain a SOC 3 report from the same examination.
What's the difference between a SOC 2 report and a SOC 2 attestation letter?
The report is the full deliverable with the opinion, system description, and test results. An attestation or bridge letter is a short management-signed summary, often used to cover the gap between audit cycles, and it carries no independent auditor assurance.