Compliance software collects the evidence. A consultant builds the system that evidence is meant to prove. That’s the real difference in the ISO 27001 consultant vs software decision, and most teams only figure it out after they’ve bought one and realized they still need the other.
Below, we compare what each route covers, where it breaks down, and what it costs you in time, money, and your team’s hours. Short version: software on its own works for a small group of companies. For most SaaS and tech scale-ups trying to get an enterprise deal over the line, consultant-led implementation on a compliance platform is the faster and safer path to a certificate.
Quick Answer: Consultant, Software, or Both?
Software-only works if you already have an in-house security lead who’s taken a company through ISO/IEC 27001 before and has the time to own the project. Consultant-only still makes sense if you run mostly on-premise or legacy systems that platforms barely integrate with. For everyone else, which means most cloud-native companies under a few hundred people, a hybrid works best: a platform to handle evidence and monitoring, and a consultant to build the management system and stand behind it in front of an auditor.
Here’s why.
Let Axipro help you build a business continuity plan that's practical, compliant, and audit-ready.
Schedule Your Free Assessment Today
What an ISO 27001 Consultant Handles
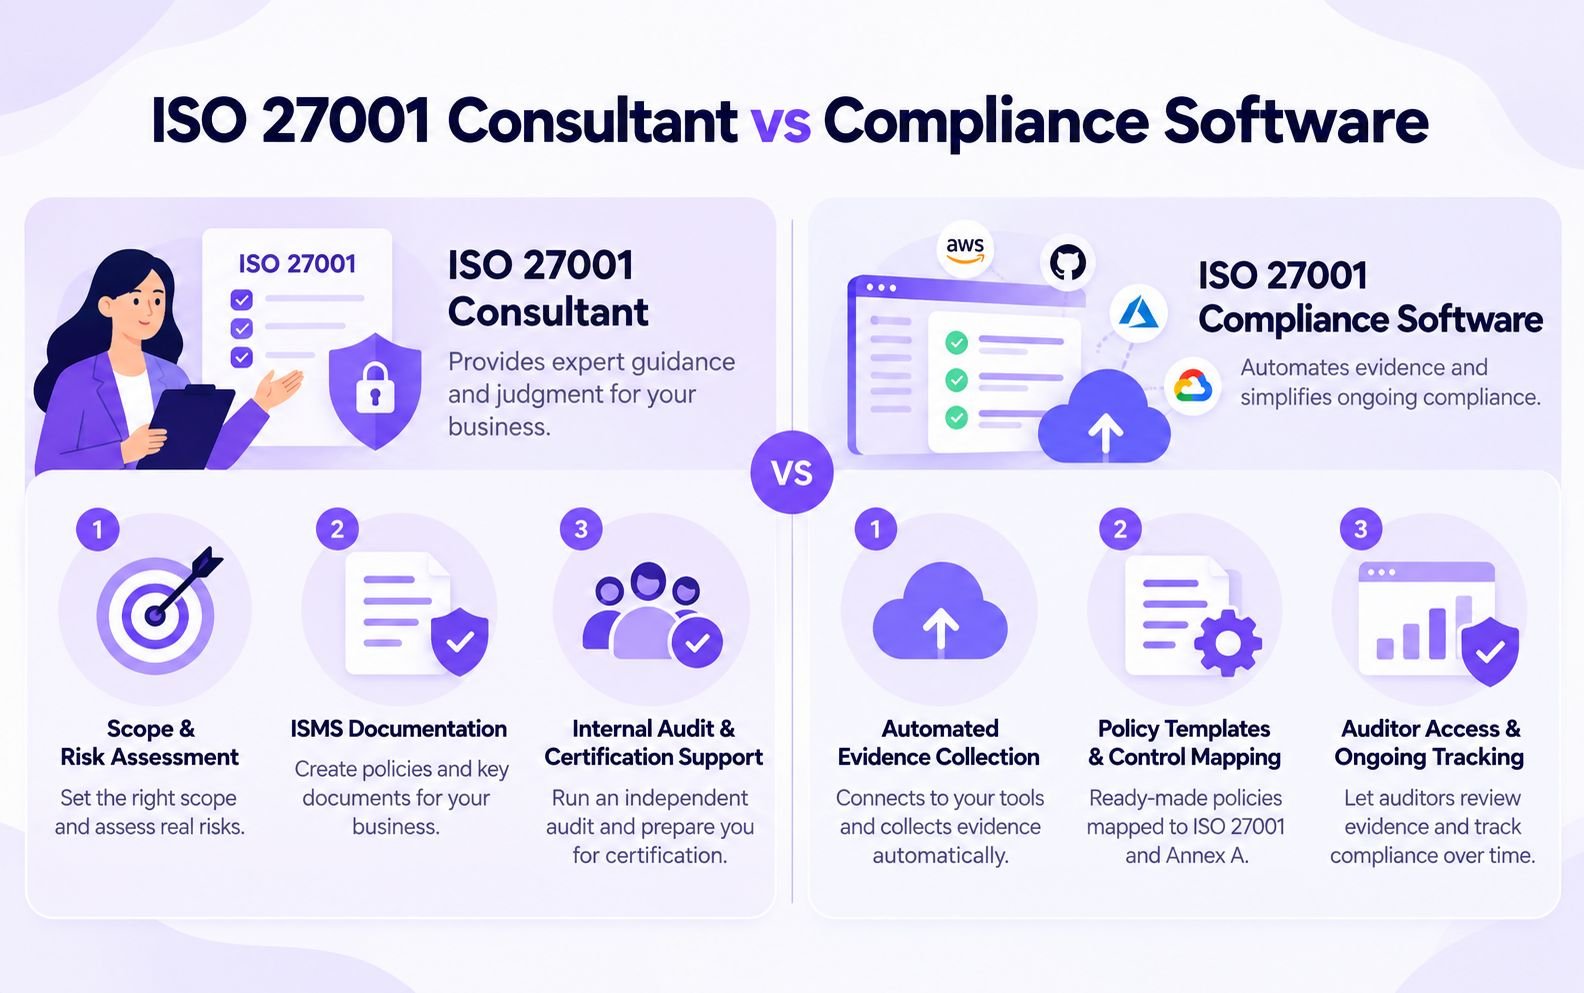
ISO/IEC 27001:2022 is a management system standard. Clauses 4 to 10 cover how you run information security, and Annex A lists 93 controls you pick from based on risk. Almost none of it is box-ticking. Most of it comes down to judgment calls about your business, and that’s what you’re paying a consultant for.
Scoping, Gap Analysis and Risk Assessment
Scope is the first decision you make, and the most expensive one to get wrong. Go too wide and you’ll spend months on controls for systems no customer asks about. Go too narrow and the certificate won’t get through the procurement review it was supposed to pass. A consultant scopes around the deals you’re trying to close, runs a gap analysis, and builds a risk assessment based on your real assets and threats. That’s the document auditors dig into hardest.
ISMS Documentation and Policy Writing
The standard asks for a specific set of documents: the ISMS scope, information security policy, risk assessment and treatment methodology, Statement of Applicability, risk treatment plan, and evidence of competence, monitoring, internal audit, and management review. A consultant writes these around how your company works day to day, instead of how a template imagines it works. Auditors check whether you follow your own procedures, so a mismatch shows up fast.
Internal Audit and Certification Audit Support
You need an internal audit before certification, and Clause 9.2 says the auditor has to be objective and impartial. In a small company, the people who built the ISMS can’t credibly audit it, so most teams outsource it through ISO 27001 internal audit services. A good consultant also gets your team ready for the Stage 1 and Stage 2 audits, joins the conversations that matter, and handles corrective actions if the auditor raises nonconformities.
What ISO 27001 Compliance Software Handles
Compliance automation platforms, often called GRC platforms, have changed how cloud-native companies get certified. They’re very good at the repetitive, evidence-heavy side of the work.
Automated Evidence Collection and Continuous Control Monitoring
The platform plugs into your cloud provider, identity provider, code repos, HR system, and device management tools, then pulls evidence on its own. It’ll flag an unencrypted storage bucket, an ex-employee who still has access, or a laptop without disk encryption. For technical controls, that saves weeks of screenshots and spreadsheet tracking.
Policy Templates and Annex A Control Mapping
Most platforms come with a policy library and map each control to the ISO 27001 clauses and Annex A. You get a starting point and a clear view of which controls have evidence and which don’t.
Auditor Access and Ongoing Compliance Tracking
Auditors can log in and review evidence themselves, which cuts down fieldwork. After you’re certified, dashboards show when controls slip between surveillance audits, so you aren’t rebuilding evidence from scratch every year.
Where Each Approach Falls Short
Neither route covers everything by itself. The good news is that the ways each one fails are predictable, so you can plan around them.
Limits of Compliance Automation Platforms
A platform can tell you a control is failing. It can’t decide your scope, run your risk assessment, write a policy that matches your operations, convince your CTO to change the offboarding process, or explain to an auditor why you excluded a control from your Statement of Applicability. Templates can also make you feel further along than you are. A dashboard at 90% can hide an ISMS that won’t survive Stage 1, because the missing 10% is the management system itself.
Insider Note: The Stage 1 problem we see most on software-only projects is a risk assessment copied straight from the platform’s default risk library. The risks are generic, the scores are almost identical, and nothing ties back to the company’s own assets. Auditors notice within minutes, and it weakens the Statement of Applicability that’s built on it.
The other problem is ownership. Software assumes someone inside the company will drive the project. At most startups that’s a CTO or ops lead who already has a full-time job, and the subscription renews whether the work gets done or not.
Limits of a Consultant-Only Approach
A consultant working without automation spends billable days on things a platform does for free, like chasing screenshots, updating evidence trackers, and collecting the same proof again before every surveillance audit. You pay more and wait longer. You also end up with a program that’s only accurate on the day it’s handed over. Once the engagement ends, the evidence goes stale and year-two surveillance turns into a scramble.
ISO 27001 Consultant vs Software: Side-by-Side Comparison
| Factor | Consultant only | Software only | Hybrid (consultant + platform) |
|---|---|---|---|
| Time to audit readiness | 3 to 6+ months | Highly variable; depends on internal expertise | As little as 6 weeks for well-scoped cloud companies |
| Cost structure | Day rates or project fees, front-loaded | Annual subscription, internal time is the hidden cost | Fixed implementation fee plus platform subscription |
| Internal team effort | Moderate | High | Low to moderate |
| Evidence quality | Strong judgment, manual evidence | Strong automated evidence, weak judgment | Strong on both |
| Ongoing maintenance | Manual, often lapses between audits | Continuous monitoring, but still needs an owner | Continuous monitoring with expert oversight |
| Adding SOC 2, ISO 42001 or GDPR | Largely re-scoped from scratch | Cross-mapped controls, but still DIY | Cross-mapped controls with guided expansion |
Time to Certification
Audit readiness and certification aren’t the same thing. You’re ready when your ISMS can pass Stage 1. The certificate comes after the Stage 1 and Stage 2 audits, and the dates depend partly on when your certification body can fit you in. Hybrid projects move fastest because the consultant handles the judgment work while the platform collects evidence at the same time.
Cost Structure: Upfront Fees vs Recurring Subscriptions
Consultant-only engagements usually run well into five figures, and Big 4 advisory firms often quote $80,000 to $150,000 or more for similar scope. Platforms rarely publish their pricing, and you pay the subscription every year. What most buyers forget to count is internal time: a software-only project can eat hundreds of hours from your most expensive engineers. You’ll pay accredited audit fees whichever route you pick. Our ISO 27001 certification cost breakdown covers each line item.
Internal Team Effort Required
Software-only puts the most on your team’s plate, because every judgment call falls to someone internal. With a hybrid setup, the consultant takes on policy writing, the risk assessment, and audit coordination, and your team handles the technical fixes and sits in on the important auditor interviews.
Audit Readiness and Evidence Quality
Auditors look at two things: whether your controls work, and whether the management system around them makes sense. Software covers the first well. Consultants cover the second. You need both to pass.
Ongoing Maintenance and Surveillance Audits
An ISO 27001 certificate runs on a three-year cycle, with surveillance audits in years two and three and recertification after that. Continuous monitoring keeps your evidence up to date, but someone still has to run management reviews, update the risk assessment, and redo the internal audit every year.
Scaling to Additional Frameworks
ISO 27001 overlaps a lot with SOC 2, ISO 42001, and GDPR. Platforms cross-map the shared controls, and a consultant who knows each framework can extend your existing ISMS instead of building a second program next to it.
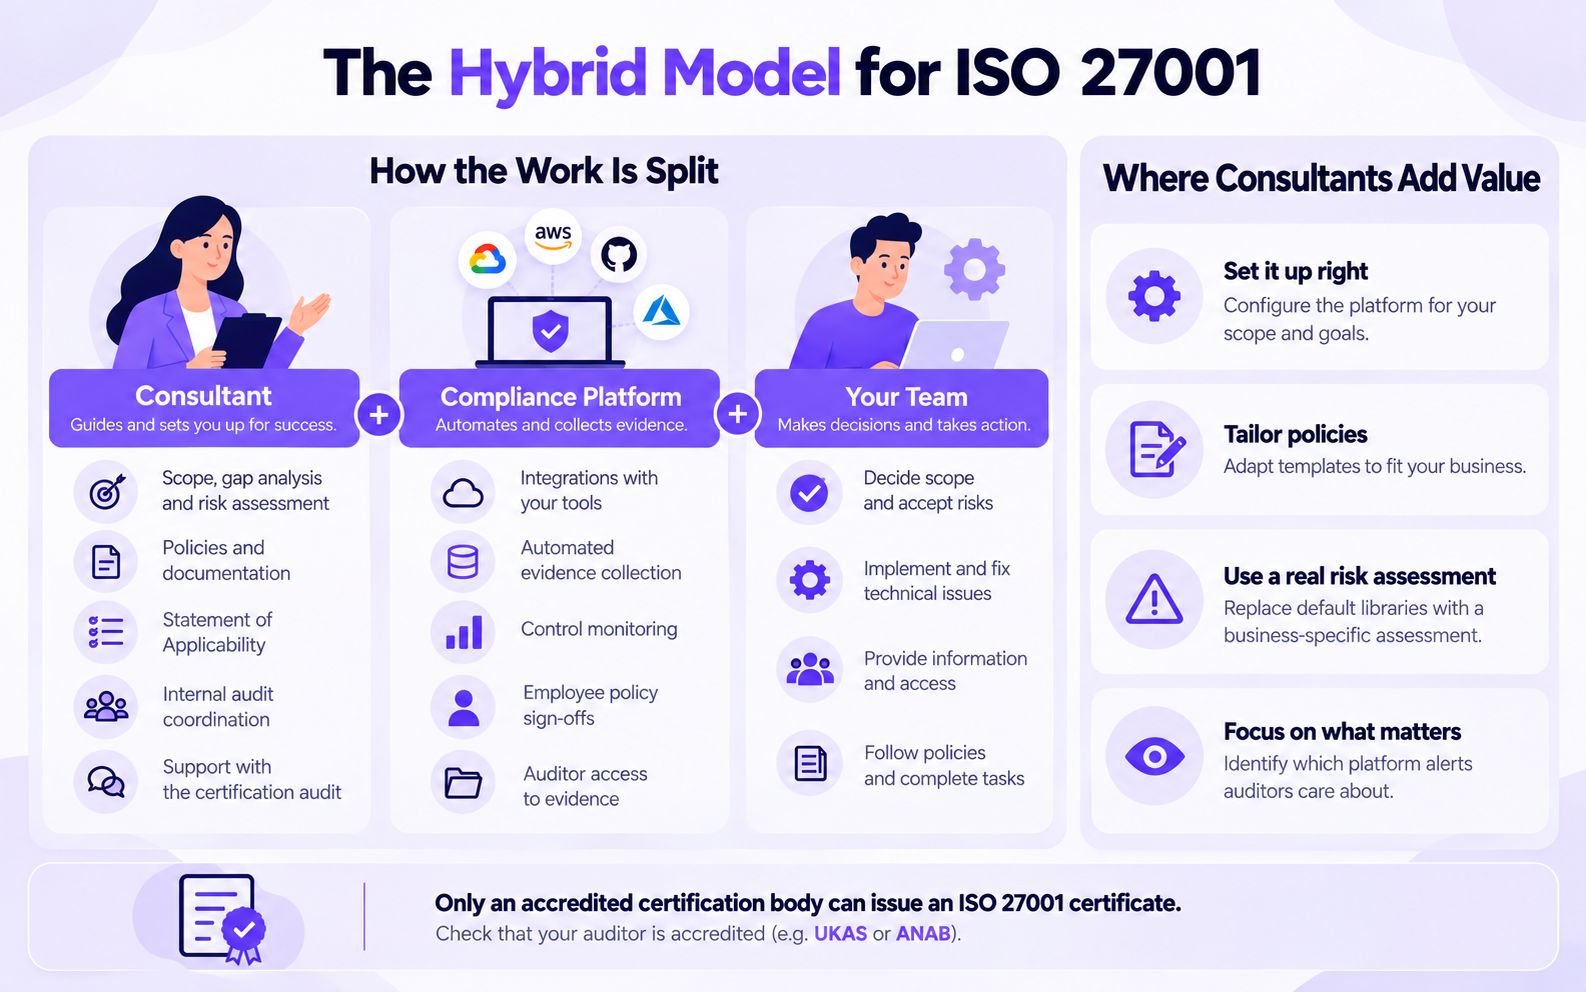
The Hybrid Model: Consultant-Led Implementation on a Compliance Platform
Think of the hybrid model as a division of labor. Each part of the work goes to whichever side does it best.
How the Work Is Split Between Consultant and Platform
The consultant owns scope, the gap analysis, the risk assessment, policies, the Statement of Applicability, internal audit coordination, and dealing with the auditor. The platform owns integrations, evidence collection, control monitoring, employee policy sign-offs, and auditor access to evidence. Your team makes the decisions and fixes the technical issues.
Where Consultants Add Value on Top of a GRC Platform
A consultant sets the platform up properly from day one. That avoids one of the most common and expensive mistakes, which is mapping controls to the wrong scope and only finding out at Stage 1. They’ll also rewrite the template policies to fit you, swap the default risk library for a real assessment, and tell you which platform warnings an auditor will care about and which ones you can ignore. If you’re still picking a tool, our comparison of Drata, Vanta and Thoropass is a good place to start.
Important: Neither a software platform nor a consultant can issue an ISO 27001 certificate. Only an accredited certification body can. Before you sign with an auditor, check that it’s accredited by a recognized body like UKAS in the UK or ANAB in the US. A certificate from an unaccredited body may not get through a customer’s security review.
How Axipro Streamlines ISO 27001 Certification
We built Axipro around the hybrid model. We’re a Drata Elite Partner, the top tier of Drata’s global partner program, and we also partner with Vanta. Since 2023, we’ve worked with more than 200 clients and kept a 100% audit success rate across 200+ certified clients. Automation handles the evidence, and a dedicated infosec team handles anything that needs judgment.
Start With a Free 30-Day Accelerator
Every engagement starts with the Compliance Accelerator Plan, 30 days of consulting at no cost. You get a gap analysis, your first policies, a tabletop exercise, and roughly 20% progress on your ISMS, so you can see real progress before you commit to anything bigger.
Implementation With Guaranteed Certification
The Achievement Plan covers the whole implementation: scoping, the risk assessment, the full documentation set, guidance across 150+ controls, vulnerability scanning, an independent internal audit, and coordination with your certification body for the external audit. You get a dedicated infosec team and a direct Slack channel, and many clients reach ISO 27001 audit readiness in as little as six weeks. The Achievement Plan comes with guaranteed certification.
Staying Certified After the Audit
The Trust Assurance Plan picks up once you have the certificate, with a vCISO, continuous monitoring, and surveillance audit prep, so year two is upkeep instead of a rebuild. You’ll find the details on our ISO 27001 certification services page.
Let Axipro help you build a business continuity plan that's practical, compliant, and audit-ready.
Schedule Your Free Assessment Today
Which Option Fits Your Organization?
Choose Software-Only If…
You have an internal security lead who’s implemented ISO 27001 before, a cloud-native stack the platform integrates with well, and no customer deadline hanging over you. In that case, a platform and solid project management can get you there, and our ISO 27001 implementation roadmap lays out the phases.
Choose a Consultant-Only Approach If…
Your environment is mostly on-premise or legacy, and platform integrations would cover very little of your scope. Expect a longer timeline, and plan now for how you’ll keep evidence current once the engagement ends.
Choose a Hybrid Approach If…
A deal is waiting on the certificate, nobody on the team has run an ISO 27001 project before, or your engineers can’t take on months of compliance work. That’s most SaaS and tech companies going for their first certificate.
Pro Tip: Ask any provider for a sample risk assessment
Ask any provider for a sample risk assessment and Statement of Applicability from a past project, with client details stripped out. It's the quickest way to tell a consultant who writes tailored ISMS documents from one who just reformats platform templates.
Questions to Ask Before You Decide
- Who on our team will own this project, and how many hours a week can they give it?
If the honest answer is “nobody” or “a few,” software-only is off the table. - When do we need the certificate, and what depends on it?
If a specific deal has a deadline, speed matters a lot more. - Which platform integrations cover our actual stack?
Check this before you buy. - Who writes the risk assessment and the Statement of Applicability?
These are the documents auditors test hardest. - What happens in year two?
Budget for the surveillance audits and the internal effort too, on top of the first certificate.
Conclusion
For most companies, the ISO 27001 consultant vs software question has a simple answer: use both, and give each one the work it’s best at. Software handles evidence and monitoring at a scale no consultant can match. The consultant handles scope, risk, documentation, and the audit itself, which is where certifications get won or lost. Go software-only if you have real in-house expertise and time, consultant-only if automation can’t reach your environment, and hybrid if you need the certificate fast and can’t afford to fail.
Frequently Asked Questions
Can you get ISO 27001 certified using software alone?
Yes, but only if someone on your team knows how to scope the ISMS, run the risk assessment, and defend it to an auditor. The software collects evidence, but it can’t make the decisions the standard requires. Certification bodies assess your management system, and they don’t care which tool you used to build it.
Is a compliance platform cheaper than an ISO 27001 consultant?
On the invoice, often yes. In total cost, not always. Software-only projects push hundreds of hours onto your own team, and without expert input they can fail Stage 1. A hybrid model with a fixed implementation fee usually works out cheaper than both day-rate consulting and going it alone.
How long does ISO 27001 take with a consultant vs with software?
Consultant-only projects usually take three to six months or more to reach audit readiness. Software-only timelines depend heavily on how much expertise you have in-house. A hybrid approach can reach readiness in as little as six weeks for well-scoped cloud companies, with certification following the Stage 1 and Stage 2 audits.
Can the consultant who implements your ISMS also perform your certification audit?
No. Under ISO/IEC 17021-1, accredited certification bodies are prohibited from offering management system consultancy, a rule the European co-operation for Accreditation reiterates in its impartiality guidance. Your consultant and your certification body have to be separate organizations, and your internal auditor shouldn’t audit controls they helped build.
Do you still need a consultant after achieving certification?
Not necessarily, but most companies are better off with some ongoing support. Surveillance audits happen every year, and you have to repeat the risk assessment, internal audit, and management review each time. A vCISO or maintenance plan keeps that on track without dragging your team back into compliance work every year.