

An AI agent that can read your inbox, query your CRM, and dig through internal documents has more standing access than most of your employees. It handles sensitive data, acts on its own, and often passes that data through sub-processors you’ll never see. Certifications are the quickest way to tell which vendors have let an outsider check their work, and which ones just put the word “secure” on a landing page.
No single certificate proves an AI agent is safe. But the right mix of security attestations, privacy certifications, and AI governance standards tells you the vendor has real controls, that an independent auditor has tested them, and that someone is on the hook when the agent misbehaves. This guide covers which certifications to ask for, how to verify them, and which claims should make you walk away.
The Core Certifications Every Secure AI Agent Vendor Should Hold
SOC 2 Type II
SOC 2 Type II is the baseline for any SaaS or AI vendor that handles customer data. A licensed CPA firm audits the vendor against the AICPA’s Trust Services Criteria (Security, Availability, Processing Integrity, Confidentiality, and Privacy) and reports on whether its controls actually worked over a review period, usually 3 to 12 months. A Type I report only confirms the controls existed on one particular day. For an AI agent vendor, insist on Type II. Anything less tells you nothing about how the company runs day-to-day.
ISO/IEC 27001
ISO/IEC 27001 certifies that the vendor runs a formal information security management system (ISMS): documented risk assessments, defined controls, internal audits, and management review, all verified by an accredited certification body. It’s the most widely recognized security certification outside the US and often a hard procurement requirement in Europe, the UK, and the Gulf. A vendor with international customers should hold it alongside SOC 2, not instead of it.
ISO/IEC 27701 (Privacy Information Management)
ISO/IEC 27701 extends ISO 27001 with a privacy information management system (PIMS). It maps closely to GDPR concepts like controller and processor obligations, consent, and data subject rights. Almost every AI agent processes personal data at scale, and ISO 27701 is a decent signal that the vendor has built privacy into how it operates instead of delegating it to a policy PDF.
ISO/IEC 42001 (AI Management Systems)
ISO/IEC 42001 is the first certifiable international standard for AI governance. According to the International Organization for Standardization, it sets out requirements for building and maintaining an AI management system (AIMS): AI risk management, AI system impact assessments, lifecycle management, and oversight of third-party suppliers. For an AI agent vendor, this is the one that covers what SOC 2 and ISO 27001 don’t: how the vendor governs model behavior, training data, and the wider impact of autonomous systems.
Worth Knowing: ISO 42001 certificates only started appearing in volume in 2024, and the accreditation ecosystem is still catching up. Check that the certificate came from a certification body accredited for ISO 42001 specifically (under ANAB or UKAS, for example), not just one accredited for ISO 27001.
HIPAA (for Healthcare AI Agents)
If the agent touches protected health information (PHI), the vendor has to comply with the HIPAA Privacy and Security Rules and sign a Business Associate Agreement (BAA). There’s no official HIPAA certification, so vendors prove compliance through third-party assessments, a SOC 2 with HIPAA mapping, or HITRUST CSF certification. A vendor that won’t sign a BAA has disqualified itself for healthcare work.
PCI DSS (for Payment-Handling AI Agents)
AI agents that process, store, or transmit cardholder data (think agents automating billing, refunds, or checkout) fall under PCI DSS. Ask for the vendor’s Attestation of Compliance (AOC) and check whether a Qualified Security Assessor validated it or the vendor assessed itself. The current version is PCI DSS 4.x, so an AOC that still references 3.2.1 is out of date.
FedRAMP (for Government-Facing AI Agents)
FedRAMP authorization is mandatory for cloud services sold to US federal agencies. Authorizations come at Low, Moderate, and High impact levels, and every authorized service appears on the public FedRAMP Marketplace. If a vendor claims FedRAMP status and isn’t in the Marketplace, either the claim is false or the service is still “in process,” and those are very different things. State and local buyers should look for StateRAMP instead.
Worth Knowing: ISO 42001 Certificates
ISO 42001 certificates only started appearing in volume in 2024, and the accreditation ecosystem is still catching up. Check that the certificate came from a certification body accredited for ISO 42001 specifically (under ANAB or UKAS, for example), not just one accredited for ISO 27001.
HIPAA (for Healthcare AI Agents)
If the agent touches protected health information (PHI), the vendor has to comply with the HIPAA Privacy and Security Rules and sign a Business Associate Agreement (BAA). There’s no official HIPAA certification, so vendors prove compliance through third-party assessments, a SOC 2 with HIPAA mapping, or HITRUST CSF certification. A vendor that won’t sign a BAA has disqualified itself for healthcare work.
PCI DSS (for Payment-Handling AI Agents)
AI agents that process, store, or transmit cardholder data (think agents automating billing, refunds, or checkout) fall under PCI DSS. Ask for the vendor’s Attestation of Compliance (AOC) and check whether a Qualified Security Assessor validated it or the vendor assessed itself. The current version is PCI DSS 4.x, so an AOC that still references 3.2.1 is out of date.
FedRAMP (for Government-Facing AI Agents)
FedRAMP authorization is mandatory for cloud services sold to US federal agencies. Authorizations come at Low, Moderate, and High impact levels, and every authorized service appears on the public FedRAMP Marketplace. If a vendor claims FedRAMP status and isn’t in the Marketplace, either the claim is false or the service is still “in process,” and those are very different things. State and local buyers should look for StateRAMP instead.
Regulatory Frameworks AI Agent Vendors Must Comply With
Certifications are voluntary. Regulations aren’t. A credible AI agent vendor should be able to explain, in writing, how it meets each of the following.
GDPR (EU Data Protection)
Any agent processing personal data of people in the EU falls under GDPR, no matter where the vendor is based. Expect a signed Data Processing Agreement (DPA), a published sub-processor list, data residency options, and a working mechanism for the right to erasure. Erasure is genuinely hard for AI vendors, so ask specifically whether customer data ends up in model training and how deletion requests reach backups and fine-tuned models.
CCPA/CPRA (California Privacy)
The CCPA, as amended by the CPRA, gives California residents the right to access, delete, and opt out of the sale or sharing of their personal information. Vendors with US customers should have a service provider agreement covering CCPA obligations and be able to handle consumer rights requests within the statutory timelines.
The EU AI Act
The EU AI Act entered into force in August 2024 and applies in phases: prohibitions kicked in from February 2025, obligations for general-purpose AI models followed in August 2025, and the high-risk requirements are phasing in from 2026 onward, with some deadlines moved by the 2026 Digital Omnibus package. Two questions for any vendor. Has it classified its agent under the Act’s risk tiers, and can it show you the analysis? And if the agent gets used in a high-risk context like employment or credit decisions, what’s the plan for conformity assessment and technical documentation? A vendor that’s never heard of Annex III isn’t ready to sell into Europe.
NIST AI Risk Management Framework (AI RMF)
The NIST AI Risk Management Framework is voluntary, but it’s become the shared vocabulary for AI risk in the US. Its four functions (Govern, Map, Measure, and Manage) give you a structured way to question a vendor’s AI risk program, and NIST’s Generative AI Profile extends it to generative-specific risks. Vendors who can map their controls to the AI RMF usually have a real program behind the claims. The ones who can’t are usually improvising.
SOC 2 vs ISO 27001: Key Differences for AI Agent Buyers
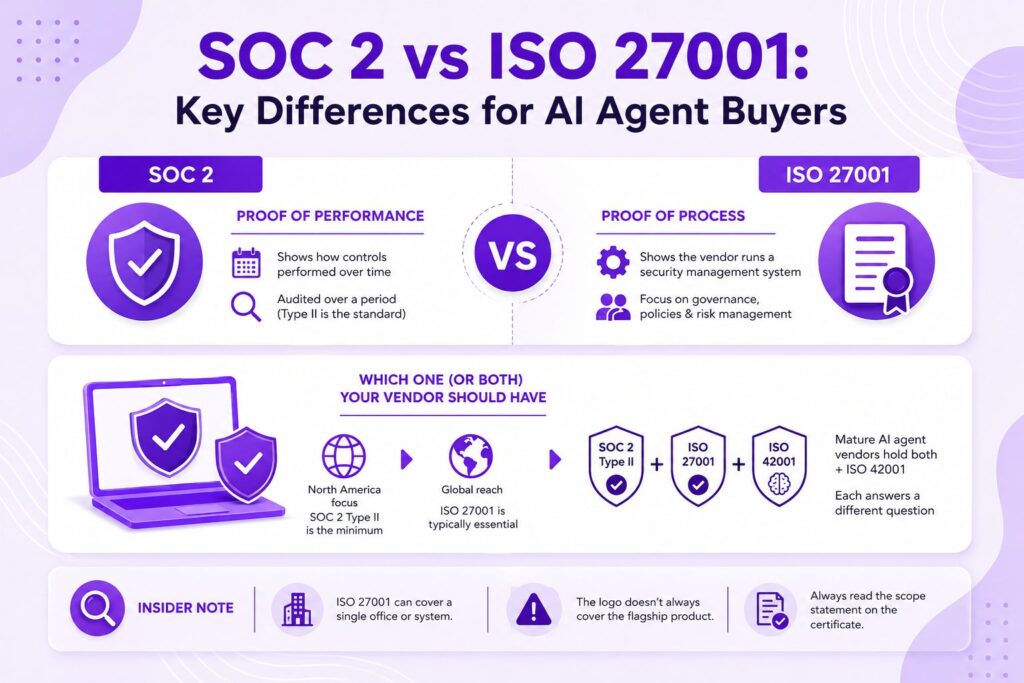
Buyers ask about these two more than anything else. The short answer: they solve different problems. SOC 2 shows you how controls actually performed over a period. ISO 27001 shows that the vendor runs a certified management system for security. For a full breakdown of how the two frameworks map to each other, see our guide to the key differences.
Which One (or Both) Your Vendor Should Have
For a vendor selling mainly into North America, SOC 2 Type II is the minimum. For one selling internationally, ISO 27001 usually isn’t optional either. Mature AI agent vendors increasingly hold both, plus ISO 42001, because each answers a different question: did the controls work, is there a disciplined security management system, and is anyone actually governing the AI. If budget forces the vendor to pick one first, what matters most to you as the buyer is that the chosen framework’s scope covers the agent product you’re buying.
Insider Note: An ISO 27001 certificate can legitimately cover a scope as narrow as one office or one internal system. Auditors regularly see vendors advertise the logo while the certified scope leaves out the flagship product entirely. Always read the scope statement on the certificate itself, not the badge on the website.
AI-Specific Certifications and Emerging Standards
ISO/IEC 42001 for AI Governance
ISO 42001 is currently the only certifiable AI governance standard, which makes it the strongest single differentiator among AI agent vendors. It also sets vendors up well for regulation: an AI management system built on 42001 covers much of the organizational groundwork the EU AI Act will demand, even though the certification itself doesn’t create a presumption of conformity with the Act.
ISO/IEC 23894 for AI Risk Management
ISO/IEC 23894 gives guidance on managing AI-specific risks across the system lifecycle, building on the general risk principles of ISO 31000. It’s a guidance standard, not a certifiable one, so treat any vendor claim of “ISO 23894 certification” as a red flag in itself. The correct claim is alignment. The right follow-up is to ask how the vendor identifies and treats AI risk sources like model drift, bias, and adversarial manipulation.
NIST AI RMF Alignment
Like ISO 23894, the NIST AI RMF isn’t certifiable. What you want from a vendor is a documented mapping: which controls implement Govern, Map, Measure, and Manage, and which artifacts back them up (model cards, evaluation reports, incident response runbooks, an AI Bill of Materials). That’s the point where model governance claims become checkable instead of decorative.
Industry-Specific Certification Requirements
Healthcare AI Agents (HIPAA, HITRUST)
Beyond HIPAA compliance and a signed BAA, many health systems require HITRUST CSF certification because it rolls HIPAA, NIST, and ISO requirements into one assessable framework with defined assurance levels. HITRUST has also added AI-specific assessment content, which makes it increasingly relevant for clinical AI agents.
Financial Services AI Agents (PCI DSS, SOX)
Agents touching cardholder data need PCI DSS validation, as covered above. Agents that feed financial reporting at public companies also run into SOX internal controls, so expect your auditors to ask for the vendor’s SOC reports and change-management evidence. Most financial institutions will run their own third-party risk assessment on top of whatever certifications the vendor holds.
Public Sector AI Agents (FedRAMP, StateRAMP)
US federal deployments need FedRAMP authorization at the impact level matching the data involved; most business data lands at Moderate. StateRAMP extends similar assurance to state and local government. Both come with continuous monitoring obligations, which work in your favor: the authorization stays under ongoing oversight rather than sitting there as a point-in-time stamp.
How to Verify a Vendor’s Certifications Are Legitimate
Requesting the SOC 2 Report vs. Attestation Letter
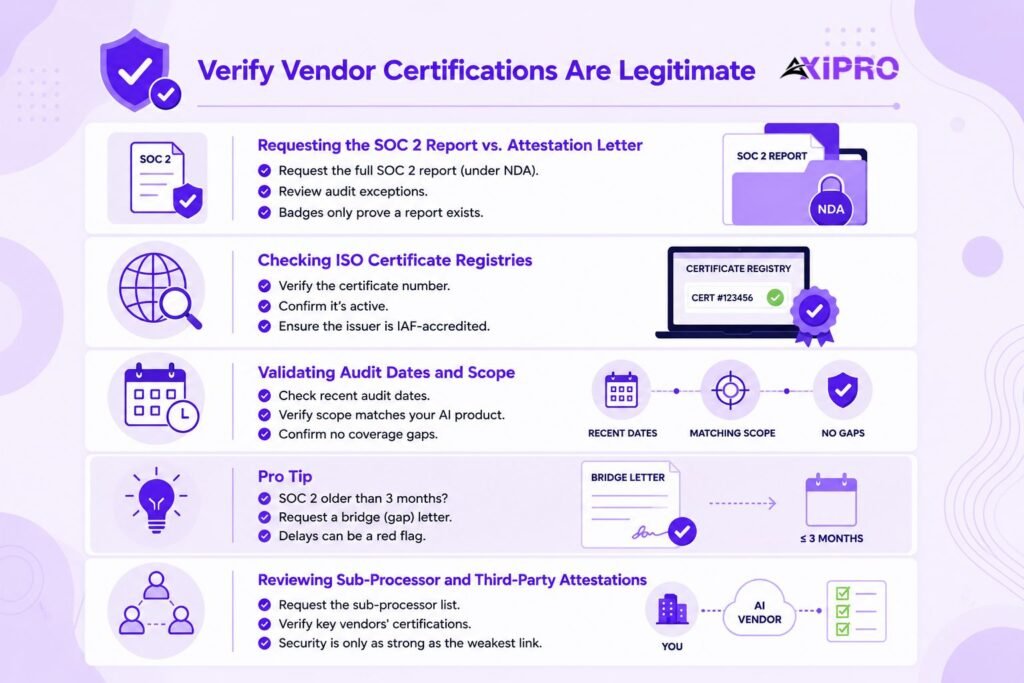
An attestation letter or a Trust Center badge only tells you a report exists. The full SOC 2 report, shared under NDA, contains the audit period, the system description, the criteria covered, the auditor’s tests, and any exceptions the auditor found. Read the exceptions and the vendor’s responses. A report with a few well-remediated exceptions is often more trustworthy than a suspiciously spotless one.
Checking ISO Certificate Registries
ISO itself doesn’t certify anyone. Certificates come from accredited certification bodies, and most of them run public verification portals where you can look up a certificate number. Confirm the certificate is current, names the right legal entity, and was issued by a body accredited by a recognized member of the International Accreditation Forum (IAF).
Validating Audit Dates and Scope
For SOC 2, check that the audit period is recent and continuous; any gap between the last report’s end date and today is uncovered time. For ISO certificates, check both the issue date and the expiry of the three-year cycle, and confirm the surveillance audits are actually happening. In every case, verify the scope covers the specific AI agent product, region, and infrastructure you’ll actually use.
Reviewing Sub-Processor and Third-Party Attestations
An AI agent vendor is usually a wrapper around other people’s infrastructure: foundation model APIs, cloud hosting, vector databases, observability tools. Request the sub-processor list and confirm the critical ones hold their own SOC 2 or ISO 27001 attestations. Your risk is the weakest link in that chain, and vendor risk management that stops at the first-party vendor misses most of the attack surface.
Pro Tip: SOC 2 Report
If a SOC 2 report period ended more than three months ago, ask for a bridge letter (also called a gap letter). It's a standard document where management confirms nothing material changed in the controls since the audit period ended. Established vendors produce one within days. Vendors who've never heard of it deserve extra scrutiny.
Red Flags: Certification Claims to Watch Out For
Expired or Out-of-Scope Reports
A SOC 2 report from two audit cycles ago, an ISO certificate past its surveillance date, or a certificate scoped to a product you aren’t buying: all of these fail verification. So does a report that only covers the corporate IT environment while the AI agent runs on separate, unaudited infrastructure.
Self-Attestations vs. Independent Audits
Security questionnaires, internal whitepapers, and “compliant with ISO 27001 principles” language are self-attestations. They have a place in due diligence, but they don’t replace an independent auditor’s opinion. The same goes for AI claims: “built with responsible AI principles” is marketing until an ISO 42001 certificate or an audited framework mapping backs it up.
Important: Watch for logo laundering: vendors displaying the AICPA SOC badge, an ISO logo, or a partner’s FedRAMP status as if it were their own. A common variant is pointing to the cloud provider’s certifications (AWS or Azure) as proof of the vendor’s own compliance. Infrastructure certifications don’t cover the vendor’s application, code, or personnel.
Certification Checklist for Evaluating AI Agent Vendors
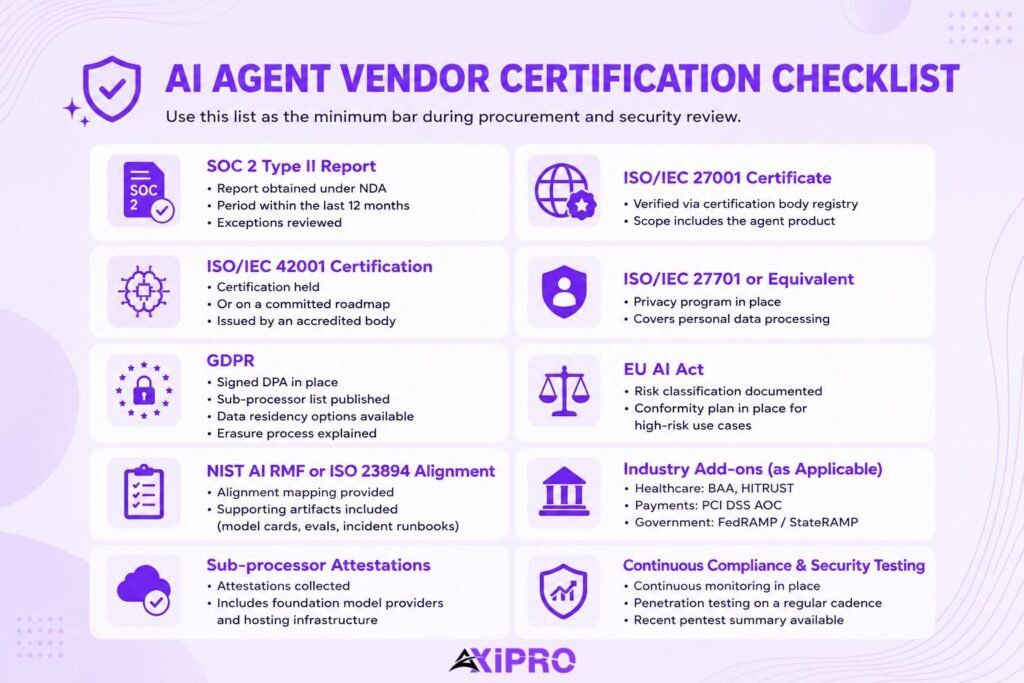
Use this list as a minimum bar during procurement and security review:
- SOC 2 Type II report obtained under NDA, period ending within the last 12 months, exceptions reviewed
- ISO/IEC 27001 certificate verified via the certification body’s registry, scope covers the agent product
- ISO/IEC 42001 certification held or on a committed roadmap, issued by an accredited body
- ISO/IEC 27701 or an equivalent, documented privacy program for personal data processing
- GDPR: signed DPA, published sub-processor list, data residency options, erasure mechanics explained
- EU AI Act risk classification documented; conformity plan exists if high-risk use is possible
- NIST AI RMF or ISO 23894 alignment mapping with supporting artifacts (model cards, evals, incident runbooks)
- Industry add-ons where relevant: BAA and HITRUST for healthcare, PCI DSS AOC for payments, FedRAMP/StateRAMP for government
- Sub-processor attestations collected for foundation model providers and hosting infrastructure
- Continuous compliance monitoring and penetration testing cadence confirmed, with a recent pentest summary available
The Bottom Line
Certifications won’t tell you whether an AI agent hallucinates, but they will tell you whether the company behind it takes controls and accountability seriously. Require SOC 2 Type II and ISO 27001 as the security floor, treat ISO 42001 as the emerging differentiator for AI governance, add HIPAA, PCI DSS, or FedRAMP where your industry demands it, and verify everything against primary sources: the full report, the certificate registry, the FedRAMP Marketplace. Vendors with real programs make verification easy. Vendors without them make it awkward, and that awkwardness is your answer.
Frequently Asked Questions
Is SOC 2 Type II enough for an AI agent vendor?
Necessary, but not sufficient. SOC 2 covers security, availability, and related criteria for the service organization. It wasn’t designed to assess AI-specific risks like model behavior, training data governance, or algorithmic bias. Pair it with ISO 42001 certification or a documented NIST AI RMF mapping.
Do AI agent vendors need both SOC 2 and ISO 27001?
Vendors selling internationally generally need both. US buyers ask for SOC 2; buyers in Europe, the UK, and the Gulf expect ISO 27001. The two overlap heavily in control substance, so a vendor with one can usually reach the other with moderate extra effort.
Does SOC 2 cover AI-specific risks like model drift or hallucinations?
No. The Trust Services Criteria cover organizational and system controls, not model quality. Model drift, hallucination rates, and bias need AI-specific governance: ISO 42001, ISO 23894 alignment, evaluation reports, and ongoing monitoring.
How often should vendor certifications be renewed?
SOC 2 Type II reports are reissued every year with a new audit period. ISO certificates run on a three-year cycle with annual surveillance audits. PCI DSS attestations are annual. FedRAMP requires continuous monitoring with annual assessments. Anything older than its cycle should be treated as lapsed.
What certifications are required for AI agents processing EU data?
GDPR compliance is the legal requirement, usually evidenced through a DPA, transfer mechanisms, and processor obligations, and the EU AI Act adds obligations based on the system’s risk classification. ISO 27001, ISO 27701, and ISO 42001 aren’t legally required, but they’re the certifications European buyers most often accept as evidence that the legal obligations are actually being met.
Is ISO 42001 replacing SOC 2 for AI vendors?
No. They answer different questions, and buyers increasingly expect both. SOC 2 attests that operational security controls worked over a period; ISO 42001 certifies a management system for governing AI responsibly. Expect ISO 42001 to become a standard line item in AI vendor questionnaires alongside SOC 2, not in place of it.


