

Most security certifications were built for software that follows rules. AI agents do not. They consume data, draw conclusions, call tools, and take action, increasingly without a human in the loop.
That gap is what AIUC-1 was created to close: it is the first auditable security standard built specifically for AI agents, and a few enterprise buyers have started asking vendors for it by name.
This guide covers what AIUC-1 actually tests, the six risk domains it audits, how the certification process works, what it costs, how long it lasts, and how it aligns with SOC 2, ISO 42001, ISO 27001, and the NIST AI Risk Management Framework. It also covers the structural questions worth asking before you treat an AIUC-1 report as proof of anything.
What Is AIUC-1 Certification?
AIUC-1 is a certifiable standard for AI agents created by the Artificial Intelligence Underwriting Company (AIUC), a San Francisco-based, venture-backed startup founded by people with experience at organizations including Anthropic. The standard was developed with input from Orrick, Stanford, the Cloud Security Alliance, MIT, and MITRE, and launched in mid-2025.
The framework comprises 51 requirements and 130 controls, organized across six risk pillars. It evaluates whether an organization has implemented and tested the technical guardrails, operational practices, and legal policies needed to reduce the risk of unsafe, unreliable, or unauthorized AI behavior. Certification applies to a specific AI system or product, not to the organization as a whole. An AIUC-1 certificate, audit report, and badge tell enterprise buyers that an agent has been independently tested against agent-specific risks.
People describe AIUC-1 as the “SOC 2 for AI agents,” and the analogy holds in spirit. The difference is what it looks at. SOC 2 examines a service organization’s general controls. AIUC-1 examines how an agent behaves under pressure: when someone tries to jailbreak it, when it is asked to do something outside its scope, when it has access to data it should not expose.
Worth Knowing: About AIUC-1
AIUC-1 does not define what counts as an "AI agent." The vendor decides which system to certify and what falls in scope. That makes scope the single most important thing to check on any certificate, because a narrowly scoped audit may not cover the agent you actually use.
Why AIUC-1 Certification Matters for Enterprise AI Adoption
The business case rests on a simple problem: enterprises cannot reliably assess the security of their AI vendors, and the failures are expensive. According to EY research on responsible AI, 64% of companies with over $1 billion in revenue have already lost more than $1 million to AI-related failures.
That gap shows up directly in sales cycles. When security, legal, and procurement teams evaluate an AI vendor, they ask about hallucinations, prompt injection defenses, and what happens when an agent makes an unauthorized call. SOC 2 and ISO 27001 do not answer those questions. AIUC-1 gives buyers a structured, third-party-tested answer, which is why holding the certificate can move a stalled procurement review forward.
The certification also produces real engineering outcomes, not just a badge. AIUC has reported cases where a customer service agent’s hallucination rate dropped from 11% to under 2% after strengthening its groundedness filter, and another where inappropriate-tone outputs fell from 9% to under 2% through better defensive prompting and output moderation. One company found and patched a PII exposure vulnerability during the certification process itself.
The Six Core Risk Domains Covered by AIUC-1
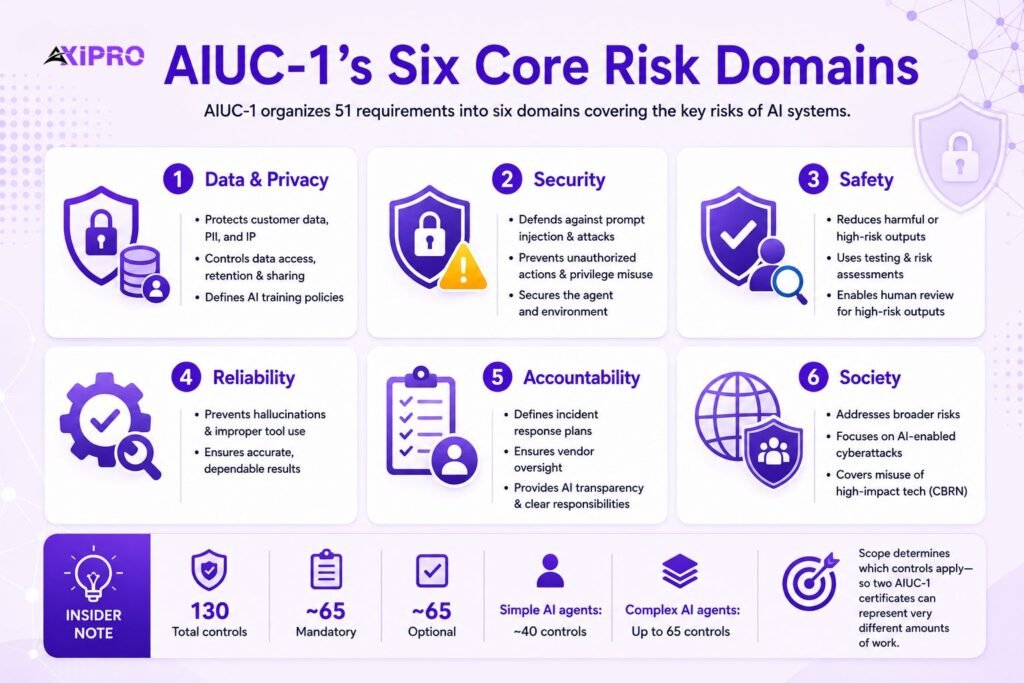
AIUC-1’s 51 requirements are grouped into six domains. Each targets a category of risk that traditional security frameworks were not designed to handle.
Data and Privacy
Covers how customer data is used, retained, and protected. Requirements address input and output data policies, limits on what data the agent can access, protection of IP and trade secrets, prevention of cross-customer data exposure, and prevention of PII leakage. This is where the standard forces clarity on whether customer data trains the model and how long it is kept.
Security
The adversarial-resistance domain. It covers third-party testing of adversarial robustness, detection and real-time filtering of malicious inputs, prevention of prompt injection and unauthorized agent actions, enforcement of user access privileges, and protection of the deployment environment. This is the heart of what separates an agent audit from a general security audit.
Safety
Focuses on preventing harmful and out-of-scope outputs. Requirements include defining an AI risk taxonomy, conducting pre-deployment testing, preventing harmful and customer-defined high-risk outputs, and flagging high-risk outputs for human review. Safety is partly judgment-based, which means documentation alone can sometimes satisfy a requirement, so the testing behind it deserves scrutiny.
Reliability
Targets the failure modes that erode trust in production: hallucinations and tool misuse. Controls cover hallucination prevention and restrictions on which tools an agent can call and when. For a customer-facing agent, this is the domain that keeps it from inventing a refund policy or triggering the wrong workflow.
Accountability
Covers what happens when things go wrong. Requirements include AI failure response plans, vendor due diligence, and clear AI disclosure so users know when they are interacting with an agent. With human workers, accountability is built into org charts and chains of command. Agents need an equivalent, and this domain supplies it.
Society
The broadest domain, focused on preventing misuse with wider consequences: AI-enabled cyber attacks and CBRN (chemical, biological, radiological, nuclear) misuse. Most enterprise agents will touch only a few of these controls, but they matter for higher-capability systems.
Insider Note: Of the 130 total controls, roughly 65 are mandatory, and 65 are optional. A straightforward agent typically needs to meet around 40 controls. A complex, multi-modal agent gets closer to 65. The scoping exercise determines which apply, so two AIUC-1 certificates can represent very different amounts of work.
Who Needs AIUC-1 Certification?
AIUC-1 is built for any company developing or deploying agentic AI that sells into enterprises. The strongest fit is an organization whose product uses AI agents in customer-facing operations, handles confidential data through autonomous workflows, or makes decisions that affect critical business processes.
Certified systems so far include customer service agents, candidate scoring and interviewer agents, internal automation agents, summarization agents, and image generation agents. Certified organizations range from seed-stage startups to publicly traded enterprises, so company size is not the gating factor. Buyer demand is. The clearest reason to pursue AIUC-1 is that your enterprise buyers are asking for it, though early adoption also lets a vendor shape the security conversation before competitors do.
How the AIUC-1 Certification Process Works
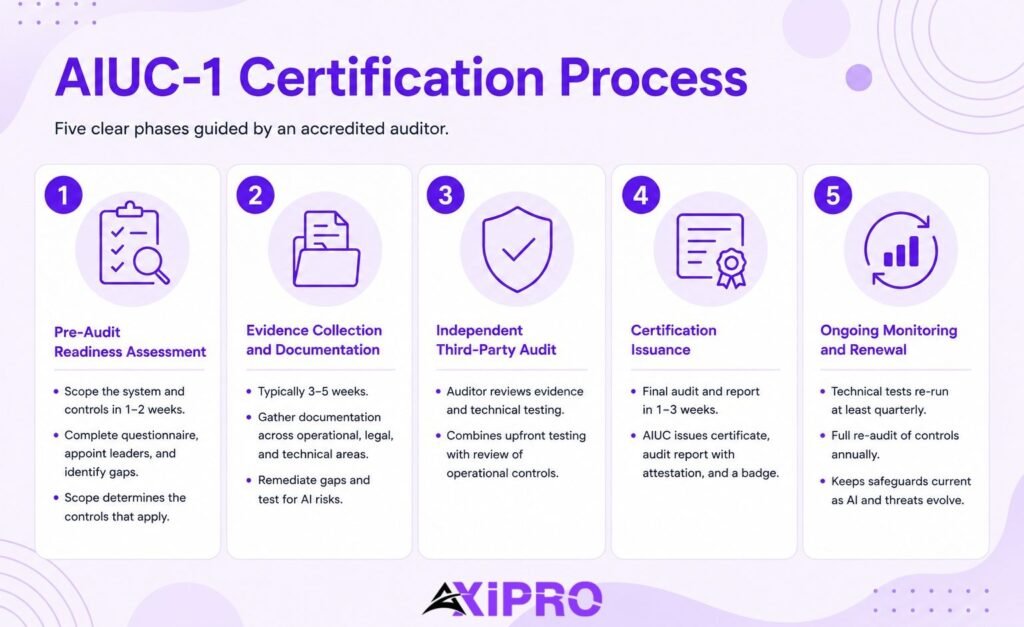
The certification runs in distinct phases, with an accredited auditor guiding the organization through evidence collection and gap remediation.
Pre-Audit Readiness Assessment
Scoping and kickoff usually take one to two weeks. The organization works with the auditor to complete a scoping questionnaire, define which system and which controls are in scope, appoint internal leaders, and identify where current practices fall short of AIUC-1’s requirements. An internal-facing agent with limited data access will scope into far fewer controls than an external customer service agent handling sensitive data.
Evidence Collection and Documentation
The bulk of the work, typically three to five weeks. Teams gather documentation across operational practices, legal policies, and technical implementations, then remediate gaps surfaced during scoping. This phase includes hands-on testing of the system for hallucinations, prompt injection resistance, and the other risks the standard covers.
Independent Third-Party Audit
An accredited auditor reviews the evidence, conducts or reviews technical testing, and assembles the report. The audit combines upfront technical testing with a review of operational controls.
Certification Issuance
The Artificial Intelligence Underwriting Company issues the certificate. Finalizing the audit, building the report, and obtaining sign-off generally takes one to three weeks. The deliverables are the certificate, a detailed audit report with third-party attestation and evaluation results, and a badge for use in a trust center or sales collateral.
Ongoing Monitoring and Renewal
Certification is not a one-time event. Technical tests are re-run at least quarterly, and the full set of technical, operational, and legal controls is re-audited annually. This continuous cadence is meant to keep safeguards current as both AI capabilities and attack techniques evolve.
Requirements for AIUC-1 Certification
There is no single checklist that applies to every applicant, because scope drives requirements. Every certification covers the mandatory controls relevant to the system, plus whichever optional controls the agent’s data access, autonomy, and modality bring into scope.
In practice, organizations need documented input and output data policies, demonstrated defenses against prompt injection and unauthorized actions, evidence of pre-deployment and adversarial testing, a defined risk taxonomy, failure response plans, and clear disclosure practices. Where there is no single industry best practice, such as data retention, the standard emphasizes clear disclosure and enforcement over mandating one specific approach.
How Long Does AIUC-1 Certification Take?
AIUC lists a typical timeline of four to eight weeks, depending on the maturity of the organization’s existing safeguards and governance. Its FAQ gives a slightly wider range of five to ten weeks. Organizations that already have AI governance in place, for example an ISO 42001 management system, tend to land at the faster end because much of the operational and legal groundwork already exists.
How Much Does AIUC-1 Certification Cost?
AIUC does not publish standard pricing, and any firm quote depends on scope, the number of controls in play, the agent’s complexity, and the auditor engaged. Cost is driven by the same factors as the timeline: a simple internal agent scoping into roughly 40 controls is a smaller engagement than a complex multi-modal agent scoping into 65, with the adversarial testing that entails.
Treat published figures from third parties with caution and get a scoped quote from an accredited auditor. As a directional anchor, AIUC-1 sits in the same tier as other independent technical audits rather than a self-attestation, so budget alongside what you would expect for a SOC 2 Type II or ISO 42001 audit, plus the cost of any remediation the readiness phase surfaces.
Pro Tip: Run a Gap Assessment
Run a gap assessment before you commit to a full audit. The readiness phase is where most of the real cost hides, because remediation work, not the audit fee, is usually the larger line item. Knowing your gaps first lets you budget accurately and avoid a stalled audit halfway through evidence collection.
How Long Is an AIUC-1 Certificate Valid?
An AIUC-1 certificate is valid for twelve months. Maintaining it requires technical testing at least every three months. Miss the quarterly cadence and the certificate lapses, even inside the twelve-month window. New requirements introduced through quarterly updates are evaluated at the next annual re-audit, so the certificate you hold reflects the version of the standard in force when you were audited.
Who Can Issue an Official AIUC-1 Certificate?
The Artificial Intelligence Underwriting Company issues all certificates. Schellman was the first accredited auditor for the standard, and accredited auditors handle evidence collection and prepare the reports. The ongoing quarterly technical evaluations are run centrally by AIUC itself rather than by individual auditors, which the company says keeps testing consistent across all certified organizations.
This structure matters for how much weight a certificate carries, a point covered in the challenges section below.
AIUC-1 Certification vs. Other Frameworks
AIUC-1 is designed to complement existing frameworks, not replace them. It operationalizes the AI-specific frameworks and avoids duplicating the general-purpose ones.
Framework | What it covers | Certifiable? | AI-agent specific? | Relationship to AIUC-1 |
|---|---|---|---|---|
AIUC-1 | Technical, operational, and legal controls for AI agent risk | Yes | Yes | The standard itself |
SOC 2 | General service organization security controls | Attestation | No | Coexists; still required for enterprise sales |
ISO 42001 | AI management system (governance and process) | Yes | Partly | AIUC-1 validates that the governance produces working controls |
ISO 27001 | Information security management system | Yes | No | Foundational security; AIUC-1 sits on top |
NIST AI RMF | Voluntary AI risk-management guidance | No | Partly | AIUC-1 translates its functions into testable controls |
AIUC-1 vs. SOC 2
SOC 2 covers a vendor’s general cybersecurity posture. It does not address hallucinations, prompt injection, or unauthorized tool calls. The two are complementary: SOC 2 remains table stakes for selling into enterprise, while AIUC-1 answers the AI-specific questions SOC 2 leaves open.
AIUC-1 vs. ISO 42001
ISO 42001 certifies that an organization has a responsible AI management system, the policies and processes for developing and operating AI. AIUC-1 incorporates a number of controls directly from ISO 42001 and then extends them, translating management-system requirements into auditable technical controls and adding protections against risks like hallucinations and jailbreaks. Many organizations pursue both: ISO 42001 builds the governance, AIUC-1 proves the safeguards behind it hold up under testing.
AIUC-1 vs. ISO 27001
ISO 27001 governs information security management broadly. It is foundational and agnostic to AI. AIUC-1 assumes that kind of security baseline exists and focuses on the agent-specific layer above it, so the two rarely overlap.
AIUC-1 vs. NIST AI RMF
The NIST AI Risk Management Framework provides high-level, voluntary guidance with no certification path. It tells organizations what to think about, not how to prove they have done it. AIUC-1 takes NIST’s functions and turns them into specific, testable controls, which is the piece NIST deliberately leaves open.
AIUC-1 also maps to threat models the security community already uses, including MITRE ATLAS, the OWASP Top 10 for Agentic Applications, and the OWASP LLM Top 10, and it maps more than 30 articles of the EU AI Act to auditable requirements.
How to Prepare for AIUC-1 Certification
Start with scope. Decide which agent or product you are certifying and document its data flows, the tools it can call, the models and versions it runs on, and its level of autonomy. That definition determines which controls apply and shapes everything downstream.
Next, run a readiness assessment against the six domains and fix the gaps before the formal audit begins. If you already hold ISO 42001 or have a NIST AI RMF program, map what you have onto AIUC-1’s controls; much of the operational and legal evidence will carry over. Build out the technical testing capability you will need: adversarial testing for prompt injection, groundedness evaluation for hallucinations, and output moderation. Going into the audit with that infrastructure already running is what separates a four-week certification from a ten-week one.
Benefits of Becoming AIUC-1 Certified
The headline benefit is faster enterprise deals. A certificate, report, and evaluation results give procurement, legal, and security teams a structured way to clear AI-specific risk, which removes a common point of friction late in the sales cycle. One certified executive summed it up by saying the certificate lets them sign contracts faster because it is a clear signal of trust.
Beyond sales, the process improves the product. The measurable drops in hallucination and inappropriate-output rates that companies report during certification are real engineering wins, not marketing. AIUC-1 also carries an insurance dimension that sets it apart: certification is backed by Lloyd’s of London insurance, and AIUC underwrites the risk associated with the certified agent. That changes the incentive structure, because the body certifying the agent also takes on financial exposure if it fails.
Common Challenges in Achieving AIUC-1 Certification
The first challenge is technical readiness. Building reliable defenses against prompt injection and hallucination is hard engineering work, and the readiness phase often surfaces gaps that take real effort to close.
Scope ambiguity is the second: because AIUC-1 does not define “AI agent,” getting the scope right requires careful judgment, and a scope drawn too narrowly undermines the certificate’s value.
The third challenge is structural, and buyers as much as vendors should understand it. AIUC authors the standard, runs the technical evaluations, issues the certificates, and sells the AI agent insurance that the certification enables. Security researcher Zack Korman has argued that this vertical integration creates potential conflicts of interest at several steps, with the closest precedent being the issuer-pays model in credit ratings, an arrangement that contributed to inflated ratings before the 2008 financial crisis. AIUC’s counterargument is that its insurance business creates a counter-incentive, since losses on a certified agent hit AIUC directly. There is also no external accreditation body: AIUC accredits its own auditors, so calling AIUC-1 a “standard” rests on AIUC’s own authority rather than a third party like ANSI or UKAS. None of this makes the certificate worthless. It makes it evidence to interrogate rather than a guarantee to accept at face value.
Important: No certification eliminates risk from a probabilistic, fast-changing system. Just as a SOC 2 report or a penetration test does not prove a system is secure against every threat, an AIUC-1 certificate cannot guarantee an agent is safe. Treat it as tested evidence of specific controls, scoped to a specific system, at a specific point in time.
The Bottom Line
AIUC-1 is the first serious attempt to give AI agents the kind of independent, testable security assurance that SOC 2 gave SaaS. It audits six domains that existing frameworks miss, runs on a quarterly testing cadence built for how fast AI moves, and comes backed by insurance that puts the issuer’s own money behind the result. It is also young, self-accredited, and commercially structured in ways worth scrutinizing.
For vendors selling agentic AI into enterprises, the practical question is no longer whether AI-specific certification is coming, but whether you would rather lead the conversation or explain to a procurement team why you cannot answer it. If buyers are already asking, the answer is straightforward.
Frequently Asked Questions About AIUC-1 Certification
Is AIUC-1 certification mandatory?
No. AIUC-1 is voluntary. It is not required by law anywhere. Demand is driven by enterprise buyers who want independent assurance on AI-specific risks, not by regulation.
Can startups get AIUC-1 certified?
Yes. Certified organizations range from seed-stage startups to publicly traded enterprises. Company size does not gate eligibility; the scope and maturity of the agent’s safeguards do.
Does AIUC-1 certification guarantee an AI agent is safe?
No. Like a SOC 2 report or a penetration test, AIUC-1 provides evidence that specific controls were tested, scoped to a specific system at a point in time. It cannot eliminate all risk from a probabilistic, fast-evolving system.
Can AIUC-1 certification be revoked?
A certificate is valid for twelve months but depends on quarterly technical testing to stay current. Failing to maintain the quarterly cadence causes the certification to lapse before the twelve-month period ends.
Does AIUC-1 replace existing security certifications?
No. AIUC-1 complements SOC 2, ISO 27001, and ISO 42001 rather than replacing them. It covers agent-specific risks those frameworks were not designed to address, and SOC 2 in particular remains expected for enterprise sales.
Is AIUC-1 only for customer service AI agents?
No. Customer service agents are a common use case because brand and customer data are on the line, but certified systems also include candidate scoring agents, internal automation agents, summarization agents, and image generation agents.
How is AIUC-1 enforced?
Through the audit and the insurance model rather than through regulation. Accredited auditors prepare reports, AIUC issues certificates and runs quarterly technical testing, and the insurance backing ties certification to real financial exposure if a certified agent fails.


