

After a SOC 2 and ISO 27001 engagement, there are two documents out of the whole pile that actually close deals: the SOC 2 attestation report and the ISO 27001 certificate. Everything else your engagement produces exists to create those two, support them, or keep them alive for another year.
Companies routinely ask their auditor for a SOC 2 certificate, which doesn’t exist. They send a prospect their full ISMS documentation when a one-page certificate would have done. They pay for six months of readiness work and then can’t say what they’re holding at the end of it.
So here’s the full list. What a SOC 2 engagement produces, what an ISO 27001 engagement produces, what a combined program produces, and who gets to see each one.
Understanding SOC 2 and ISO 27001 Engagement Outputs
The Core Difference: Report vs. Certificate
SOC 2 is an attestation. A licensed CPA firm examines your controls against the Trust Services Criteria under standards set by the AICPA, then writes up what it found and signs an opinion. No certificate. No logo from the AICPA. No pass or fail stamp. What you get is the report, and it usually runs 60 to 120 pages.
ISO 27001 is a certification. An accredited certification body audits your Information Security Management System (ISMS) against ISO/IEC 27001:2022, and if you conform, it issues a certificate of registration. The certificate itself is a page or two. All the detail lives behind it, in your ISMS documentation and the audit reports the certification body writes as it goes.
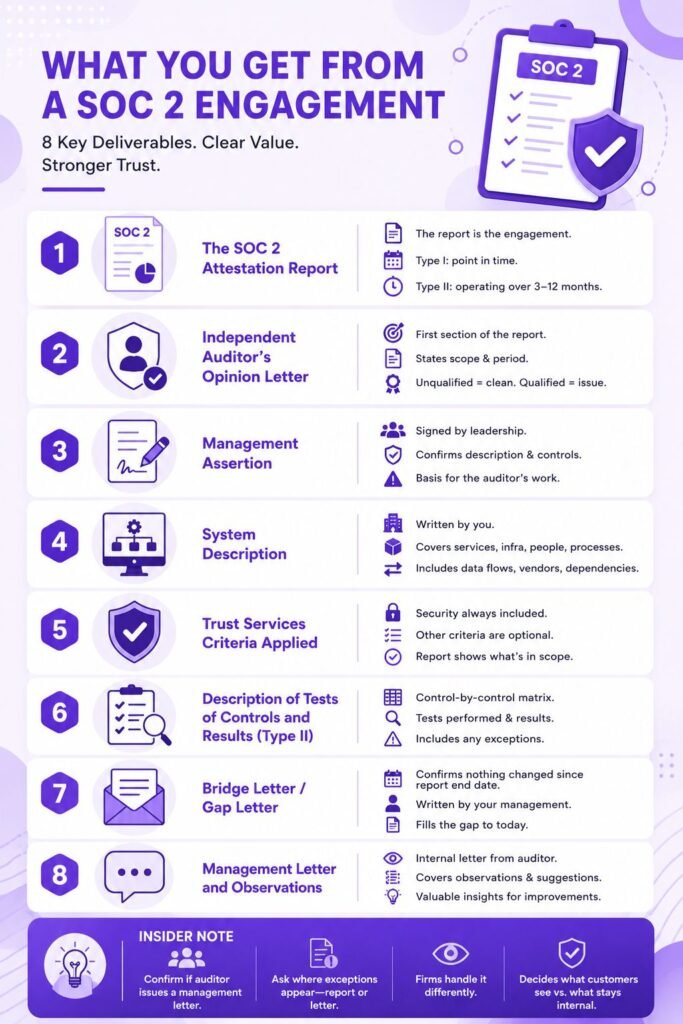
SOC 2 Engagement Deliverables
The SOC 2 Attestation Report
The report is the engagement. The AICPA’s illustrative SOC 2 report lays out the standard structure: auditor’s report, management’s assertion, system description, the Trust Services Criteria in scope, and the controls tested with their results.
- A Type I covers control design at one point in time.
- A Type II covers whether those controls actually operated over a period, usually three to twelve months, and most enterprise buyers now won’t accept anything else.
Independent Auditor’s Opinion Letter
First section of the report, and the first thing anyone experienced turns to. It gives the scope, the examination period, and the auditor’s conclusion.
- An unqualified opinion means the description held up and the controls worked.
- A qualified opinion means the auditor found something material, and every serious reviewer will want to talk about it.
Management Assertion
Your leadership signs a written statement stating that the system description is accurate and that the controls were properly designed and are operating. It reads like a formality, and it isn’t. The auditor’s entire examination runs against what management asserts here, so overstating anything creates real exposure.
System Description
Usually the longest part of the report, and you write it, not the auditor. It covers the services in scope, your infrastructure, software, people, processes, how data moves, which subservice organizations you depend on, and the complementary user entity controls your customers have to run on their side for your controls to hold up.
Trust Services Criteria Applied
Security (the Common Criteria) is in every SOC 2. Availability, Processing Integrity, Confidentiality, and Privacy are optional, and the report names exactly which ones you picked. Whatever you decide during scoping ends up printed in a document your customers read for the next several years.
Description of Tests of Controls and Results (Type II)
The matrix: every control, what the auditor did to test it, and what came back, including exceptions. Reviewers spend most of their time here, because the exceptions tell them things the opinion letter won’t.
Bridge Letter / Gap Letter
Your report covers a fixed window, so one ending December 31 leaves a hole for a customer doing diligence in June. A bridge letter from your management, not the auditor, confirms that nothing material changed in the control environment between the report’s end date and today. You’ll write these often enough to keep a template.
Management Letter and Observations
Plenty of auditors also send an internal-only letter covering observations, minor exceptions, and suggestions that never reached the threshold of a qualified opinion. It’s the closest thing to free consulting you’ll get before next year’s audit starts.
Insider Note: Ask early whether your auditor issues a management letter, and whether exceptions land in the report body or only in that letter. Firms handle this differently, and the answer decides what your customers see versus what stays behind your firewall. It rarely comes up in the proposal, but it changes how the finished report reads to a buyer.
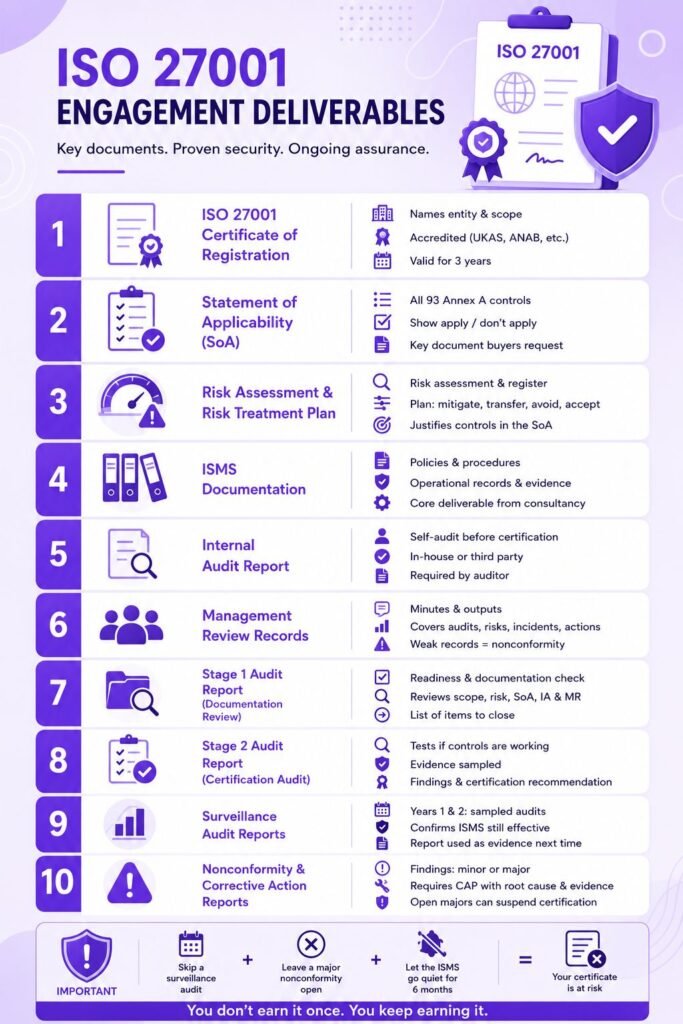
ISO 27001 Engagement Deliverables
ISO 27001 Certificate of Registration
The document everyone asks for. It names the certified legal entity, states the ISMS scope, identifies the certification body, carries an accreditation mark from a body recognized under the International Accreditation Forum such as UKAS or ANAB, and shows the validity dates. It’s good for three years as long as you pass annual surveillance audits.
Read the scope statement carefully, on your own certificate as much as anyone else’s. A certificate covering one office or one product line says nothing about the rest of the business.
Statement of Applicability (SoA)
After the certificate, this is the document buyers request most. The Statement of Applicability runs through all 93 Annex A controls in ISO/IEC 27001:2022, says which apply to you, justifies the ones you excluded, and records where each stands. Auditors use it as the map of your control environment, and larger customers increasingly want to see it or a summary of it during diligence.
Risk Assessment and Risk Treatment Plan
Your methodology, the register it produced, and the Risk Treatment Plan showing what you decided to do about each significant risk: mitigate it with a control, transfer it, avoid it, or accept it. ISO 27001 is built around risk, so these documents are what justify every control decision recorded in the SoA.
Information Security Management System (ISMS) Documentation
The policy and procedure set, plus the operational records that prove any of it happens. Information security policy, access control, incident management, supplier security, business continuity, and the rest. When a consultancy builds your ISMS, this pile is most of what they hand over at the end.
Internal Audit Report
You have to audit yourself before the certification body does. The internal audit report, done in-house or outsourced, is a mandatory record and one of the first things an external auditor asks to see.
Management Review Records
Minutes and outputs from leadership’s formal review of the ISMS: audit results, changes in risk, incidents, and what the business decided to do about them. Missing records, or records that were obviously written the week before the audit, are a reliable way to collect a nonconformity.
Stage 1 Audit Report (Documentation Review)
Stage 1 is a readiness check. The auditor reads your scope, risk assessment, Statement of Applicability, and the evidence that you’ve run an internal audit and a management review, then decides whether you’re ready for Stage 2. The report comes back as a list of things to close first.
Stage 2 Audit Report (Certification Audit)
Stage 2 tests whether any of it is true. The auditor samples evidence across your operation to confirm the controls you selected are running, then writes up the findings with a certification recommendation.
Surveillance Audit Reports
In years one and two, the certification body samples part of the ISMS rather than reviewing the whole thing, checking that it still runs and still improves. Each visit produces a report, and each report becomes evidence at the next one.
Nonconformity and Corrective Action Reports
Findings are graded.
- A minor nonconformity is an isolated slip.
- A major nonconformity points to something systemic and can hold up or suspend certification.
Each one generates a corrective action plan (CAP) with root cause analysis and proof you closed it, and the auditor will pull those up next visit.
Important: Certificates get suspended between audits. Skip a surveillance visit, leave a major nonconformity open, or let the ISMS go quiet for six months, and the certificate is at risk well before the three years are up. You don’t earn it once. You keep earning it.
Shared Deliverables in a Combined SOC 2 + ISO 27001 Engagement
Somewhere around 70 to 80 percent of the underlying work is the same for both frameworks, which is why combined programs have become the default for companies selling into the US and internationally at once. Run properly, you end up with one set of artifacts instead of two stacks that slowly drift apart.
Unified Policy and Procedure Set
One set of policies mapped to the Trust Services Criteria and Annex A at the same time. Keep two sets, and you’ll maintain both badly, and eventually they’ll contradict each other in front of an auditor.
Consolidated Risk Register
A single register feeding the ISO 27001 risk treatment process and SOC 2’s risk assessment criteria under CC3. You maintain it once, and both auditors sample from it.
Shared Evidence Repository
Access reviews, change tickets, training records, vendor assessments, all collected once and tagged to both frameworks, usually inside a GRC platform like Vanta or Drata. Most of the cost savings people expect from a combined engagement actually come from here.
Combined Control Matrix / Crosswalk
A mapping document showing how each control you’ve implemented satisfies specific Trust Services Criteria and specific Annex A controls. Without the crosswalk, “collect once, comply twice” stays a slogan.
Integrated Gap Assessment Report
One readiness assessment scored against both frameworks, producing one prioritized remediation list rather than two that compete for the same engineers.
Pro Tip: Line up your SOC 2 Type II Observation
Line up your SOC 2 Type II observation window with the ISO surveillance schedule before either clock starts. Companies that stagger them by a few months end up in audit season permanently, fielding evidence requests every month of the year. One shared calendar takes a surprising amount of pressure off the team doing the collecting.
Pre-Engagement Deliverables (Readiness Phase)
Readiness has its own outputs, and they usually come from a consultancy rather than the auditor or certification body, since independence rules cap how much hands-on help the certifying party can give you.
Readiness Assessment Report
An evaluation of where you stand against every applicable requirement, with gaps rated by severity and by how much work they’ll take. This is the Readiness Assessment Report that turns “we should probably get SOC 2” into a plan with a number attached.
Scoping Document
Names the systems, locations, entities, people, and for SOC 2 the Trust Services Categories in scope. What you decide here flows straight into the system description and the scope line on your certificate, so it deserves an hour of executive attention rather than a signature.
Remediation Roadmap
The sequenced plan for closing each gap, with owners and dates, normally built backward from the date your Type II window opens or your Stage 1 audit begins.
Control Design Documentation
Written descriptions of each control: what it does, who runs it, how often, and what evidence it leaves behind. Auditors test against these descriptions, so vague control language produces exceptions you didn’t need to have.
Post-Engagement Deliverables
Final Report Distribution Package
For SOC 2, the signed report plus guidance on who can receive it, since SOC 2 reports are restricted-use documents that go out under NDA. For ISO 27001, the certificate, the certification body’s rules for using its mark, and the final audit report.
Customer-Facing Trust Documentation
Most companies build a trust page or a security packet: the ISO certificate, a SOC 3 summary if they have one, penetration test summaries, and pre-written answers to the questions everyone asks. Your engagement deliverables feed it. The packet is what sales actually sends.
Renewal and Continuous Monitoring Schedule
A Renewal and Continuous Monitoring Schedule covering the next SOC 2 observation period, surveillance dates, internal audits, management reviews, access reviews, and policy refreshes. Skip it and year two turns into the same scramble as year one, which is the thing everyone swore wouldn’t happen again.
Corrective Action Tracking
A live register of exceptions, nonconformities, and observations from every audit, with status and closure evidence. Your next SOC 2 auditor and your surveillance auditor will both open with the same question: what happened to last year’s findings?
Who Receives Each Deliverable?
Internal Stakeholders
Leadership signs the management assertion and receives the management letter, the audit reports, and any nonconformities. Security and engineering own the ISMS documentation, the control matrix, and the corrective action register. Boards now tend to expect a summary of both audit outcomes as part of cyber risk oversight.
Customers and Prospects
Customers get the SOC 2 report under NDA, the certificate freely, and a bridge letter when they ask. Bigger ones may push for the SoA, penetration test summaries, or specific policy excerpts. Almost none of them have a legitimate claim on your full ISMS documentation, and handing it over sets a precedent you’ll regret.
Regulators and Third Parties
Regulators, cyber insurers, and partners generally take the certificate and the SOC 2 report as primary evidence. Insurers have started pricing against them, and a current Type II plus a valid certificate visibly shortens the underwriting questionnaire.
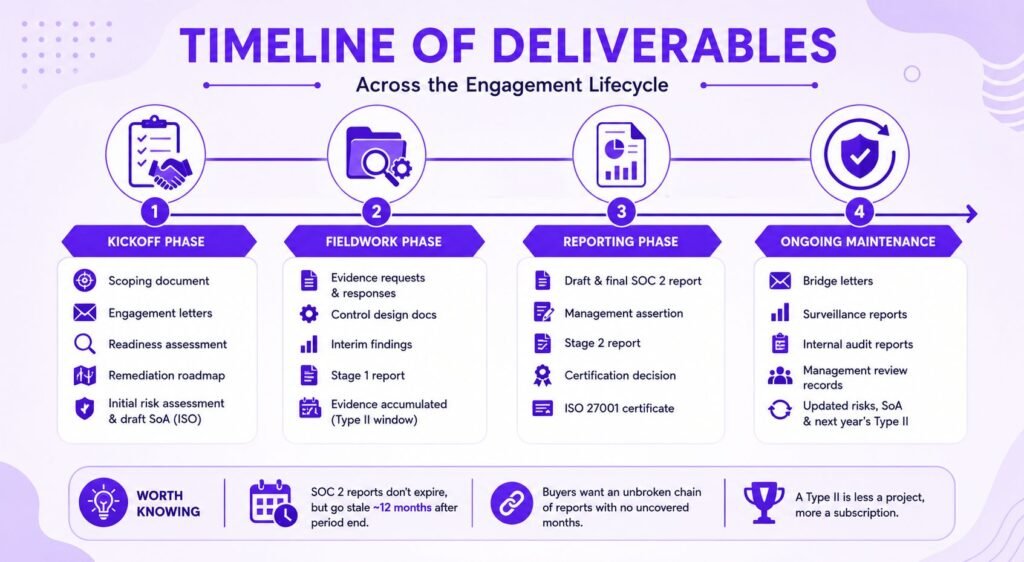
Timeline of Deliverables Across the Engagement Lifecycle
Kickoff Phase Outputs
Scoping document, engagement letters, readiness assessment, and remediation roadmap. On the ISO side, your initial risk assessment and a draft SoA land here too.
Fieldwork Phase Outputs
Evidence requests and responses, control design documentation, interim findings, the Stage 1 report, and for a Type II, the evidence accumulating through the observation window itself.
Reporting Phase Outputs
Draft and final SOC 2 report, the management assertion, the Stage 2 report, the certification decision, and the certificate. This phase compresses badly when fieldwork evidence was messy, which is the most common reason timelines slip.
Ongoing Maintenance Outputs
Bridge letters, surveillance reports, annual internal audit reports, management review records, updated risk assessments and SoA versions, and next year’s Type II. The stream doesn’t stop after certification. It settles into a rhythm.
Worth Knowing: SOC 2 reports carry no formal expiration date, but the market treats one as stale about 12 months past the period end. That makes a Type II less a project than a subscription, and what buyers really want is an unbroken chain of reports with no uncovered months in between.
Worth Knowing: SOC 2 Reports
SOC 2 reports carry no formal expiration date, but the market treats one as stale about 12 months past the period end. That makes a Type II less a project than a subscription, and what buyers really want is an unbroken chain of reports with no uncovered months in between.
Let Axipro help you build a business continuity plan that's practical, compliant, and audit-ready.
Schedule Your Free Assessment Today
In Summary
SOC 2 gets you a long, restricted-use report built from an opinion letter, a management assertion, a system description, and control test results, refreshed every year and bridged in between.
ISO 27001 gets you a public three-year certificate backed by the SoA, the risk treatment plan, your ISMS documentation, and the Stage 1, Stage 2, and surveillance reports behind it. Running both together adds shared artifacts, one policy set, one risk register, and one evidence repository, which is what makes doing both cheaper than doing either one twice.
Know what each document is for, who’s allowed to read it, and when the next one is due, and the whole engagement starts paying for itself in vendor reviews.
Frequently Asked Questions
Is the SOC 2 report the same as an ISO 27001 certificate?
No. The SOC 2 report is a detailed attestation from a CPA firm, shared under NDA. The ISO 27001 certificate is a short public document from an accredited certification body. Related questions, completely different artifacts.
Can one engagement produce both deliverables at once?
Yes, and plenty of companies now do exactly that. The CPA firm still issues the report and the certification body still issues the certificate, but one evidence collection effort, one policy set, and one audit calendar sit behind both.
How long are SOC 2 reports and ISO 27001 certificates valid?
A SOC 2 report covers its stated period and is generally accepted as current for around 12 months after that period ends. An ISO 27001 certificate lasts three years, assuming you pass the annual surveillance audits and keep the ISMS running.
Who owns the deliverables after the engagement ends?
You own the ISMS documentation, the policies, the risk register, the SoA, and the system description. The auditor keeps their workpapers. The report and certificate are issued to you, but the report carries distribution restrictions and the certificate comes with rules about how you can use the certification body’s mark.
Are the Statement of Applicability and SOC 2 System Description interchangeable?
No. The SoA is a control-by-control inventory against Annex A with justifications for anything excluded. The system description is a narrative about your services, infrastructure, and processes written for someone reading the report. Same subject matter, different structure and different audience.
What deliverables can be shared publicly vs. under NDA?
Public: the certificate, a SOC 3 report if you commission one, and whatever summary you put on your trust page. Under NDA: the SOC 2 report, the SoA in most cases, bridge letters, and audit findings. Not shared at all: internal audit workpapers, the raw risk register, and detailed corrective action records.
Do surveillance audits produce new deliverables each year?
Yes. Each one produces a report, plus any nonconformities raised and the corrective action records that close them. Updated SoA versions, internal audit reports, and management review minutes pile up alongside, and the recertification audit in year three goes back through the whole trail.


