
Most companies pursuing ISO 27001 certification for the first time will spend between $10,000 and $50,000 in year one, and far less than half of that goes to the auditor. A 50-person SaaS company typically pays $10,000 to $22,000 in certification body fees alone, then doubles or triples that figure in implementation work, tooling, and internal hours before the Stage 2 audit even begins. The wide range exists because ISO 27001 certification cost is not a price tag; it is the sum of a dozen separate decisions: your scope, your security maturity, your certification body, and whether you build the ISMS yourself, hire a consultant, or run it through a compliance automation platform.
This article breaks down every one of those costs, stage by stage and region by region, including the ones that never appear in vendor quotes.
Startups under 50 employees can price the readiness work up front. Axipro’s Achievement Plan starts at $4,000 for companies of that size. That fee covers the implementation work, not the certification body’s audit, which is billed separately and is the other large line in your budget. The sections below show what each piece costs and where fixed-fee readiness fits.

What Determines ISO 27001 Certification Cost?
Six variables drive almost all of the variance between a $10,000 certification and a $150,000 one.
Company Size and Employee Count
Headcount is the single biggest cost driver because certification bodies calculate audit days (mandays) primarily based on the number of people working within the scope of your Information Security Management System (ISMS). The calculation is not arbitrary: accredited bodies follow the audit time tables in ISO/IEC 27006, which means a 20-person company and a 200-person company will receive structurally different quotes no matter how hard they negotiate. More employees also means more interviews, more evidence sampling, and more Annex A controls applied across more people.
Scope and Complexity of the ISMS
Scope is the variable you actually control. Your Statement of Scope defines which business units, systems, products, and locations fall inside the ISMS. A scope limited to one product line and the engineering team that runs it costs dramatically less to implement and audit than a whole-of-company scope. Complexity compounds this: bespoke infrastructure, regulated data types, and heavy third-party dependency chains all add controls, evidence, and audit time.
Number of Physical and Cloud Locations
Each physical site within scope can require its own audit visit, with travel costs on top. Multi-site organizations can reduce this through sampling (more on the square root rule later), but every additional location still adds something. Cloud environments count too: multiple cloud providers, regions, and tenancy models expand the technical scope auditors must cover, even when no travel is involved.
Existing Security Maturity
A company that already runs access reviews, maintains an asset inventory, and documents its incident response process is buying a much shorter journey than one starting from a blank page. The gap analysis exists precisely to price this difference. Organizations already aligned to SOC 2, NIST CSF, or Cyber Essentials Plus typically reuse 50 to 70 percent of their existing controls and evidence, which translates directly into lower implementation cost.
Choice of Certification Body
Certification bodies are not interchangeable on price. Large international names like BSI, Bureau Veritas, LRQA, and DNV charge premium day rates, often 30 to 50 percent above smaller accredited bodies, and their brand carries weight with enterprise procurement teams. What matters most is accreditation: a certificate issued by a body accredited by UKAS, ANAB, or another IAF (International Accreditation Forum) member carries international recognition. An unaccredited certificate is cheaper and close to worthless in serious sales conversations.
Internal vs. External Implementation Approach
The final driver is who does the work. Internal teams cost salary hours. Consultants cost fees. Platforms cost subscriptions. Each approach lands at a very different total, which is why this article dedicates a full section to it below.
Average ISO 27001 Certification Cost Ranges
The ranges below cover total first-year cost: implementation, tooling, and certification audits combined. They assume an accredited certification body and a sensibly defined scope.
Cost for Small Businesses and Startups (1–50 Employees)
A focused startup with a single product, cloud-native infrastructure, and a tight scope can realistically certify for $10,000 to $35,000 all-in. Lean implementations using templates or an automation platform sit at the bottom of that range. UK micro-businesses can find UKAS-accredited audit fees starting around £6,250, with day rates near £1,250.
Startup Budget Example: Readiness Plus Certification Audit
A startup with under 50 employees pays three separate parties, and only one is a consultant.
| Cost line | Typical startup cost | Who bills it |
|---|---|---|
| ISO 27001 readiness: risk assessment, policies, control implementation, audit preparation | From $4,000 with Axipro’s Achievement Plan (under 50 employees) | Axipro |
| Certification audit, Stage 1 and Stage 2 | $5,000 to $10,000 for a small scope | Accredited certification body |
| Tooling gaps, training, and internal time | Varies with what you already run | You |
Readiness from $4,000 plus a small-scope audit of $5,000 to $10,000 puts the external invoices for a lean startup scope at roughly $9,000 to $14,000. Tooling gaps and internal time sit on top, which is how the all-in figure reaches the $10,000 to $35,000 range above.
The Achievement Plan includes a dedicated information security team, a dedicated project manager, vulnerability scanning, and facilitation of your external audit, with guaranteed certification. ISO 27001 readiness takes as little as six weeks, and your team commits about five hours a week. The $4,000 price covers companies with fewer than 50 employees. Larger companies are priced separately.
Cost for Mid-Sized Organizations (50–250 Employees)
This is where most certifications happen, and where costs spread widest. Expect 8 to 12 initial audit days, $30,000 to $80,000 in total first-year spend, and a six to nine month timeline. Multiple departments, more mature customer requirements, and the first real multi-team coordination overhead all show up in the budget.
Cost for Large Enterprises (250+ Employees)
Enterprise certifications routinely exceed $100,000 in year one once you include program management, multiple sites, and large-scale audits. The audit fee alone can pass $50,000 for complex, multi-site scopes. At this scale, the internal time investment, covered under hidden costs below, often outweighs every external invoice.
ISO 27001 Cost Breakdown by Stage
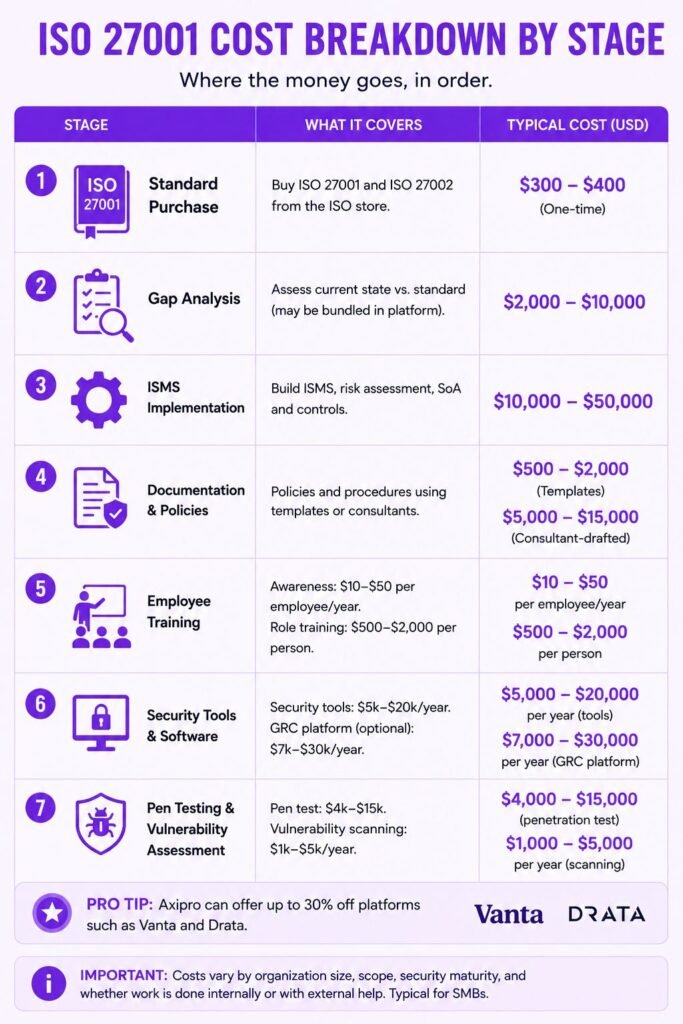
Here is where the money actually goes, in roughly the order you will spend it.
Cost of Purchasing the ISO 27001 Standard
The official ISO/IEC 27001:2022 document costs CHF 155 (roughly $170) from the ISO store. Most teams also buy ISO 27002, the implementation guidance for the Annex A controls, for a similar amount. Budget $300 to $400 for both. Do not skip this purchase: implementing against second-hand summaries of the standard is a common source of audit findings.
Gap Analysis Costs
A consultant-led gap analysis before committing to anything else runs $2,000 to $10,000 depending on scope, while platform-based readiness assessments are often bundled into the subscription. The output, a clear map of where you stand against every clause and control, is what makes the rest of the budget predictable.
ISMS Implementation Costs
This is the largest and most variable line item: building the risk assessment, the risk treatment plan, the Statement of Applicability (SoA), and operationalizing the controls you have selected. Done internally, it consumes 200 to 600 hours of staff time over four to eight months. Done with consultants, expect $10,000 to $50,000 in fees for a typical SMB.
Documentation and Policy Development Costs
ISO 27001 requires a defined set of documented policies and procedures. Template toolkits cost $500 to $2,000 and save weeks. Consultant-drafted documentation runs $5,000 to $15,000. Writing everything from scratch internally is free on paper and expensive in reality.
Employee Training Costs
Security awareness training for all in-scope staff costs roughly $10 to $50 per employee per year via standard platforms. Formal role-based training, such as internal auditor or implementer courses, costs $500 to $2,000 per person. A Lead Auditor course, useful if you want internal audit capability in-house, sits at the top of that range.
Security Tools and Software Costs
Most organizations need to fill at least some tooling gaps: endpoint management, MDM, vulnerability scanning, logging and monitoring, password management. Budget $5,000 to $20,000 annually depending on what you already run. A GRC platform or compliance automation tool adds $7,000 to $30,000 per year on top, if you go that route.
We’ve previously written about the cost of Vanta.
Penetration Testing and Vulnerability Assessment Costs
ISO 27001 does not strictly mandate a penetration test, but auditors expect to see technical vulnerability management in practice, and most certified companies run one. A scoped external penetration test costs $4,000 to $15,000; automated vulnerability assessment tooling runs $1,000 to $5,000 per year.
Pro Tip: Axipro Offers
As implementation partners, Axipro can offer up to 30% off popular compliance automation platforms such as Vanta and Drata.
Internal Audit Costs
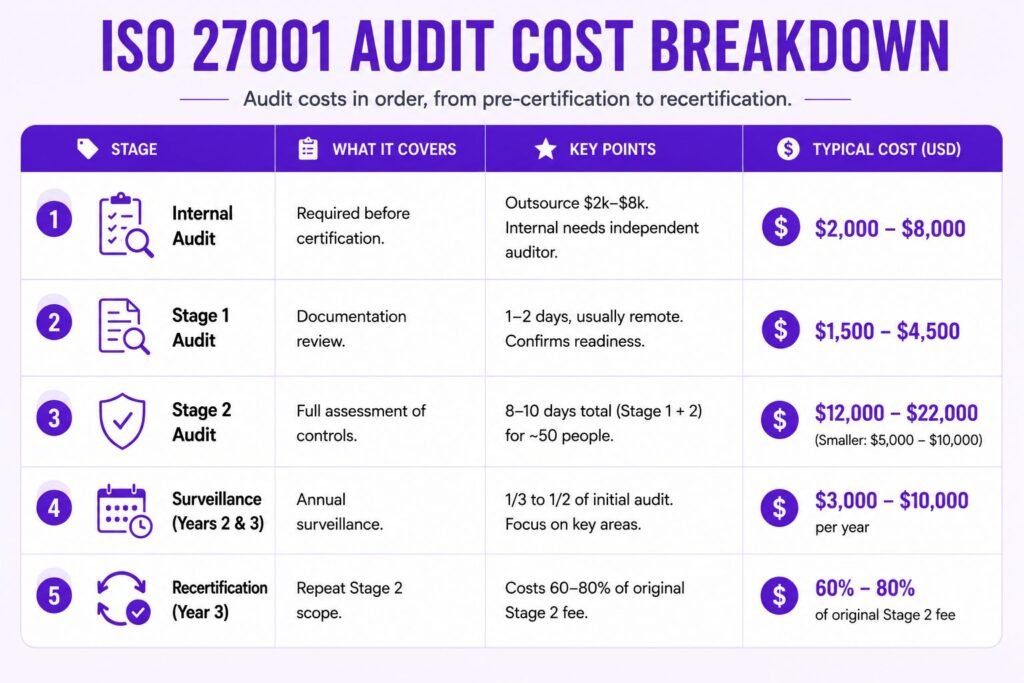
The standard requires a completed internal audit before certification. Outsourcing it to an independent consultant costs $2,000 to $8,000. Doing it internally requires a trained auditor who is independent of the ISMS they audit, which is genuinely difficult in companies under 50 people. Most small organizations outsource this one.
Stage 1 Audit Costs
The Stage 1 audit is a documentation readiness review, typically one to two audit days, often conducted remotely. At prevailing day rates of $1,500 to $2,200, expect $1,500 to $4,500. Its job is to confirm you are ready for Stage 2 and flag anything that would cause a failure.
Stage 2 Certification Audit Costs
The Stage 2 audit is the full assessment: interviews, evidence sampling, and control testing against your SoA. For a 50-person company, the combined Stage 1 and 2 effort typically lands at 8 to 10 audit days, putting certification body fees at $12,000 to $22,000 before travel. Smaller scopes can come in at $5,000 to $10,000.
Surveillance Audit Costs (Years 2 and 3)
Certification runs on a three-year cycle. In years two and three, the certification body returns for a surveillance audit, typically one-third to one-half the duration of the initial audit, focused on core clauses, internal audit, management review, and a sample of controls. Budget $3,000 to $10,000 per year for most SMBs.
Recertification Audit Costs (Year 3)
At the end of year three, a recertification audit repeats most of the Stage 2 scope. Price it at 60 to 80 percent of the original Stage 2 fee. Companies that maintained their ISMS well find it routine; companies that let the system gather dust effectively pay for implementation twice.
ISO 27001 Cost by Implementation Approach
DIY with an Internal Team
Lowest cash outlay, highest time cost. You pay for the standard, a template toolkit, training, tooling gaps, and the audits. The real price is 300 to 600 hours of staff time, and the real risk is a failed or delayed audit caused by inexperience with auditor expectations.
Hiring an ISO 27001 Consultant
Consultants charge $150 to $300 per hour, or $15,000 to $50,000 for a full implementation engagement. A vCISO retainer ($3,000 to $10,000 per month) is a common variant that spreads the cost and keeps expertise available after certification. Consultants shine on complex scopes, awkward legacy environments, and organizations with no internal security function.
Fixed-fee readiness sits between those two routes. Instead of hourly billing, you pay one published price for the implementation work, and your team knows the number before the project starts. Axipro’s Achievement Plan works like this: starting at $4,000 for companies with under 50 employees, excluding the certification body’s audit fee, with guaranteed certification. After certification, the Trust Assurance Plan covers maintenance from $500 per month, which sits at the low end of the fractional CISO pricing range we break down separately.
Using a Compliance Automation Platform
Platforms automate evidence collection from your cloud stack, ship policy templates, and run continuous control monitoring. Subscriptions for ISO 27001 typically run $7,000 to $30,000 per year depending on company size and the number of frameworks. They compress timelines dramatically for cloud-native companies and do much less for organizations with significant on-premise or physical scope.
Hybrid Approach
The most common pattern in practice: a platform for evidence automation and continuous monitoring, plus a fractional consultant for the judgment-heavy work, risk assessment, scoping, internal audit, and audit accompaniment. It usually beats either pure approach on total cost of ownership for SMBs.
Hidden Costs of ISO 27001 Certification
The line items above are the visible budget. These are the ones that surprise people.
Lost Productivity and Internal Time Investment
Even with consultants and platforms, your team still attends interviews, remediates findings, documents processes, and sits in audits. For a mid-sized company, expect 200 to 500 internal hours in year one. At a blended $75 per hour, that is $15,000 to $37,500 of payroll that never appears on a compliance invoice.
Re-Audit Fees After a Failed Audit
Major nonconformities at Stage 2 do not usually void the whole audit, but they do require remediation and a follow-up assessment, typically one to three additional audit days plus fees, at $1,500 to $6,000. Worse is the delay: a three-month slip can cost deals that were waiting on the certificate.
Platform Lock-In and Subscription Growth Fees
Automation platforms price by headcount and framework count, so the subscription grows as you do. Migrating years of evidence and control mappings to another platform is painful enough that few companies ever do it. Model the three-year subscription cost, not the year-one promotional price.
Multi-Site Audit Add-Ons
Every sampled site adds audit days, travel, and accommodation to the certification body invoice. Organizations frequently discover these travel recharges only when the first invoice arrives, because quotes are often presented exclusive of expenses.
Ongoing Maintenance and Continuous Improvement
ISO 27001 is a management system, not a plaque. Budget ongoing internal audits, management reviews, risk assessment refreshes, training renewals, and control operation at $5,000 to $25,000 per year in mixed internal and external costs. Certificates lapse for companies that treat year one as the finish line.

ISO 27001 Certification Cost by Region
Audit day rates and consultant fees vary substantially by market, even though the standard and the audit-day tables are global.
United States
The most expensive market for both auditors and consultants, with ANAB-accredited bodies charging $1,500 to $2,200 per audit day. US buyers more often pair ISO 27001 with SOC 2, which changes the budget conversation entirely (see bundling, below).
United Kingdom
UKAS-accredited audits average around £1,250 per day in 2026, with micro-business certification audit packages starting near £6,250. The UK has a deep consultant market, which keeps implementation pricing competitive.
European Union
Rates broadly track the UK, with national accreditation bodies (DAkkS in Germany, COFRAC in France) all operating under the same IAF umbrella. GDPR records of processing requirements make ISO 27001 a common board-level mandate, and certificates from any EU-accredited body are recognised across the bloc.
Australia
JAS-ANZ-accredited bodies price slightly above European equivalents once travel is included, since multi-site Australian scopes often involve significant distances. Government supply chains increasingly expect certification, supporting both demand and prices.
Canada
Pricing sits just under the US market. Many Canadian companies use US-based certification bodies, and cross-border audit delivery (often remote) keeps rates aligned.
India
The cheapest major market by far: full certifications for small scopes can complete for under $10,000. The critical check is accreditation. Certificates from non-IAF bodies sell cheaply in this market and fail procurement review with international customers.
When Do You Pay? ISO 27001 Cost Cash Flow Timeline
The spend is front-loaded but not simultaneous.
- Months one to two: the standard, gap analysis, and any platform or consultant onboarding (10 to 20 percent of year-one budget).
- Months two to six: implementation, documentation, tooling, and training (50 to 60 percent).
- Months six to nine: internal audit, penetration test, and Stage 1 and Stage 2 fees (25 to 35 percent).
Certification body fees are usually invoiced per stage, and many bodies offer the three-year cycle, initial plus two surveillance audits, on a payment schedule. From year two onward, costs settle into a predictable annual rhythm of surveillance fees plus maintenance.
How to Reduce ISO 27001 Certification Costs
Start with a Scoped Gap Analysis
Spending $3,000 on a gap analysis before committing to anything else routinely saves five figures later, because it lets you scope the ISMS around what you already do well and price the genuine gaps accurately.
Reuse Existing Documentation and Controls
SOC 2 controls, NIST CSF mappings, GDPR records of processing, and even informal runbooks all count. Auditors care that controls exist and operate, not that they were written fresh for ISO 27001.
Apply the Square Root Rule for Multi-Site Audits
Under IAF MD 1, the mandatory multi-site sampling rules, certification bodies can sample sites rather than visit all of them: the initial audit samples roughly the square root of total sites, surveillance audits sample about 0.6 times the square root, and recertification about 0.8 times. A 25-site organization gets audited at five sites in year one instead of twenty-five. Structuring your ISMS with a genuine central function is what unlocks this, and it is one of the largest single savings available to distributed companies.
Negotiate Multi-Year Audit Contracts
Committing to the full three-year cycle with one certification body typically earns a 10 to 20 percent discount on audit fees and locks the day rate against annual increases. Quotes are negotiable; treat the first number as an opening position.
Bundle ISO 27001 With Other Audits (SOC 2, ISO 42001)
Integrated audits share evidence, interviews, and sometimes audit days. Pairing ISO 27001 with SOC 2, or adding ISO 42001 for AI management systems, through the same audit firm commonly cuts 20 to 30 percent against running each engagement separately. The overlap in controls does most of the work: a single access review can serve three frameworks.
Leverage Templates and Toolkits
A $1,000 documentation toolkit replacing $10,000 of consultant drafting is the single best cost-to-value ratio in the entire project, provided someone internal actually adapts the templates to reality. Auditors spot unmodified boilerplate instantly, and generic policies that do not match practice generate nonconformities.
ISO 27001 Certification Cost vs. ROI
Cost of Certification vs. Cost of a Data Breach
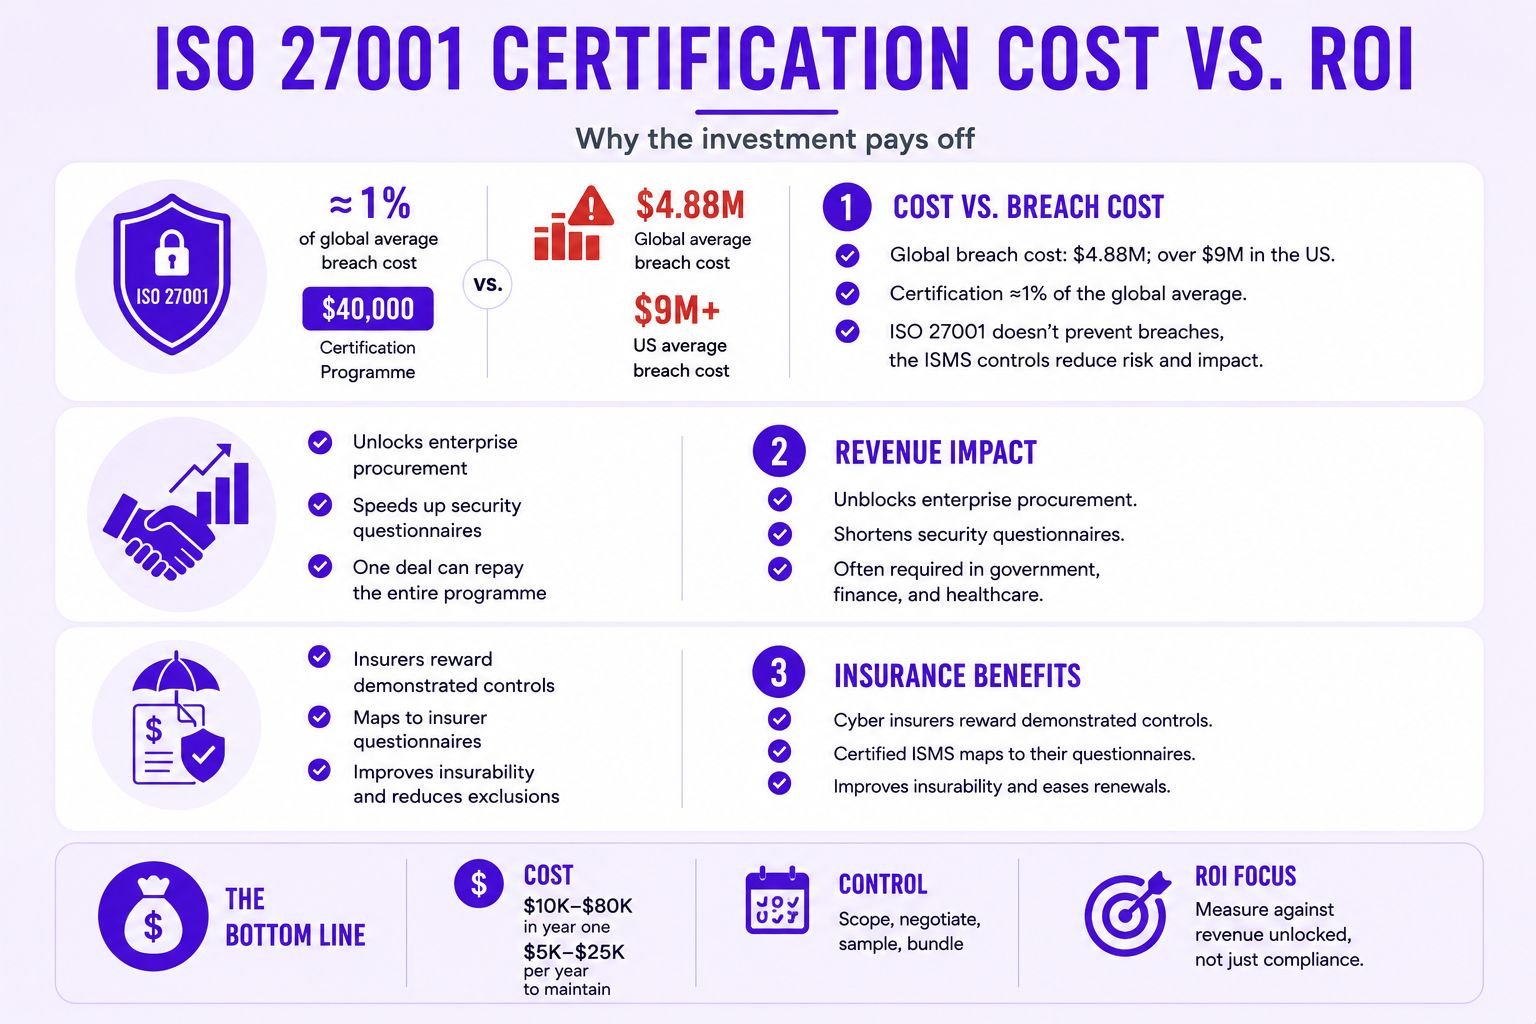
IBM’s 2024 Cost of a Data Breach Report puts the global average breach cost at $4.88 million, with US organizations averaging over $9 million. A $40,000 certification program is roughly one percent of that global average. The certification itself does not prevent breaches, but the ISMS discipline behind it (asset inventories, access reviews, incident response, vendor management) demonstrably reduces both likelihood and impact.
Revenue Impact and Sales Enablement
For most companies, the honest ROI case is commercial, not defensive. Certification unblocks enterprise procurement, shortens security questionnaires from weeks to days, and is increasingly a hard tender requirement in government, finance, and healthcare supply chains. One enterprise deal that closes because the certificate exists usually repays the entire program.
Reduced Insurance Premiums
Cyber insurers increasingly price against demonstrated security controls, and a certified ISMS maps directly onto their underwriting questionnaires. The more reliable benefit, beyond reported premium reductions, is insurability itself: certified organizations face fewer exclusions and less painful renewals.
In short: ISO 27001 certification costs most organizations between $10,000 and $80,000 in year one, driven primarily by headcount, scope, and implementation approach, with $5,000 to $25,000 per year thereafter to maintain. The budget is controllable through scoping, accredited-body negotiation, multi-site sampling, and framework bundling, and the spend is best evaluated against the revenue it unblocks rather than as a pure compliance tax.
ISO 27001 Certification Cost FAQs
How much does ISO 27001 certification cost on average?
Most small to mid-sized organisations spend $15,000 to $50,000 in the first year, covering implementation, tooling, and the certification audits, with large or complex enterprises exceeding $100,000. Ongoing costs run $5,000 to $25,000 per year across surveillance audits and ISMS maintenance.
Is ISO 27001 affordable for startups and small businesses?
Yes, with a tight scope. A cloud-native startup using templates or an automation platform can certify for $10,000 to $25,000 all-in. The key decisions are limiting scope to what customers actually require and choosing a right-sized accredited certification body rather than a premium brand.
Fixed-fee readiness also keeps the implementation side predictable: Axipro’s Achievement Plan starts at $4,000 for companies under 50 employees, with the certification body’s audit billed separately.
How much does an ISO 27001 auditor charge per day?
Accredited certification bodies charge roughly $1,500 to $2,200 per audit day in the US and £1,000 to £1,500 in the UK in 2026. The number of days is calculated from ISO/IEC 27006 tables based on your in-scope headcount and complexity, so the day rate is only half of the fee equation.
Are surveillance audits cheaper than the initial audit?
Yes. Surveillance audits in years two and three typically run one third to one half the duration of the initial Stage 2 audit, which puts most SMB surveillance fees at $3,000 to $10,000 per year.
What is the cost of failing an ISO 27001 audit?
Major nonconformities require remediation plus a follow-up assessment, usually adding $1,500 to $6,000 in audit fees and one to three months of delay. The larger cost is commercial: deals and tenders waiting on the certificate stall until the follow-up closes the findings.
Are UKAS or ANAB-accredited audits more expensive?
Accredited audits cost more than unaccredited ones because accredited bodies carry oversight obligations, witnessed audits, and qualified auditor requirements. The premium is worth paying: unaccredited certificates are routinely rejected by enterprise procurement and effectively buy you nothing.
Does remote auditing reduce certification cost?
It eliminates travel and accommodation recharges and often shortens elapsed time, but the audit-day count itself is fixed by the ISO/IEC 27006 calculation, so the fee reduction is real yet modest. Remote delivery helps most for multi-site and internationally distributed scopes.
What is the cost difference between ISO 27001 and SOC 2?
The ranges overlap heavily: SOC 2 Type II reports typically cost $20,000 to $60,000 all-in, similar to ISO 27001. The structural difference is that SOC 2 requires a fresh attestation every year, while ISO 27001 runs cheaper surveillance audits in years two and three of its cycle. Companies needing both should bundle them with one audit firm and reuse the shared control evidence.
What does ISO 27001 readiness include, and what do you pay the auditor separately?
Readiness is everything before the audit: gap analysis, risk assessment, policies, control implementation, and audit preparation. The accredited certification body charges separately for the Stage 1 and Stage 2 audits, typically $5,000 to $10,000 for a small scope and $12,000 to $22,000 for a 50-person company. Axipro’s readiness starts at $4,000 for companies under 50 employees and does not include that audit fee.
What is the cheapest way for a 40-person company to get ISO 27001 policies and a Statement of Applicability?
A documentation toolkit at $500 to $2,000 is the cheapest route, provided someone internal adapts the templates to how the company actually works. Auditors spot unmodified boilerplate quickly. If nobody has the time, fixed-fee readiness removes that work: Axipro’s starts at $4,000 for companies under 50 employees and includes the policies and procedures, risk assessment, and control implementation.


