
A single VS Code extension installed by a single GitHub employee has cost the world’s largest code host roughly 3,800 of its internal repositories. GitHub confirmed the breach in a five-post thread on X on May 20, 2026, attributing the compromise to a poisoned extension that ran on the employee’s machine and gave attackers a foothold inside Microsoft’s flagship developer platform. The threat group TeamPCP, already infamous for a string of supply chain attacks across npm, PyPI, and PHP packages earlier this year, has claimed responsibility on underground forums and is reportedly asking more than $50,000 for the stolen dataset. GitHub’s own assessment is that the attacker’s claim of around 3,800 exfiltrated repositories is directionally consistent with what investigators have found so far. The company says no customer data was touched. What GitHub Disclosed GitHub broke the news in a numbered thread of five short posts on X, with no entry on the official github.blog or githubstatus.com at the time of disclosure. The company said it detected the compromise of an employee device the previous day, removed the malicious extension version from the marketplace, isolated the affected endpoint, and rotated critical secrets overnight, prioritizing the highest-impact credentials first. “Our current
Axipro, the cybersecurity and compliance consulting firm, and Kertos, the European compliance automation platform, and have entered a strategic partnership that combines software automation with hands-on implementation support for organisations navigating Europe’s expanding regulatory regime. The agreement, effective April 1, 2026, names Axipro as an implementation partner for Kertos. Customers can now buy the Kertos platform through Axipro alongside consulting, implementation support, and broader compliance service packages spanning frameworks including GDPR, NIS2, DORA, the EU AI Act, ISO 27001, and SOC 2. The partnership lands as European companies face mounting regulatory pressure. The NIS2 Directive pulled around 28,700 additional companies into scope when it replaced its predecessor in October 2024. DORA became fully applicable in January 2025, binding around 22,000 EU financial entities to a single ICT risk management framework with penalties of up to 2% of global turnover. The EU AI Act adds another layer, with compliance costs for SMEs running between €50,000 and €500,000 per organisation depending on use case. What the partnership delivers Under the agreement, Axipro sells, implements, and operates Kertos for customers as part of integrated service packages. The same partner that scopes the gap assessment, defines the control framework, and runs the implementation also
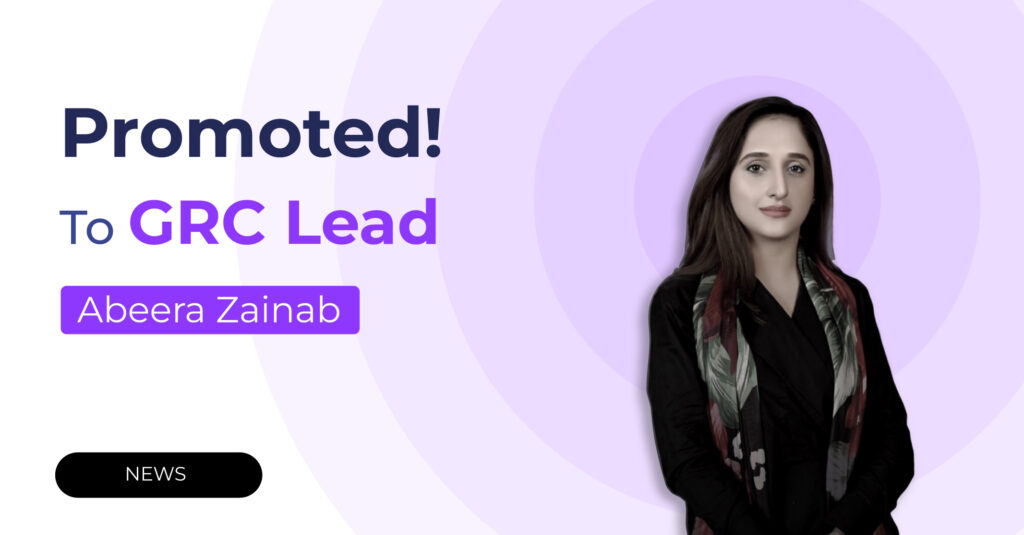
When Abeera Zainab joined Axipro in early 2024, she quickly became more than just part of the delivery team—she became a driving force behind how compliance engagements are executed across the firm.Over the past few years, her role has naturally expanded. What began as hands-on involvement in compliance delivery has evolved into leading complex, multi-framework programs across diverse client environments. Today, Abeera operates at the centre of Axipro’s GRC function—overseeing engagements that span ISO 27001, ISO 27701, SOC 2, PCI DSS, GDPR, HIPAA, ISO 42001, and DORA, often managing multiple frameworks simultaneously within a single scope. Her strength lies not just in understanding these standards, but in making them work together—bringing structure to complexity and helping organisations move toward audit readiness without unnecessary friction. This approach has translated into tangible results. Abeera has played a key role in maintaining Axipro’s 100% audit success rate across 40+ certified clients, with no failed audits to date, while consistently delivering a high level of client satisfaction.But what clients often highlight most isn’t just the outcome—it’s the experience of working with her. Even in high-pressure situations—tight timelines, evolving scopes, or complex stakeholder environments—Abeera is known for her calm, structured, and transparent approach. She brings
On April 19, 2026, Vercel confirmed attackers had reached parts of its internal systems. The entry point was an infostealer infection on an employee’s laptop at Context.ai, a third-party AI platform, two months earlier. From that single compromised machine, an attacker moved through Google Workspace OAuth, into a Vercel employee’s account, and then into Vercel environments where customer environment variables were stored. This is the shape of a modern supply-chain breach, and it is worth understanding in detail. What Vercel Has Confirmed Vercel published a short security bulletin on April 19, 2026, stating that unauthorized access had affected a limited subset of customers. The company engaged external incident response experts and notified law enforcement. Hours later, CEO Guillermo Rauch provided the attack chain on X: Context.ai was breached, a Vercel employee’s Google Workspace account was taken over through that breach, and the attacker then pivoted into Vercel’s internal environments. Incident responders from Mandiant were engaged alongside law enforcement, according to BleepingComputer’s reporting on the incident. Rauch stated that Next.js, Turbopack, and Vercel’s open-source projects had been audited and remained safe, a direct response to claims circulating on a cybercrime forum that framed the incident as a potential Next.js supply-chain disaster.
A new version of the world’s most widely adopted quality management standard is on the way. The Draft International Standard (ISO/DIS 9001) was released on 27 August 2025, and ISO member bodies voted to approve it in December 2025. Final publication is targeted for September 2026, with a three-year transition window expected to follow. Over 1.3 million organizations worldwide currently hold ISO 9001 certification. For every one of them, understanding what is changing, and what is not, matters. This guide covers the confirmed changes in the DIS, the full revision timeline, what the update means for currently certified organizations, and how to plan your transition. Whether you are managing an existing Quality Management System (QMS) or considering certification for the first time, this is what you need to know. What Is ISO 9001:2026? ISO 9001 is the international standard that defines requirements for a Quality Management System. Published by the International Organization for Standardization (ISO), it provides a framework organizations can use to consistently deliver products and services that meet customer and regulatory requirements, and to drive continual improvement. Certification to ISO 9001 is recognized in virtually every industry and country worldwide. ISO 9001:2026 is the sixth edition of the
WhatsApp us