/ ,

  / Ikponke Godwin Joins Axipro as Principal Advisor

Ikponke Godwin Joins Axipro as Principal Advisor

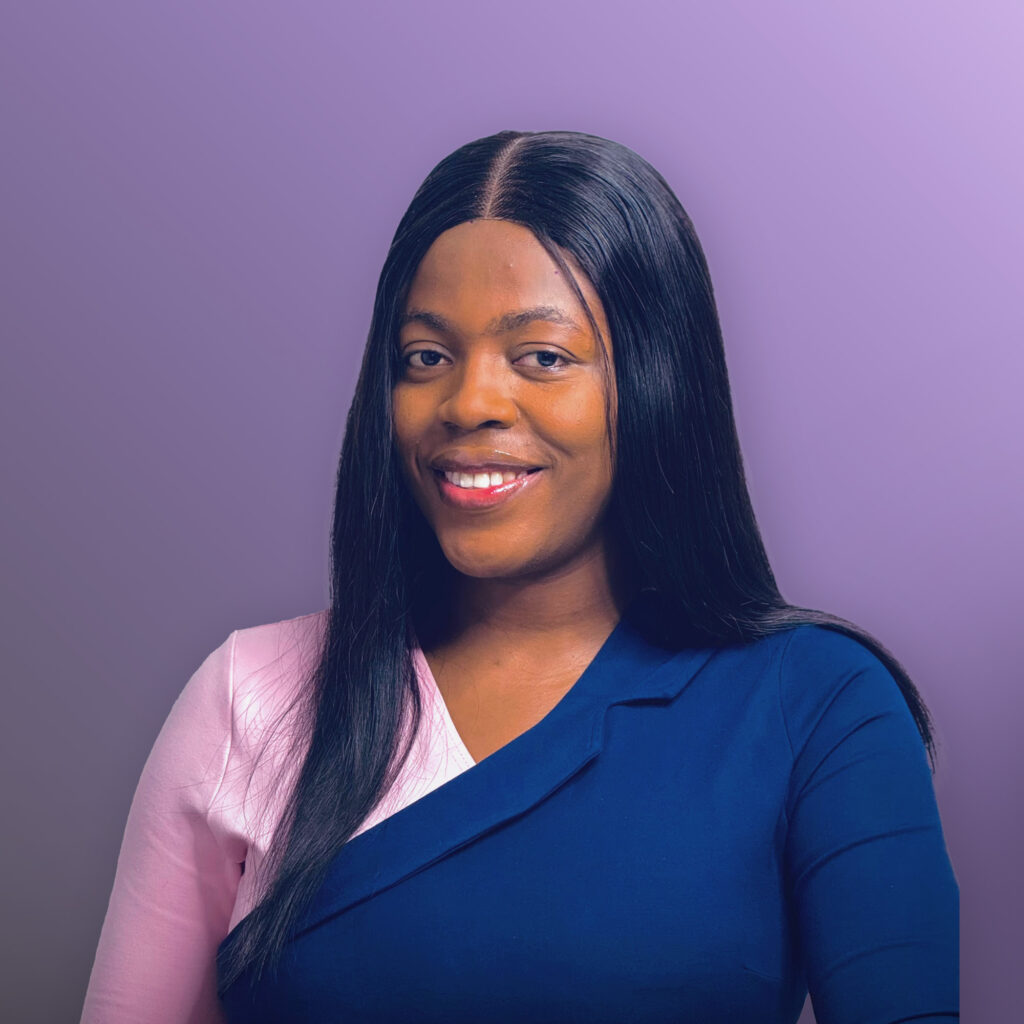
Axipro has appointed Ikponke Godwin, CISM, as Principal Advisor. She joins from EY and brings a profile that is genuinely rare in this space: deep technical security experience and mature governance expertise, built in parallel rather than one after the other.

Ikponke spent over a year at EY as Senior Cybersecurity Consultant for West Africa, advising enterprise clients across security operations, GRC, and digital transformation. Before that, nearly two years at PwC Nigeria as both Associate Cybersecurity Specialist and Penetration Tester, where she worked across vulnerability assessment, framework implementation, and technical risk analysis. Most recently, she completed a secondment at Flutterwave as GRC Analyst, where she led an enterprise gap assessment using NIST CSF 2.0, co-developed a risk-based remediation roadmap, built out risk taxonomies, and used Drata to automate compliance workflows across one of Africa’s most closely-watched fintech platforms.
That combination of offensive security work and governance programme delivery is what makes her appointment significant. Many practitioners develop in one direction or the other. Ikponke has done both, and the combination shapes how she approaches client problems: starting with what could actually go wrong, not just what the framework says should be documented.


She holds the Certified Information Security Manager (CISM) designation and has hands-on experience across penetration testing, SIEM operations, third-party risk management, and security policy development. She has also worked as a Cybersecurity Instructor, which speaks to how clearly she can communicate complex topics to teams who are not security specialists.

Ikponke on joining Axipro: “What drew me here is the combination of ambition and precision. The firm is growing fast but has not traded rigour for speed. I want to build on that.”

As Principal Advisor, Ikponke will work with enterprise and mid-market clients on complex compliance engagements, technical security assessments, and GRC transformation programmes. She is based in Lagos, Nigeria.

We’re glad to have her.

Axipro Author

Picture of Pedro Dias

Pedro Dias

Pedro has been writing online for over 10 years. With experience in all things programming, cyber security, and compliance, he is our editor-in-chief at Axipro.

Blog Highlights

Explore More Articles

A fractional CISO costs anywhere from $500 to $25,000 a month in 2026. This range might look absurd until you analyze what’s included at each level of spending, and that’s exactly what we’ll do in this article. At $500 you’re buying a compliance-led security program with a virtual CISO attached, run by a team that already knows SOC 2 and ISO 27001 well. At $25,000 you’re buying two or three days a week of a senior executive’s time and team, to run security for a company with real headcount and a board that asks hard questions. Both make sense for the right company. Buy the wrong one and you either overspend by six figures or end up short on leadership right before a breach or a failed audit. This guide covers fractional CISO pricing by model, tier, company stage and framework, compares it with the full cost of a full-time hire, and shows where Axipro’s published price of $500 per month fits. TL;DR: Fractional CISO Cost at a Glance Engagement type Typical 2026 cost Best fit Early-stage Startup compliance vCISO (Axipro Trust Assurance Plan) $500 to $850 per month, certification billed separately Startups and SaaS teams that need SOC 2

Every PHP installation that serves web requests has been open to unauthenticated remote code execution since 2004. On October 21, 2026, the PHP project shipped the fix, the NSA told organizations to take unpatchable systems offline, and four European governments pulled their own websites to patch. Your security team is handling the interpreter. This article is for the person who has to explain the response to an auditor. php2shell is a security incident, and it’s also a live test of the vulnerability management, asset inventory, incident response and vendor management controls you attested to in your last audit. Every framework Axipro works with has a specific expectation for what you do in the next 72 hours and what evidence you keep. Below is the mapping, framework by framework: the control reference, what you need to do, and the artifact that satisfies it. What php2shell Is, in One Minute Two flaws in PHP core, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS v4.0, let an unauthenticated attacker run code on the server. The first is triggered through out-of-memory handling that interrupts PHP while request data is only partially initialized. The second exploits request-owned internal state that survives after its memory has

Essential PCI DSS Controls
This blog explores PCI DSS controls, their importance, and key compliance requirements. We also discuss how businesses can effectively implement security measures.