The EU AI Act names recruitment AI as high-risk. Annex III explicitly lists AI systems used for recruitment, candidate selection, and employment decisions, which pulls CV screeners, video interview platforms, and assessment tools into the most demanding compliance regime the Act contains. The original compliance date for these systems was August 2, 2026. In June 2026, the EU’s Digital Omnibus moved the deadline to December 2, 2027, a 16-month extension that has led many HR and talent teams to shelve the topic entirely.
That’s a mistake, for two reasons.
- First, one rule that directly affects recruitment technology is already in force: the ban on emotion recognition in the workplace has applied since February 2, 2025, and it catches features still shipping in some video interview products today.
- Second, the deferred obligations didn’t shrink. Conformity assessments, human oversight design, bias monitoring, and documentation all still arrive in full, and the practical work of auditing a recruitment stack, renegotiating vendor contracts, and training hiring teams routinely takes a year or more.
Here’s what the EU AI Act actually requires of employers and vendors using recruitment tools, on the timeline that now applies.
Let Axipro help you build a business continuity plan that's practical, compliant, and audit-ready.
Schedule Your Free Assessment Today
Why Recruitment Tools Are Classified as High-Risk Under the EU AI Act
Definition of High-Risk AI Systems in Hiring
The Act takes a list-based approach. Annex III, point 4, designates as high-risk any AI system intended for the recruitment or selection of natural persons, including placing targeted job advertisements, analyzing and filtering applications, and evaluating candidates. The same point covers AI used for decisions on promotion, termination, task allocation, and monitoring of workers, so the classification follows the tool through the entire employment lifecycle, not just the hiring funnel.
The reasoning is straightforward: hiring decisions shape access to livelihoods, and algorithmic discrimination in hiring is well documented. The European Commission’s regulatory framework for AI treats employment as one of the areas where an AI error or bias causes serious harm to fundamental rights. That’s the test for the high-risk tier.
Types of Recruitment Tools Affected
In practice, the high-risk classification captures most of the modern recruitment stack: CV and resume screeners that rank or filter applicants, video interview platforms that score responses or delivery, psychometric and skills assessment tools that produce scores feeding a hiring decision, sourcing and matching algorithms that decide which candidates a recruiter sees, and programmatic job ad targeting systems that determine who sees a vacancy at all.
If the system’s output materially influences who advances and who does not, assume high-risk until proven otherwise.
Important: Emotion recognition is not high-risk in the workplace. It is prohibited. Article 5 bans AI systems that infer emotions of people in the workplace (outside narrow medical and safety cases), and that ban has applied since February 2025 with the Act’s top penalty tier attached. If your video interview vendor markets “engagement scoring” or “sentiment analysis” of candidates, that feature needs to be switched off for EU hiring now, not in 2027.
Recruitment Tools That May Fall Outside High-Risk Classification
Not everything in the HR stack qualifies. The Act carves out systems performing narrow procedural tasks that do not materially influence decision outcomes. An applicant tracking system that stores applications, schedules interviews, and sends templated emails is a database with a workflow, not a high-risk AI system. The same goes for tools that transcribe interviews without scoring them, deduplicate candidate records, or generate first drafts of job descriptions for a human to edit.
The line is decision influence: the moment a tool ranks, scores, filters, or recommends candidates, it crosses into Annex III territory. Deployers who rely on an exemption must be able to document that assessment, so “we decided it doesn’t count” needs to exist on paper.
Extraterritorial Scope: Which Employers Are Covered
The Act applies to providers placing AI systems on the EU market and to deployers established in the EU, but it also reaches further: it covers providers and deployers located outside the EU where the output of the system is used in the EU. For recruitment, the consequence is blunt. A US or UK company with no EU entity that uses an AI screener to filter applicants for roles based in Berlin or Dublin, or that screens candidates located in the EU, is using the system’s output in the Union. Brexit doesn’t move UK employers out of scope when they hire into or from the EU.
Providers vs. Deployers of Recruitment AI Tools
The Act splits obligations between the provider (the vendor that develops the tool and places it on the market) and the deployer (the employer using it). Most employers are deployers, and deployer obligations are lighter but real. One common trap: an employer that substantially modifies a high-risk system, or puts its own name on it, can be reclassified as a provider and inherit the full provider stack. Heavy customization of a screening model, or fine-tuning it on your own hiring data, can be enough to trigger this.
Key Obligations for Employers Using AI Recruitment Tools
Human Oversight in Automated Hiring Decisions
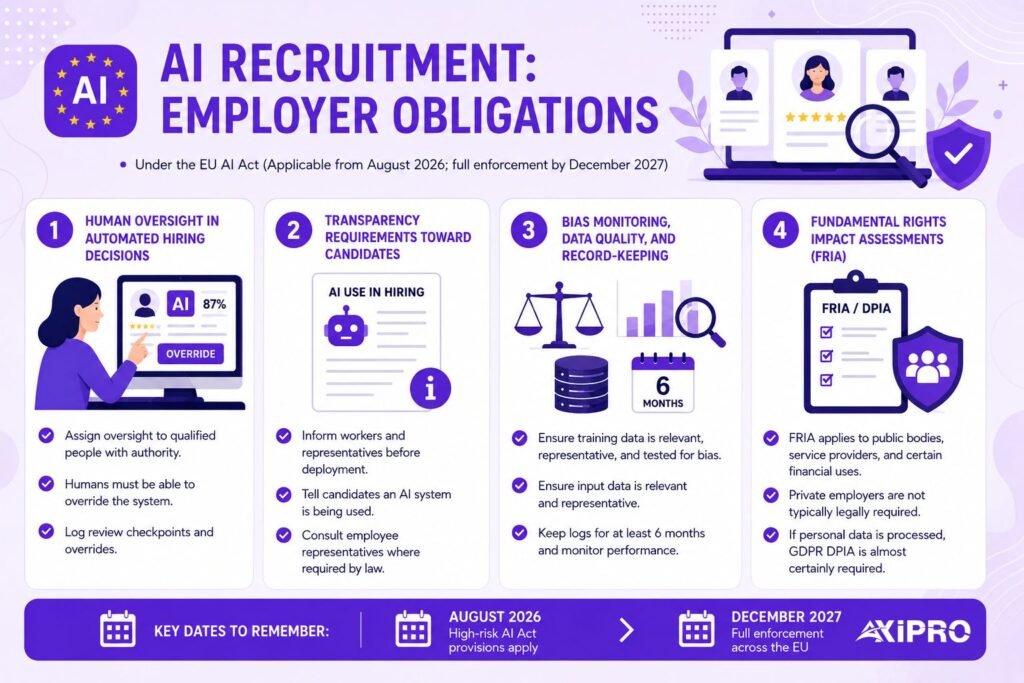
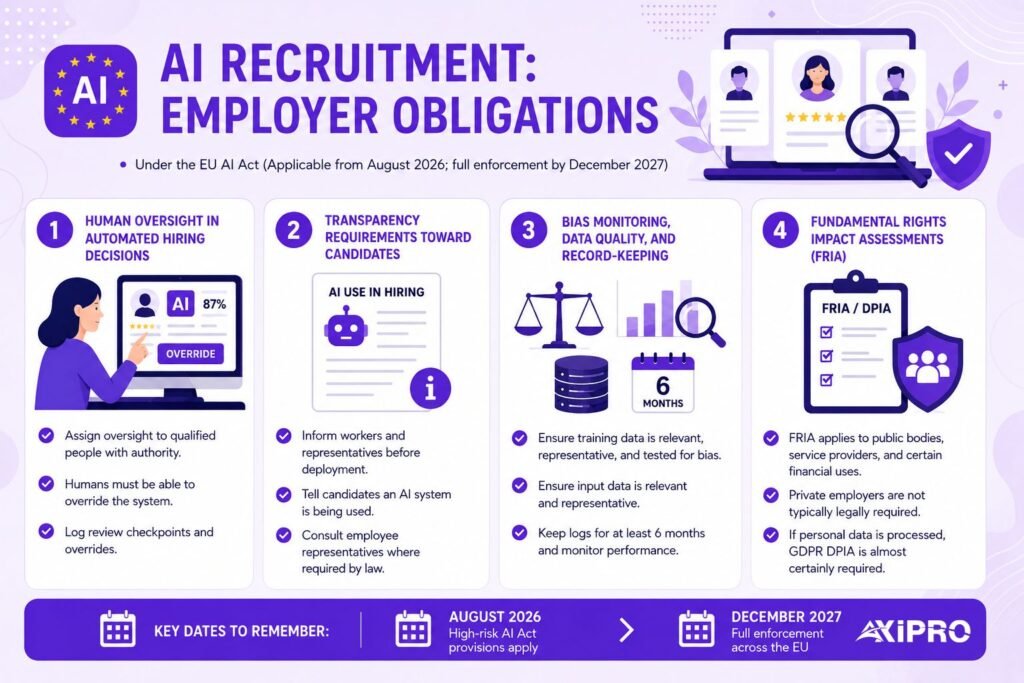
Deployers must assign oversight of the system to people with the competence, training, and authority to intervene. That last word matters. A recruiter who rubber-stamps whatever the ranking algorithm produces, because nobody has time to review 800 rejected CVs, doesn’t count as oversight. Regulators and courts will look at whether the human could genuinely override the system and whether they ever did. Designing review checkpoints where a person can meaningfully change the outcome, and logging when they do, is the core of compliant deployment.
Transparency Requirements Toward Candidates
Employers must inform workers and their representatives before putting a high-risk AI system into use at work, and candidates subjected to such a system must be told it is being used. In countries with works councils, such as Germany, this obligation lands on top of existing co-determination rights, so employee representatives may need to be consulted before the tool goes live rather than just told afterward. Burying an AI disclosure in a privacy policy paragraph is unlikely to survive scrutiny.
Bias Monitoring, Data Quality, and Record-Keeping
Providers carry the primary data governance duties, including training data that is relevant, representative, and examined for bias. Deployers must ensure the input data they feed the system is relevant and sufficiently representative for its purpose, keep the automatically generated logs for at least six months, and monitor performance in live use. If your candidate pool in a given market differs sharply from what the tool was built on, that is a deployer problem, not just a vendor one.
Fundamental Rights Impact Assessments (FRIA)
The FRIA obligation in Article 27 applies to deployers that are public bodies or private entities providing public services, plus certain financial use cases. A typical private employer running an AI screener isn’t legally required to produce a FRIA. Two caveats: public-sector employers are covered, and where the tool processes personal data, a Data Protection Impact Assessment under the GDPR is almost certainly required anyway. Most organizations that get this right run a single combined assessment covering both.
Obligations for Providers and Vendors of AI Recruitment Software
Vendors face the full high-risk regime:
- a risk management system across the product lifecycle,
- data governance,
- technical documentation proving compliance,
- a third-party or internal conformity assessment before market placement, CE marking,
- registration in the EU’s high-risk AI database,
- and post-market monitoring with incident reporting.
For employers, this paperwork is your due diligence checklist. A vendor who cannot show you their conformity documentation by mid-2027 is telling you something about your own December 2027 exposure.
Insider Note: The vendor conversation to watch for is “we’re just an ATS, the Act doesn’t apply to us.” Sometimes that’s true. But many platforms marketed as applicant tracking systems have added AI ranking, matching, or “best fit” features over the past three years, and those features change the classification even if the core product predates them. Ask specifically which features use AI to score, rank, or filter candidates, and get the answer in writing.
Implementation Timeline for Recruitment AI Compliance
The timeline shifted materially in mid-2026. The Digital Omnibus, given final approval by the Council on June 29, 2026, replaced the original August 2, 2026 date for standalone Annex III systems. According to analysis by Gibson Dunn, high-risk obligations for Annex III systems, including recruitment tools, now apply from December 2, 2027, with AI embedded in regulated products following on August 2, 2028. The dates that matter for hiring teams:
- February 2, 2025: prohibited practices in force, including the workplace emotion recognition ban. Already live.
- August 2, 2025: general-purpose AI model obligations in force. Already live.
- August 2, 2026: most Article 50 transparency obligations in force, including chatbot disclosure for candidate-facing assistants. Already live.
- December 2, 2027: full high-risk obligations apply to standalone Annex III systems, including recruitment and employment tools.
Law firm guidance throughout the negotiation, including from DLA Piper, has been consistent on one point: the deferral moved the deadline and nothing else. No obligation was removed or softened for employment AI.
Worth Knowing: Grandfathering rule for High-risk systems
There is a grandfathering rule for high-risk systems already placed on the market before the deadline, but it resets the moment the system is substantially modified. Recruitment AI vendors ship model updates constantly, so treating grandfathering as a durable shield for a SaaS screening tool is optimistic at best.
Penalties for Non-Compliant Use of Recruitment Tools
Article 99 sets three fine tiers. Use of a prohibited practice, such as workplace emotion recognition, carries fines up to €35 million or 7% of global annual turnover, whichever is higher. Non-compliance with high-risk obligations, the tier most relevant to recruitment AI, reaches €15 million or 3% of turnover. Supplying misleading information to authorities carries up to €7.5 million or 1%. SMEs benefit from a proportionality rule where the lower of the two amounts applies, but a fine calculated on turnover is still serious money for a growth-stage company.
The fine is rarely the whole cost, though. A finding of non-compliant AI hiring invites discrimination claims from rejected candidates, works council disputes, orders to withdraw the system (mid-hiring-cycle, with a pipeline built on it), and the kind of press coverage that makes the next thousand candidates think twice. GDPR enforcement history suggests regulators reserve the harshest penalties for organizations with no documentation and no good-faith effort, and that pattern should factor into any plan that starts the work in late 2027.
Interaction with GDPR and Other EU Employment Laws
The AI Act does not replace the GDPR; the two apply in parallel, and for recruitment the GDPR has been the binding constraint since 2018. Article 22 GDPR gives candidates the right not to be subject to a decision based solely on automated processing that significantly affects them. A fully automated rejection fits that description. Candidates also hold access, rectification, and erasure rights over their application data, and the right to meaningful information about the logic involved in automated decisions.
EU anti-discrimination law adds a third layer. The equal treatment directives prohibit indirect discrimination, and an algorithm that disadvantages a protected group produces liability regardless of intent. The AI Act’s bias testing and logging obligations effectively create the evidence trail that discrimination claims will be argued from, in both directions: good records are a defense, and missing records are an admission.
How to Audit Your Recruitment Tool Stack for EU AI Act Compliance
Start with an inventory, because most organizations do not have one. In our compliance work, the most common gap isn’t a defiant vendor or a rogue algorithm. It’s that HR bought the tool two years ago, nobody mapped which features use AI, and nobody can produce the vendor’s documentation when asked.
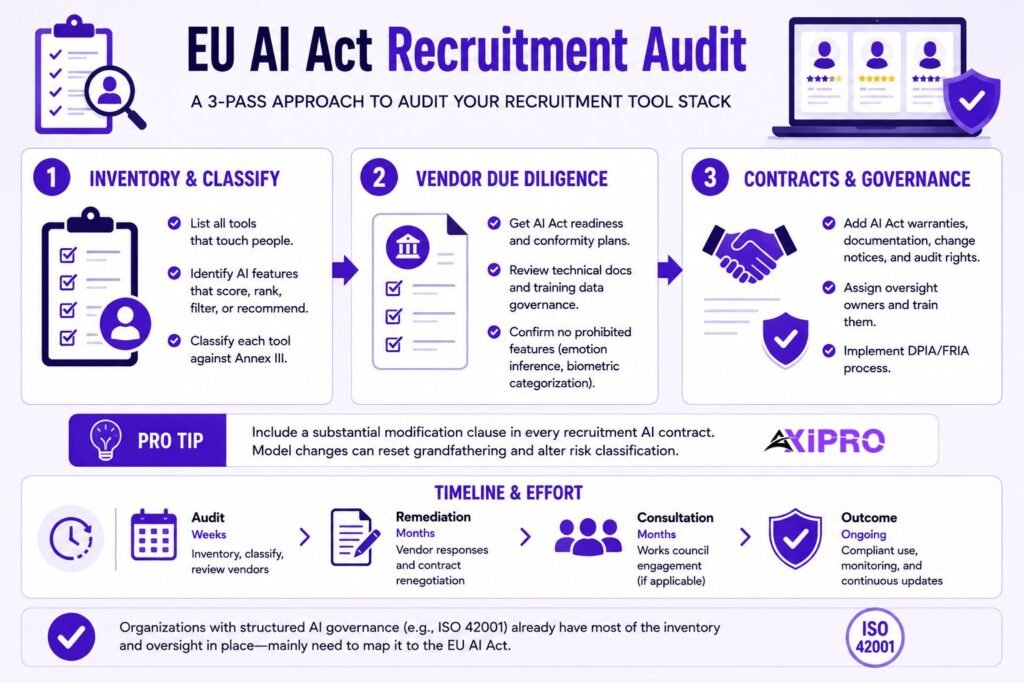
A workable audit runs in three passes:
- Inventory and classify. List every tool touching candidates or employees, flag every feature that scores, ranks, filters, or recommends people, and classify each against Annex III.
- Vendor due diligence. Request each vendor’s AI Act readiness statement, conformity assessment plans, technical documentation summary, training data governance description, and confirmation that no prohibited features (emotion inference, biometric categorization) are active for EU use.
- Contracts and governance. Add AI Act warranties, documentation delivery obligations, notification of substantial modifications, and audit rights to vendor contracts at the next renewal. Internally, assign oversight owners, train them, and stand up the DPIA/FRIA process.
For budgeting purposes, a focused audit of a typical mid-size recruitment stack (an ATS plus two to four AI-enabled tools) is a matter of weeks, not months, but remediation is where the calendar burns: vendor responses, contract renegotiation, and works council consultation each add months of elapsed time.
Organizations already running structured AI governance, for example under ISO 42001, have most of the inventory and oversight machinery in place already and mainly need to map it to the Act’s specific articles.
Pro Tip: Substantial Modification Clause
Put a substantial modification clause in every recruitment AI contract renewed from now on. If the vendor makes a substantial change to the model, you need to know, because it can reset grandfathering and change your risk classification. Vendors won't volunteer this; the contract has to make them.
Practical Steps to Prepare Your Recruitment Process
Sequence the work backward from December 2027.
- Quarter one: inventory, classification, and killing any prohibited features immediately.
- Quarters two and three: vendor due diligence and contract updates, candidate-facing transparency language, and a combined DPIA covering AI-specific risks.
- Quarters four onward: human-in-the-loop process design, training for recruiters and hiring managers, log retention setup, and a dry-run review of one live hiring campaign end to end.
Teams that treat the first half of 2027 as the deadline, rather than December, leave room for the vendor who answers slowly and the works council that meets quarterly.
The talent market makes early movement more valuable. Axipro’s 2026 study of AI governance hiring across Europe found companies hiring roughly seven AI builders for every governance professional, which means the people who can run this compliance work are scarce and getting scarcer. Employers who need external EU AI Act compliance support should scope it before the 2027 crunch pushes prices up.
Let Axipro help you build a business continuity plan that's practical, compliant, and audit-ready.
Schedule Your Free Assessment Today
Conclusion: Turning Compliance Into a Competitive Recruitment Advantage
The EU AI Act treats recruitment tools as high-risk because hiring decisions change lives, and the December 2027 deadline is a reprieve on paperwork, not on principle. The emotion recognition ban already applies, transparency duties began in August 2026, and the full high-risk regime arrives with no obligations removed.
Employers who inventory their stack, pressure-test their vendors, and build genuine human oversight now will spend 2027 refining a working system instead of triaging one.
And in a market where candidates increasingly ask how they are being screened, being able to answer clearly is a recruiting asset in its own right.
Frequently Asked Questions
Are ATS (Applicant Tracking Systems) considered high-risk AI?
Not by default. An ATS that stores applications and manages workflow performs narrow procedural tasks and falls outside the high-risk category. It becomes high-risk when it includes AI features that rank, score, filter, or match candidates, which many modern ATS platforms now do. Audit the features, not the product label.
Can employers still use AI video interview tools in the EU?
Yes, as high-risk systems with full obligations attached: human oversight, candidate disclosure, logging, and a compliant vendor. What they can’t do is infer candidates’ emotions. Emotion recognition in the workplace has been prohibited since February 2025, so any sentiment or engagement scoring feature must be disabled for EU hiring.
Do candidates have the right to opt out of AI screening?
The AI Act itself grants disclosure rights rather than an opt-out. The stronger right comes from Article 22 GDPR: candidates cannot be subject to a solely automated decision with significant effects, which in practice forces meaningful human involvement in rejections. Combined with access and objection rights over their data, a candidate can effectively demand human review.
What happens if an AI recruitment vendor is non-compliant?
The vendor faces provider-tier fines of up to €15 million or 3% of turnover, but the employer isn’t insulated. Deployers have independent obligations, and using a system you knew or should have known lacked conformity documentation is your own compliance failure. This is why vendor due diligence and contractual warranties belong in every renewal between now and December 2027.
Does the EU AI Act apply to internal mobility and promotion tools?
Yes. Annex III covers AI used for decisions affecting work-related relationships, including promotion, termination, task allocation, and performance monitoring. A tool that recommends internal candidates for advancement carries the same high-risk obligations as an external hiring screener.