

Most SOC 2 preparation effort goes into access controls, encryption, and vendor reviews. Then the auditor’s first evidence request arrives, and item one has nothing to do with technology: show us your board charter, your meeting minutes, and proof that your board operates independently from management. That’s CC1.2, and it causes more last-minute scrambling than almost any technical control in the framework.
This guide explains what CC1.2 requires, provides a board charter template with sample language that auditors accept, and covers the situation most startups actually face: satisfying the criterion without a traditional board of directors.
What Is a SOC 2 Board Charter and Why It Matters for CC1.2
A board charter is a formal document that defines your board’s purpose, composition, authority, meeting procedures, and oversight responsibilities. Outside of compliance, it’s a corporate governance tool and a good idea in general for companies with shareholders.
Inside a SOC 2 audit, it’s the primary design evidence for CC1.2, the criterion that asks whether an independent body oversees management and the internal control environment.
The charter matters because CC1.2 is one of the few criteria where the control is a document plus behavior. The charter establishes the structure. The auditor then tests whether the structure operates: did the board actually meet, did it review the security program, did it challenge management? A beautifully drafted charter with no meeting minutes behind it fails just as surely as no charter at all. If you’re earlier in your preparation, our complete SOC 2 guide covers how the full audit fits together.
Understanding CC1.2: The Board Independence Criterion
CC1.2 is part of the Trust Services Criteria published by the AICPA (American Institute of Certified Public Accountants). The criterion requires that the board of directors, in the AICPA’s words, “demonstrates independence from management and exercises oversight” of how internal control is developed and how it performs. That sentence hides two separate tests.
- Independence means the board isn’t just management wearing a second hat.
- Active oversight means the board actually reviews and challenges the control environment instead of existing on paper. Plenty of companies pass one and fail the other.
How CC1.2 Fits Within the CC1 Control Environment
The Common Criteria run from CC1 through CC9, and the CC1 series covers the control environment: the governance and people layer everything else rests on. CC1.1 addresses integrity and ethical values, CC1.2 addresses board independence and oversight, CC1.3 covers organizational structure and reporting lines, CC1.4 covers competence and hiring, and CC1.5 covers accountability. CC1.2 is the layer that makes the other four credible. A code of conduct means little if nobody independent of management ever checks whether leadership follows it.
The COSO Principle 2 Connection
The Trust Services Criteria are built directly on the COSO Internal Control—Integrated Framework and its 17 principles. CC1.2 maps to COSO Principle 2, which carries four points of focus: the board establishes oversight responsibilities, applies relevant expertise, operates independently of management, and provides oversight of the system of internal control. Those four phrases are worth memorizing, because they’re effectively the outline of a good board charter.
Why Auditors Prioritize Board Charter Evidence
Auditors test the control environment first because failures there cascade. If governance is weak, every other control claim gets harder to trust: who approved the risk assessment, who reviewed the incident report, who held management accountable when a control slipped? An exception at CC1.2 tells the auditor that nobody independent was watching, and they’ll read the rest of your evidence with that in mind. That’s why board charter requests sit near the top of almost every evidence list.
Worth Knowing: Points of Focus
Points of focus are not pass/fail requirements. The AICPA describes them as characteristics that assist evaluation, and the 2022 revisions changed points of focus without changing any criteria. In practice, though, they function as the auditor's mental checklist, so drafting your charter against them is the safest move.
What Auditors Actually Look For in a Board Charter
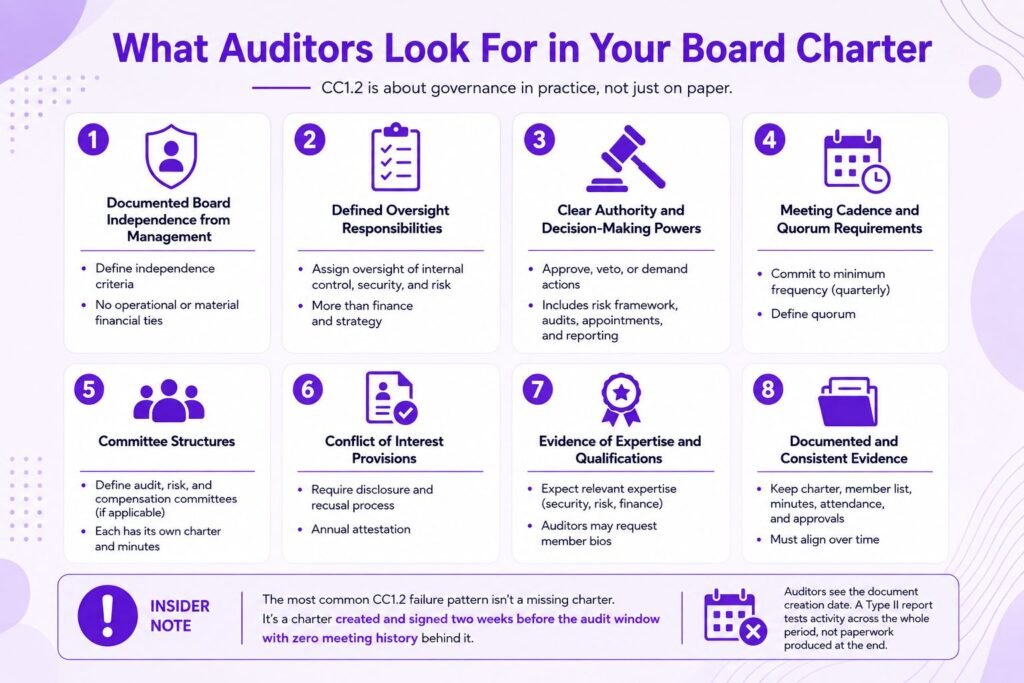
Auditors don’t grade prose style. They scan for specific, verifiable commitments. Here’s what they check, roughly in order.
Documented Board Independence from Management
The charter must state how many members are independent, define what independence means (no operational role, no material financial relationship beyond board compensation or equity), and describe how independence is maintained. “The board includes members independent of management” without a definition is boilerplate; auditors want criteria they can test against actual member profiles.
Defined Oversight Responsibilities
This is the heart of CC1.2. The charter should explicitly assign the board oversight of internal control, information security, and risk management. If the charter only mentions financial oversight and strategy, it wasn’t written with SOC 2 in mind, and the auditor will notice the gap.
Clear Authority and Decision-Making Powers
What can the board approve, veto, or demand? Typical provisions include approving the risk management framework, reviewing audit results, approving executive appointments, and requiring management to report on control deficiencies. Authority without teeth reads as decorative.
Meeting Cadence and Quorum Requirements
The charter should commit to a minimum meeting frequency (quarterly is the common standard) and define a quorum. This clause matters more than founders expect, because it’s the one auditors test directly against your calendar: if the charter says quarterly and you met twice last year, that’s an exception you wrote for yourself.
Committee Structures
Larger organizations delegate through audit, risk, and compensation committees, each with its own mini-charter. Smaller companies don’t need committees, but if your charter mentions them, they must exist and produce minutes. Never copy a public-company template with a phantom audit committee.
Conflict of Interest Provisions
A disclosure and recusal process for conflicts, usually paired with an annual attestation. This clause supports the independence claim: independence isn’t a one-time status, it’s maintained through disclosed and managed conflicts.
Evidence of Board Member Expertise and Qualifications
COSO’s “applies relevant expertise” point of focus means the board should be able to ask probing questions about security and risk, not just finance. Charters increasingly include a skills expectation clause, and auditors may request member bios to corroborate it.
Insider Note: The most common CC1.2 failure pattern isn’t a missing charter. It’s a charter created and signed two weeks before the audit window with zero meeting history behind it. Auditors see the document creation date, and a Type II report tests activity across the whole period, not paperwork produced at the end.
Essential Sections to Include in Your SOC 2 Board Charter Template
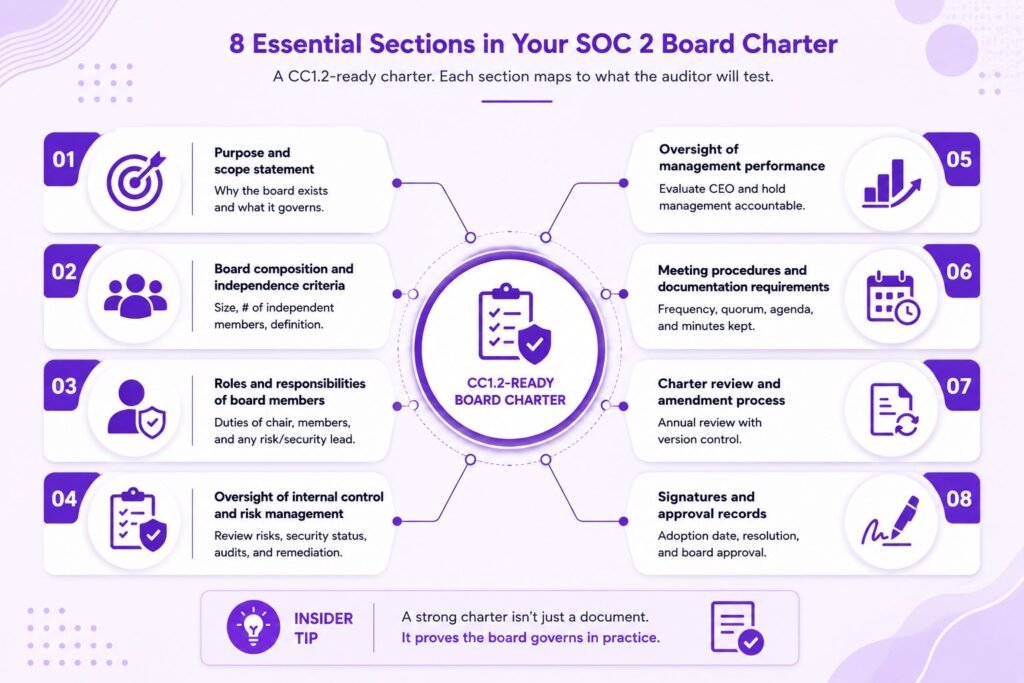
A CC1.2-ready charter needs eight sections. Each maps to something the auditor will test.
- Purpose and scope statement. Why the board exists and what it governs, explicitly including oversight of internal control and the security program.
- Board composition and independence criteria. Size, the number of independent members, and a working definition of independence.
- Roles and responsibilities of board members. Duties of the chair, members, and any designated security or risk lead, including fiduciary duty language.
- Oversight of internal control and risk management. The board’s obligation to review the risk assessment, security program status, audit results, and remediation of deficiencies.
- Oversight of management performance. How the board evaluates the CEO and holds management accountable for control failures, which is the independence test in action.
- Meeting procedures and documentation requirements. Frequency, quorum, agenda-setting, and a commitment that minutes are taken, approved, and retained.
- Charter review and amendment process. An annual review clause with version control, so the document has a paper trail showing it actually stays alive.
- Signatures and approval records. Adoption date, approval resolution, and signatures or documented board approval in minutes.
Free SOC 2 Board Charter Template (Downloadable)
The template below is deliberately compact. Auditors prefer a two-page charter your board actually follows over a fifteen-page document copied from a public company. You can read the full text here, or download the editable board charter template (.docx) to adapt directly:
Replace bracketed items, delete anything that doesn’t reflect reality, and have the board formally adopt it in a documented meeting.
BOARD CHARTER OF [COMPANY LEGAL NAME] · Adopted [date] · Version [1.0]
- Purpose and scope. The Board of Directors (the “Board”) of [Company] provides independent oversight of management, corporate strategy, risk management, and the design and performance of the Company’s system of internal control, including its information security and compliance programs.
- Composition and independence. The Board consists of [number] members, of whom at least [number] are independent. A member is independent if they hold no operational or employment role at the Company and have no material financial relationship with it other than board compensation or equity ownership. Members annually confirm their independence status in writing.
- Roles and responsibilities. Members act in the best interests of the Company consistent with their fiduciary duties, prepare for and attend meetings, and maintain confidentiality. The Chair sets agendas, ensures minutes are recorded and approved, and facilitates independent judgment in discussions.
- Oversight of internal control and risk management. The Board reviews, at least [quarterly], management’s reports on the information security program, the risk assessment and risk treatment plans, results of internal and external audits, significant incidents, and the remediation status of identified control deficiencies. The Board may direct management to take corrective action and require follow-up reporting.
- Oversight of management. The Board evaluates the performance of the [CEO/executive team] at least annually, including performance against security and compliance objectives, and approves the appointment or removal of executive officers.
- Meetings and documentation. The Board meets at least [four] times per year. A quorum is [a majority] of members. Minutes recording attendance, matters reviewed, decisions, and action items are prepared for every meeting, approved at the following meeting, and retained for at least [seven] years.
- Conflicts of interest. Members disclose actual or potential conflicts as they arise and annually in writing, and recuse themselves from related deliberations and decisions. Disclosures and recusals are recorded in the minutes.
- Review and amendment. The Board reviews this charter at least annually and records its reapproval or amendment, with version and date, in the minutes. Amendments require approval by [a majority] of the Board.
Approved by resolution of the Board on [date]. [Signature blocks or reference to adoption minutes]
How to Customize the Template for Your Organization
Only promise what you’ll actually do. If quarterly meetings are unrealistic, write “at least three times per year” and hit it, because every unfulfilled promise in the charter becomes a potential exception. Match the document to your legal reality too: an LLC managed by members should reference its operating agreement and governing body rather than inventing a board that doesn’t legally exist. And strip out any committee language unless the committees are real. A phantom audit committee is one of the fastest ways to lose an auditor’s benefit of the doubt.
Sample Language Auditors Accept
For the oversight clause, language along these lines works because it’s specific and testable:
At each regular meeting, management shall report to the Board on the status of the information security program, material changes to the risk assessment, significant incidents, and the remediation status of known control deficiencies. The Board shall review and challenge these reports and document its review in the minutes.
Notice the verbs: report, review, challenge, document. Each one generates evidence. Vague alternatives like “the board supports a strong culture of security” generate nothing an auditor can test.
Supporting Evidence Auditors Request Alongside the Charter
The charter is design evidence. Operating evidence proves the design ran. Expect requests for board meeting minutes covering the audit period, showing security and internal control on the agenda rather than just fundraising and product. Alongside those, auditors want attendance records (usually captured in the minutes, which prove you hit quorum) and independence attestations: annual confirmations from independent members that no disqualifying relationships exist.
If your charter establishes committees, be ready to produce committee reports showing they met and reported to the full board. Finally, expect a request for annual charter review documentation, a minuted agenda item or resolution showing the charter was reviewed and reapproved or amended.
Pro Tip: Internal control and Security Program Review
Put a standing item called “Internal control and security program review” on every board agenda and set the meetings as recurring calendar events for the entire audit window now. Minutes written against a standing agenda item generate CC1.2 evidence automatically, and you'll never reconstruct oversight after the fact, which auditors can usually detect anyway.
Common Mistakes That Cause CC1.2 Exceptions
Five patterns account for most CC1.2 findings, and most of them come down to a gap between what the charter says and what the company did.
- Generic or boilerplate language is the most obvious one. A downloaded public-company charter referencing shareholders, three committees, and NYSE listing rules doesn’t fit a 30-person SaaS company, and it signals the document is decorative. Auditors read a lot of charters. They can tell.
- Missing meeting evidence is the most common. The charter promises quarterly meetings; the company can produce minutes for one, and in a Type II every gap in the cadence during the window is an exception you wrote for yourself.
- Undocumented independence shows up constantly at startups: every board member is a founder or executive, and nothing in the file explains how oversight of management works regardless. Related to it is undefined oversight of management, where the charter covers strategy and finance but never says the board reviews internal control, security, or management performance. That’s the exact subject of CC1.2, so its absence is hard to miss.
- Finally, no review cadence or version control. A charter last touched four years ago, with no review clause and no record of reapproval, undermines the whole claim that governance is active rather than archived.
Board Charter Requirements for Startups Without a Traditional Board
Here’s the honest answer most vendors dodge: plenty of companies pass SOC 2 without a conventional independent board, but nobody gets to skip CC1.2. Security is mandatory in every SOC 2 audit; all nine Common Criteria come with it, and CC1.2 is one of them. What flexes is the structure that satisfies it. COSO’s own guidance recognizes that smaller entities may achieve board oversight through different governance arrangements, and experienced auditors apply that flexibility.
Advisory Board Alternatives
The most common substitute is an advisory board or governance committee that includes at least one or two members with no operational role: an investor, an experienced outside advisor, a fractional CISO acting in a governance capacity. Give it a charter using the same template above, meet quarterly, keep minutes, and have it genuinely review the security program. The label matters less than the independence and the paper trail.
Founder-Led Governance Documentation
If even an advisory board isn’t feasible, the fallback is a formally chartered management oversight function with documented compensating factors: a standing governance meeting with fixed agenda and minutes, an external party (investor or advisor) receiving and reviewing security reporting, and clear escalation and accountability rules. This is the weakest position of the three and the one where auditor acceptance varies most.
When Auditors Accept Substitute Governance Structures
Important: Auditor acceptance of substitute structures is a judgment call, and different CPA firms draw the line in different places. Agree on your governance structure with your auditor during the readiness or scoping phase, in writing, before the observation window opens. Discovering during fieldwork that your auditor expected an independent member is the expensive way to learn this.
How to Implement Your Board Charter Before the Audit
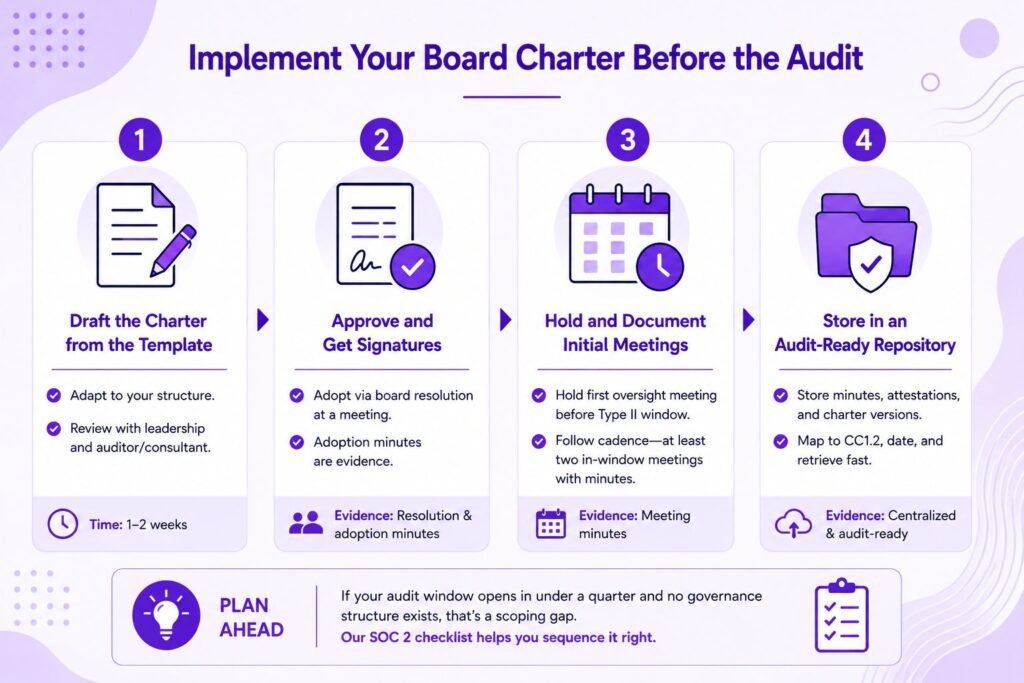
The charter itself takes a week. The evidence takes months, which is why timing drives everything here. A realistic sequence:
Step 1: Draft using the template. Adapt the template above to your actual structure. One or two review cycles with leadership and, ideally, your auditor or readiness consultant. Budget one to two weeks.
Step 2: Get board approval and signatures. Adopt the charter through a documented resolution at a board meeting. The adoption minutes are themselves evidence.
Step 3: Schedule and document initial meetings. Hold the first oversight meeting before your Type II window opens, then follow the charter’s cadence. For a six-month window on a quarterly cadence, that means at least two in-window meetings with minutes.
Step 4: Store evidence in an audit-ready repository. Minutes, attestations, and charter versions belong in your GRC platform or evidence folder, mapped to CC1.2, dated, and retrievable in minutes rather than days.
Work backward from your audit date. If your window opens in under a quarter and no governance structure exists yet, that’s a scoping conversation, and it’s exactly the kind of sequencing our SOC 2 compliance checklist is built to prevent.
Board Charter Best Practices for SOC 2 Type II
Type II changes the question from “does the structure exist” to “did it run for the entire period.” That mostly means discipline about evidence. Every scheduled meeting gets held, minuted, and filed within days, because reconstructed minutes have a distinctive smell and auditors have seen plenty of them. Nobody enjoys writing minutes. Write them anyway.
The minutes also need to show a board that reacts to real inputs, not one that rubber-stamps a slide. An incident review, a change to the risk register, a pentest result, follow-ups on remediation items from the last meeting: that’s what continuous oversight looks like on paper. And the same rhythm pays off elsewhere in the audit. Board review of the risk assessment supports CC3, review of monitoring reports supports CC4, and the reporting lines the charter establishes support CC1.3, so one governance habit feeds evidence across the five Trust Services Criteria categories.
CC1.2 rewards companies that treat governance as an operating habit rather than an audit artifact. A short, honest charter, a quarterly meeting that actually reviews security, and minutes filed on time will pass. A polished template with no life behind it won’t. If you’d rather compress the whole process, structure included, Axipro’s SOC 2 compliance services take companies from no governance documentation to audit-ready, with charter drafting, meeting cadence design, and evidence mapping handled as part of readiness.
Frequently Asked Questions
Is a formal Board of Directors required to pass CC1.2?
No. CC1.2 requires independent oversight of management and internal control, not a specific legal structure. Corporations typically have boards anyway, but LLCs and early-stage companies can satisfy the criterion through an advisory board, governance committee, or documented oversight function, provided the arrangement is chartered, independent where possible, and evidenced by minutes.
Can an advisory board satisfy SOC 2 CC1.2 requirements?
Usually, yes. Most auditors accept an advisory board or governance committee that includes members without operational roles, follows a charter, meets on a defined cadence, and documents its review of the security program. Confirm the structure with your specific auditor during scoping, because acceptance thresholds vary between firms
How often should the board charter be reviewed?
Annually. Include a review clause in the charter itself, put the review on a board agenda once a year, and record the reapproval or amendment in the minutes with a version number and date. The review record is evidence auditors specifically request.
What board meeting frequency do auditors expect?
Quarterly is the de facto standard, and it’s what most charters commit to. Auditors primarily test your actual cadence against your charter’s promise, so a charter that commits to three meetings per year and delivers three is safer than one that promises quarterly and delivers two. For a Type II, meetings must occur within the observation window.
How does CC1.2 differ from CC1.1 and CC1.3?
CC1.1 covers the organization’s commitment to integrity and ethical values, evidenced by a code of conduct and acknowledgments. CC1.3 covers how management, with board oversight, establishes structures, reporting lines, and authorities. CC1.2 sits between them: it’s specifically about the board being independent from management and actively overseeing internal control.


