ISO 14001:2026 was published on 15 April 2026. Over 600,000 organizations in more than 180 countries are currently certified to the previous edition, and all of them have until approximately May 2029 to transition.
The revision is not a rebuild, but it is not cosmetic either. It sharpens several requirements that were inconsistently applied under the 2015 standard, introduces a formally new clause on change management, and embeds climate change, biodiversity, and lifecycle thinking more directly into the Environmental Management System (EMS) framework.
This article explains what has changed, what has not, and what certified organizations need to do next.
What Is ISO 14001 and Why Is It Being Updated?
A Brief Overview of ISO 14001
ISO 14001 is the internationally recognized standard for Environmental Management Systems (EMS). Published by the International Organization for Standardization (ISO), it gives organizations a structured framework for managing environmental impacts, meeting legal obligations, and pursuing continual improvement in environmental performance. The standard applies to organizations of any size, in any sector, anywhere in the world, and more than one million sites globally are currently certified against it.
Its value lies not in prescribing specific environmental outcomes, but in building the management system infrastructure that makes consistent, improving performance possible. Whether an organization is a manufacturer managing chemical discharge or a logistics provider tracking fuel consumption, ISO 14001 provides the same underlying framework for setting objectives, measuring performance, and driving improvement.
Why ISO 14001:2015 Is Being Revised
The 2015 version replaced ISO 14001:2004 and introduced several significant advances: risk-based thinking, a stronger link to organizational strategy, and the Harmonized Structure that aligned ISO 14001 with ISO 9001 and ISO 45001. It was a substantial step forward. But the environment it was designed for has changed.
Climate change is now a core business risk, not a future projection. Biodiversity loss is accelerating. ESG reporting obligations have multiplied. Investors and regulators expect documented evidence of environmental performance, not just policy statements. The 2015 edition left too much room for organizations to treat climate and biodiversity as optional considerations within context analysis. The 2026 revision corrects that deliberately.
Reach ISO 14001 Compliance in 6 Weeks or Less
Schedule Your Free ISO 14001 Assessment Today
ISO 14001:2015 vs ISO 14001:2026: Overview of Key Differences
What Has Changed and What Has Stayed the Same
The core architecture of ISO 14001 is unchanged. The standard still follows the Plan-Do-Check-Act (PDCA) cycle and retains the Harmonized Structure it shares with ISO 9001, ISO 45001, ISO 50001, and other major management system standards. The ten-clause framework remains intact.
What has changed is the specificity and accountability required within that framework. Environmental conditions must now be explicitly identified and named in context analysis. Change management is now a formal, auditable requirement rather than an implied expectation. Supply chain thinking is more directly embedded into operational controls. Internal audits must now have defined objectives, not just scope and criteria.
The table below summarizes the most significant differences between the two editions.
Area | ISO 14001:2015 | ISO 14001:2026 |
|---|---|---|
Climate change | Not explicitly required (added via 2024 amendment) | Formally integrated; required across multiple clauses |
Biodiversity | Implied; not named | Explicitly required in context analysis |
Change management | No standalone clause | New standalone Clause 6.3 |
Risks and opportunities | Within Clause 6.1 | New standalone Clause 6.1.4 |
Supply chain scope | “Outsourced processes” | “Externally provided processes, products and services” |
Internal audit | Defined scope and criteria | Defined scope, criteria, and objectives |
Clause 10.1 | Standalone continual improvement clause | Integrated into Clauses 10.2 and 10.3 |
What the ISO 14001:2026 Revision Is, and Is Not
ISO 14001:2026 is not a new standard. It does not introduce a fundamentally different approach to environmental management. Organizations with a mature, well-run ISO 14001:2015 EMS will not be starting from scratch.
What the revision is: a targeted update that addresses gaps and ambiguities that have accumulated since 2015. It makes previously optional considerations mandatory, adds structural clarity where the 2015 edition was ambiguous, and aligns the standard more closely with how environmental management intersects with modern business risk, ESG reporting, and supply chain accountability.
Organizations that applied the 2015 standard in a minimal or box-ticking way will face more substantial transition work. Organizations that ran a genuine, actively managed EMS will find most of what is required already in place, with focused updates needed in a handful of areas.
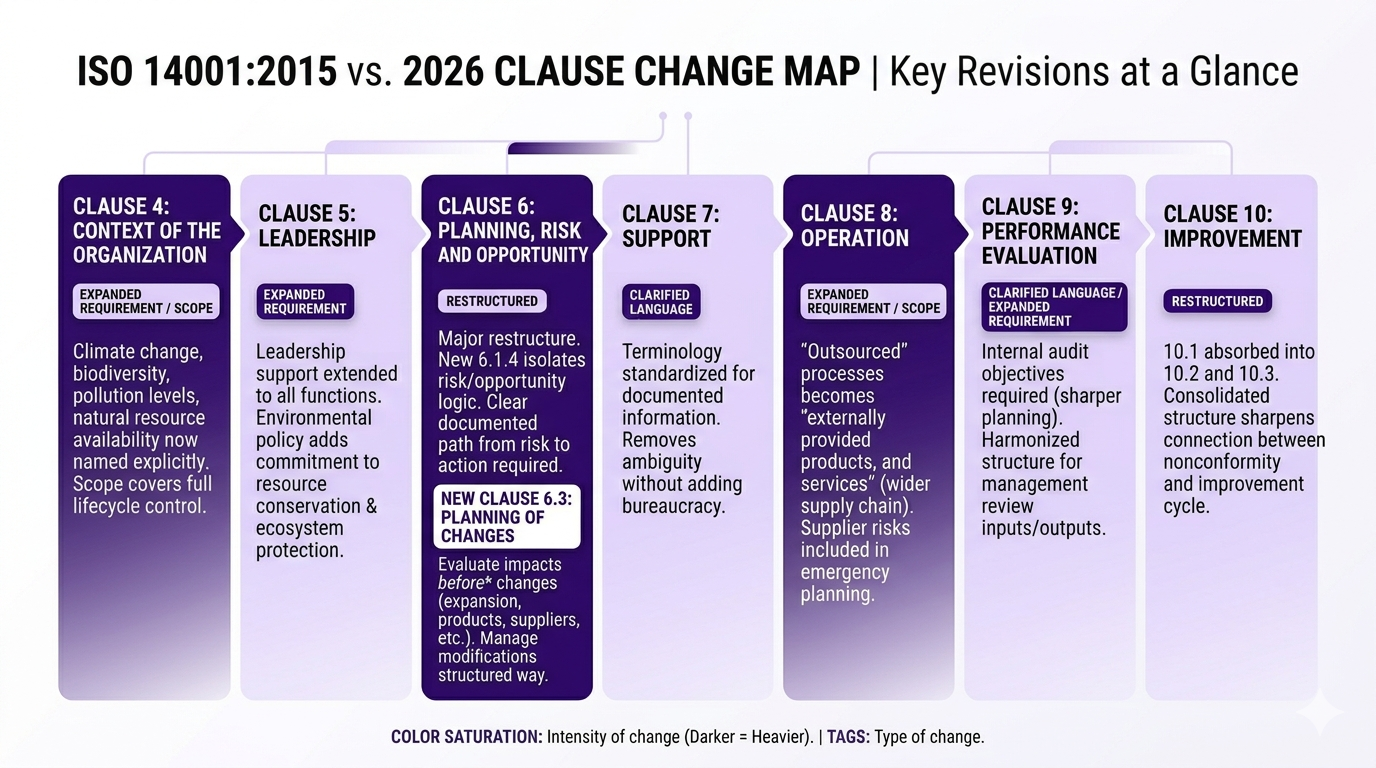
Clause-by-Clause Comparison: ISO 14001:2015 vs ISO 14001:2026
Clause 4: Context of the Organization
In ISO 14001:2015, Clause 4.1 required organizations to identify external and internal issues relevant to their EMS. Climate change was a possible consideration, but not a named one. The 2026 revision changes this directly.
ISO 14001:2026 now explicitly names four categories of environmental condition that must be assessed when determining organizational context: climate change, pollution levels, biodiversity and ecosystem health, and the availability of natural resources. These are not suggestions; they place these issues squarely on the required agenda for every certified organization.
The practical implication is significant. An organization that previously mapped its context by tracking energy use and waste generation now needs to demonstrate how it has assessed whether biodiversity loss, water scarcity, or local pollution levels are material to its operating environment. If they are, those factors must flow into objectives, risk registers, and operational controls.
Clause 4.3, which covers the scope of the EMS, has also been strengthened. Organizations are now expected to define their scope with explicit reference to their authority and ability to exercise control and influence across the full life cycle of their activities, products, and services. The EMS boundary is no longer limited to the physical boundary of the facility.
Clause 5: Leadership
Top management responsibilities are expanded in the 2026 edition. The 2015 version focused on management roles. The 2026 revision makes clear that leadership must support environmental performance across all relevant functions, including non-management roles.
The environmental policy itself has been updated. ISO 14001:2026 expects the policy to include a commitment to conserving natural resources and protecting ecosystems, alongside the existing commitments to pollution prevention and continual improvement.
This clause often receives less attention during gap analyses than the more structural changes in Clause 6. But it is increasingly relevant for organizations facing ESG scrutiny, where auditors and investors want to see leadership accountability that goes beyond a signed policy on a wall.
Clause 6: Planning, Risk and Opportunity Now Clearer and More Auditable
Clause 6 sees the most structural change of any section in the revised standard. The 2015 edition bundled environmental aspects, compliance obligations, and risks and opportunities together in Clause 6.1. ISO 14001:2026 reorganizes this logic.
A new Clause 6.1.4 isolates risks and opportunities as a distinct planning step. This brings ISO 14001 into closer alignment with the risk-based framework of ISO 9001:2015 and makes the risk assessment process more clearly auditable. Organizations must now demonstrate a documented path from identified risk or opportunity to planned action, with that logic visible and reviewable.
The most significant structural addition is Clause 6.3: Planning of Changes. This is the only genuinely new clause in the revision. ISO 14001:2015 had no formal requirement for managing planned changes to the EMS; its absence was a recognized gap, and the 2026 revision fills it. Clause 6.3 requires organizations to evaluate environmental impacts before changes occur, manage new or modified activities and processes in a structured way, and monitor the effectiveness of planned changes. Relevant change events might include business expansion, new product lines, supplier changes, site relocation, or process redesign.
You do not need a formal standalone procedure to demonstrate conformance with Clause 6.3. Evidence can include change forms, meeting notes, or digital workflow logs. What auditors will look for is a defined, repeatable process that is being followed consistently, not necessarily a dedicated document.
Clause 7: Support
Documentation requirements are clarified and standardized. Under ISO 14001:2015, the language around what must be formally documented was inconsistent in places. The 2026 revision standardizes terminology: information that must be available as documented information is now clearly distinguished from information that must be maintained as controlled documentation. The intent is to remove ambiguity without adding bureaucratic load.
Clause 8: Operation, Change Management Now Explicit
Clause 8.1 replaces the previous reference to “outsourced processes” with “externally provided processes, products, and services.” This is more than a terminology update. It broadens the scope of what the EMS must cover in operational controls, extending expectations to a wider range of external providers including suppliers, logistics partners, and service contractors, a development with direct implications for organizations managing complex supply chains or working toward R2 certification or e-waste certification, where supply chain accountability is central.
Clause 8.2, covering emergency preparedness and response, has also been strengthened. Supplier-related risks that the organization can control or influence must now be explicitly factored into emergency planning scenarios, rather than treated as external and therefore outside the EMS.
Clause 9: Performance Evaluation
Two targeted updates in Clause 9 change how internal audits are planned and how management reviews are structured. Under Clause 9.2.2, internal audits must now have defined objectives in addition to the previously required scope and criteria. This distinction matters: an audit designed to verify legal compliance has a different objective than one assessing the effectiveness of a new operational control. Making objectives explicit sharpens audit planning and produces more actionable outputs.
Management reviews have also been updated with clearer guidance on required inputs and expected outputs, bringing them into closer alignment with the structured approach used in other harmonized management system standards.
Clause 10: Improvement
Clause 10.1, previously a standalone continual improvement clause, has been absorbed into Clauses 10.2 and 10.3. The underlying requirements have not changed. The consolidation sharpens the connection between nonconformity management, corrective action, and the EMS improvement cycle, removing the loose separation that existed in the 2015 structure.
Major Thematic Changes in ISO 14001:2026
A Stronger Focus on Real-World Environmental Issues
Climate change, biodiversity, and natural resource use are now core topics within the EMS, not optional context. By explicitly naming these issues in Clause 4, the standard makes it much harder for organizations to treat them as peripheral. Auditors will expect to see documented evidence of how each has been considered. Organizations tracking only energy consumption and carbon emissions will need to broaden their environmental context analysis.
ISO 14001 maps closely to several Corporate Sustainability Reporting Directive (CSRD) reporting obligations, particularly the ESRS E topics covering climate (E1), pollution (E2), water (E3), biodiversity (E4), and circular economy (E5). Organizations with a well-run ISO 14001:2026 EMS will have much of the process infrastructure already in place for regulatory environmental disclosures.
Supply Chain and Lifecycle Thinking Continues to Strengthen
The 2026 revision reinforces a direction that has been building in the standard since 2015: responsibility does not stop at organizational boundaries. The change from “outsourced processes” to “externally provided processes, products, and services” in Clause 8.1, combined with the lifecycle perspective now embedded in the EMS scope, means that supply chain environmental impacts must be actively considered. For organizations subject to Scope 3 emissions reporting under GHG accounting frameworks, this alignment between EMS expectations and sustainability reporting obligations is directly useful.
Environmental Policy Expectations Have Evolved
The environmental policy update in Clause 5 reflects the broader shift in how environmental management is understood externally. Committing to conserving natural resources and protecting ecosystems is now a formal expectation within the policy, not just a best practice. For organizations that have already updated their policies to reflect ESG commitments, this may require little more than a review. For those with older, minimally revised policies, substantive revision will be needed.
Documentation, More Flexible, But Still Important
The standardization of documentation language across the 2026 edition is clarifying rather than restrictive. Organizations do not need elaborate procedure libraries to demonstrate conformance. What auditors look for is accessible, consistent evidence that requirements are being applied in practice, not whether a particular document exists in a particular format.
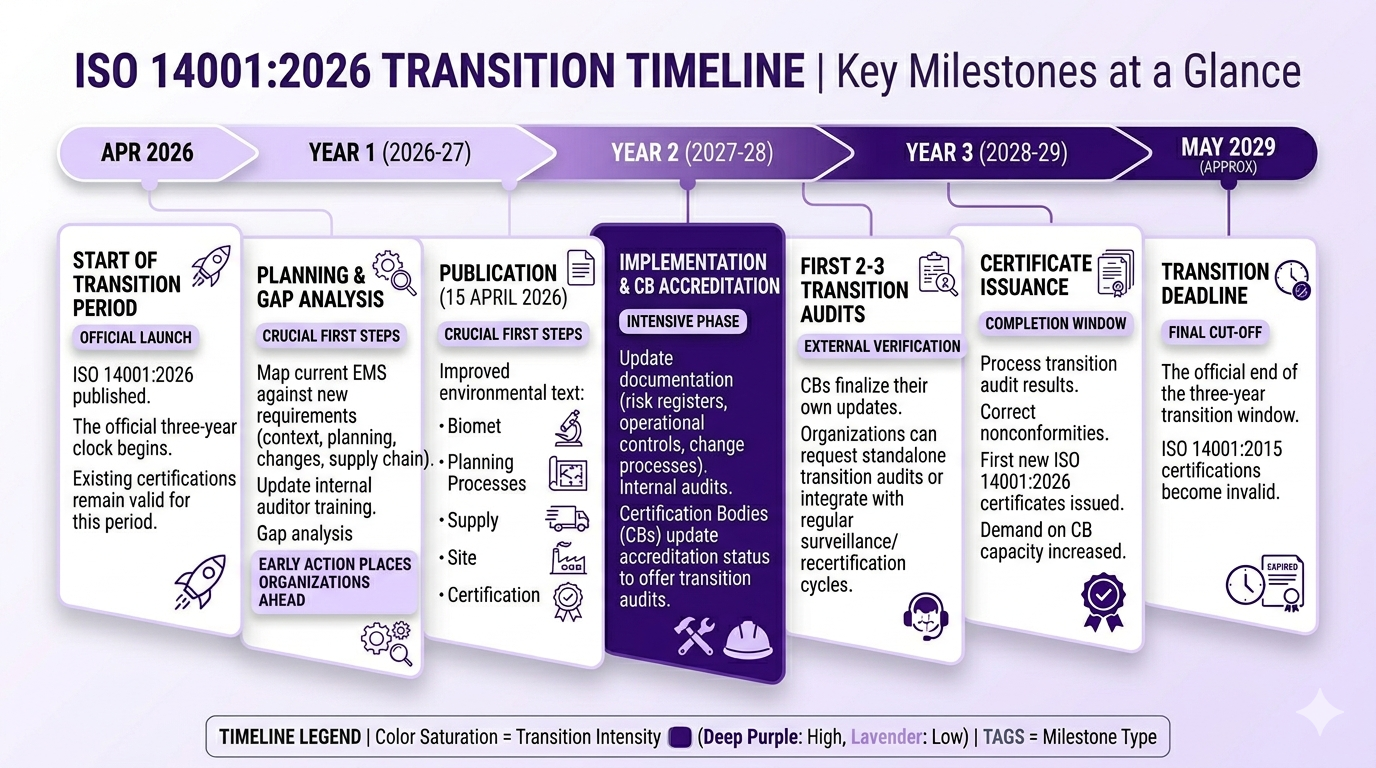
ISO 14001:2026 Transition Timeline and What to Expect
Three-Year Transition Period Explained
ISO 14001:2026 was published on 15 April 2026. The transition period is three years, consistent with standard International Accreditation Forum (IAF) practice for major management system standard revisions. The expected transition deadline is approximately May 2029.
During the transition period, ISO 14001:2015 certifications remain valid. Organizations can continue operating under their current certificate until their transition audit is completed. Certification bodies accredited by national bodies, such as UKAS (United Kingdom Accreditation Service) in the UK, or equivalent bodies elsewhere, will need to complete their own accreditation updates before issuing certificates to the new edition.
Key Deadlines for Certified Organizations
Transition can be conducted as a standalone transition audit or incorporated into the regular surveillance or recertification audit cycle. Most practitioners recommend using the existing surveillance cycle where possible, since it reduces disruption and cost. Certification bodies are expected to begin offering transition audits during 2027, once their own accreditation processes are finalized. First ISO 14001:2026 certificates are likely to be issued during 2027 or 2028.
Why Consider Transitioning Early
The three-year window is generous, but organizations that wait until 2028 will face compressed timelines, potential bottlenecks with certification bodies, and the risk of rushed updates. Gap analysis, documentation review, internal audit training, and management review preparation all take time, particularly for large or multi-site organizations. Starting now places organizations well ahead of both the deadline and the expected demand on certification body capacity.
What ISO 14001:2026 Means for Your Business
Impact on Currently Certified Organizations
For organizations with a mature, actively managed ISO 14001:2015 EMS, the transition will require targeted updates rather than wholesale redesign. The areas that typically require the most attention are: context analysis (broadening it to explicitly address climate, biodiversity, resource availability, and pollution); change management (formalizing a process for Clause 6.3); lifecycle and supply chain thinking (extending operational controls and aspect assessments beyond direct operations); and internal audit planning (adding defined objectives to the audit program). Organizations that implemented the 2015 standard minimally, without genuine integration into operational decision-making, will face more substantial work.
Key Steps to Prepare for the Transition Now
- First: read and understand the revised requirements, with priority attention to Clauses 4, 6, and 8.
- Second: run a gap analysis comparing the current EMS against the 2026 requirements.
- Third: update the context analysis and environmental policy to reflect the new expectations.
- Fourth: build or formalize a change management process for Clause 6.3.
- Fifth: review and extend operational controls across the supply chain.
- Sixth: update the internal audit program to include objectives, run an internal audit against the updated requirements, and prepare for the transition audit with the certification body. For a mature EMS, a realistic timeline for this sequence is three to six months of focused work.
How ISO 14001:2026 Relates to Other Standards (ISO 9001, ISO 45001)
The updated Harmonized Structure alignment in ISO 14001:2026 makes integrated management systems easier to operate and audit consistently. Organizations running ISO 14001 alongside ISO 9001 or ISO 45001 will find that the structural consistency across all three standards is now stronger than it was in 2015.
ISO 9001 is also undergoing revision, with publication expected in September 2026. Organizations managing both certifications may be able to coordinate transition planning, reducing the overall effort of updating an integrated management system and avoiding two separate rounds of internal disruption.
Reach ISO 14001 Compliance in 6 Weeks or Less
Schedule Your Free ISO 14001 Assessment Today
Frequently Asked Questions
What Is the Difference Between ISO 14001:2015 and ISO 14001:2026?
ISO 14001:2026 builds on the 2015 version without replacing its fundamental structure. The main differences are: explicit requirements for climate change, biodiversity, and natural resource considerations in organizational context (Clause 4); a new Clause 6.3 on change management; a new Clause 6.1.4 separating risks and opportunities; broader supply chain scope in operational controls; standardized documentation language; and defined objectives now required for internal audits. The PDCA cycle and the Harmonized Structure remain unchanged.
Is ISO 14001:2015 Still Valid?
Yes, during the transition period. ISO 14001:2015 certifications remain valid until approximately May 2029. After that deadline, certificates to the 2015 edition will no longer be recognized, and all certified organizations must have completed their transition to the 2026 edition.
When Does the Transition to ISO 14001:2026 Need to Be Completed?
The transition deadline is approximately May 2029, three years from the April 2026 publication date. This is consistent with IAF guidance for management system standard transitions and applies to all currently certified organizations worldwide.
Do I Need to Be Recertified for ISO 14001:2026?
Not from scratch. Transition does not require a full recertification process. It is typically handled as a transition audit, which can be a standalone event or integrated into regular surveillance or recertification audits. Contact us or your accredited certification body for specific guidance on how they plan to manage transition audits and what evidence they will require.
How Does ISO 14001:2026 Address Climate Change?
Climate change is now explicitly required in context analysis under Clause 4. The 2024 amendment (ISO 14001:2015/Amd 1:2024) already made this mandatory for organizations certified to the 2015 edition. The 2026 revision formally integrates that requirement and extends the climate lens further, connecting it to biodiversity, ecosystem health, and natural resource availability across multiple clauses.
Will ISO 14001:2026 Change How Audits Are Conducted?
Audits will evolve to reflect the new requirements. Clause 6.3 is new, so auditors will look for evidence of a defined change management process and documented examples of how changes have been planned and controlled. Context analysis reviews will need to show explicit consideration of the four named environmental conditions. Internal audits will be expected to have documented objectives alongside scope and criteria. Organizations should expect audit checklists and criteria to be updated by certification bodies during 2026 and 2027 as accreditation processes are finalized.