HIPAA and GDPR are the two most consequential data protection frameworks any healthcare or technology organisation is likely to encounter. They share a common purpose, protecting sensitive personal data, but they differ significantly in scope, enforcement mechanisms, and compliance obligations.
For organisations operating across the Atlantic, understanding where they align, where they clash, and how to satisfy both simultaneously is not optional. It is a legal necessity.
What Is HIPAA?
The Health Insurance Portability and Accountability Act was enacted by the U.S. Congress in 1996. Its original purpose was to modernise the flow of healthcare information and ensure the portability of health insurance coverage. Over time, it became primarily known for its data protection requirements, administered by the U.S. Department of Health and Human Services (HHS) and enforced by the Office for Civil Rights (OCR).
HIPAA is built around three core rules.
- The Privacy Rule governs how Protected Health Information (PHI) may be used and disclosed.
- The Security Rule sets standards for safeguarding electronic PHI (ePHI).
- The Breach Notification Rule establishes mandatory reporting timelines when PHI is compromised.
Who Needs to Be HIPAA Compliant?
HIPAA applies to covered entities, healthcare providers, health plans, and healthcare clearinghouses, and to their business associates: any third-party organisation that handles PHI on their behalf. If you build software that processes patient data for a U.S. hospital, you are a business associate. If you store medical records in the cloud for an insurance company, you are a business associate. A Business Associate Agreement (BAA) is the formal contract that governs this relationship.
What Types of Data Does HIPAA Protect?
HIPAA protects Protected Health Information (PHI): any individually identifiable information relating to a person’s past, present, or future physical or mental health condition, the provision of healthcare, or the payment for healthcare.
This includes names, dates of birth, Social Security numbers, medical record numbers, and any data that could be used to identify a patient in connection with their health. Electronic PHI, the subset stored or transmitted digitally, is subject to the Security Rule’s additional technical requirements.
What Is GDPR?
The General Data Protection Regulation came into force across the European Union on 25 May 2018, replacing the 1995 Data Protection Directive. It is the world’s most comprehensive data privacy law, and its extraterritorial reach means it extends well beyond Europe’s borders. The GDPR is enforced by national Data Protection Authorities (DPAs) and coordinated at the European level by the European Data Protection Board (EDPB). Unlike HIPAA, GDPR is not sector-specific. It applies to any organisation processing the personal data of EU residents, regardless of industry.
Who Needs to Be GDPR Compliant?
Any organisation that processes the personal data of individuals located in the European Union, regardless of where the organisation is based. A U.S. hospital treating European patients, a SaaS company offering services to German users, or a health app collecting data from French residents all fall within GDPR’s scope. The regulation applies to both data controllers (organisations that determine how and why data is processed) and data processors (third parties that process data on a controller’s behalf).
What Types of Data Does GDPR Protect?
GDPR protects all personal data: any information relating to an identified or identifiable natural person. Health data is explicitly designated a special category under GDPR Article 9, commanding heightened protection alongside biometric data, genetic data, racial or ethnic origin, religious beliefs, and sexual orientation.
HIPAA vs GDPR: Key Differences at a Glance
| Feature | HIPAA | GDPR |
|---|---|---|
| Jurisdiction | United States only | EU + extraterritorial reach |
| Sector | Healthcare only | All sectors |
| Regulatory body | HHS / OCR | National DPAs / EDPB |
| Data covered | PHI only | All personal data |
| Consent model | Treatment-based exceptions | Explicit consent required |
| Breach notification | 60 days (proposed: 72 hours) | 72 hours |
| Max fine | $1.9M per violation category/year | €20M or 4% of global turnover |
| DPO required | No | Sometimes |
| Right to erasure | Limited | Yes |
Scope and Geographic Reach
HIPAA’s reach is defined by entity type: it applies to covered entities and business associates operating within the United States. Whether a patient holds EU citizenship is irrelevant to HIPAA jurisdiction. What matters is whether the organisation providing care or processing health data operates within the U.S. healthcare system.
GDPR’s reach is defined by the location of the data subject, not the organisation. Article 3 of the GDPR gives it explicit extraterritorial effect. If your organisation targets or monitors EU residents, GDPR applies, regardless of where you are headquartered, where your servers are located, or what industry you operate in.
Types of Data Protected: Personal Data vs Protected Health Information (PHI)
This is the sharpest structural difference between the two frameworks. HIPAA is focused exclusively on health data in the context of healthcare delivery or payment. GDPR covers all personal data, from email addresses and IP addresses to medical records and genetic profiles.
Health data under GDPR is a subset of the broader personal data category, not the totality of it. An organisation that is fully HIPAA-compliant may still be in violation of GDPR if it mishandles employee data, marketing data, or website analytics.
Legal Basis for Data Processing
GDPR requires organisations to identify a valid legal basis before processing any personal data. For health data, that typically means explicit consent or one of the specific derogations in Article 9(2), such as processing necessary for medical diagnosis or the provision of healthcare. This is a meaningful threshold; pre-ticked boxes, bundled consent, or vague terms of service do not meet GDPR’s standard.
HIPAA takes a different approach. It permits covered entities to use and disclose PHI for treatment, payment, and healthcare operations without obtaining patient consent. Authorisation is required only in specific circumstances, such as disclosures for marketing purposes or release of psychotherapy notes.
Important: GDPR’s explicit consent requirement creates real friction for U.S. healthcare organisations treating EU patients. A hospital cannot rely on its standard HIPAA-compliant intake forms to satisfy GDPR. The legal bases must be documented separately, and consent forms must meet the GDPR’s granularity requirements.
Regulatory Authority and Enforcement
HHS OCR is the primary HIPAA enforcer in the United States. OCR investigates complaints, conducts compliance reviews, and imposes civil monetary penalties. In serious cases, the Department of Justice (DOJ) handles criminal enforcement.
Under GDPR, enforcement sits with each EU member state’s national DPA. Ireland’s Data Protection Commission (DPC), France’s CNIL, and Germany’s BfDI are among the most active. The EDPB coordinates cross-border enforcement and issues binding guidelines, but individual DPAs investigate organisations and impose fines.
Consent Requirements
Under GDPR, consent must be freely given, specific, informed, and unambiguous. For special category data, including health data, it must be explicit. Individuals can withdraw consent at any time, and organisations must be able to demonstrate that it was validly obtained. Silence, pre-ticked boxes, or inactivity do not count.
HIPAA permits treatment, payment, and operations processing without patient consent. Authorisation is required for specific disclosures outside these standard permissions.
Data Breach Notification Requirements
Under current HIPAA rules, covered entities must notify affected individuals and HHS within 60 calendar days of discovering a breach. For breaches affecting 500 or more individuals in a state, media notification is also required. The HIPAA Breach Notification Rule permits smaller breaches to be reported on an annual basis. Importantly, the 2025 proposed HIPAA Security Rule overhaul would reduce this to 72 hours for large breaches, aligning HIPAA’s timeline with GDPR.
GDPR requires notification to the relevant supervisory authority within 72 hours of becoming aware of a breach, where that breach is likely to result in a risk to individuals’ rights. If the breach poses a high risk to those individuals, affected data subjects must also be notified directly, without undue delay.
Worth Knowing: GDPR’s 72-Hour Breach Notification Rule
Under GDPR, if you cannot provide all details within 72 hours, you can submit the notification in phases, but the clock does not pause while you investigate. Initial notification is required, with supplemental information to follow. Many organisations discover a breach and wait to notify until the investigation is complete; this approach routinely results in regulatory scrutiny.
Penalties and Fines
HIPAA penalties are tiered by culpability, ranging from $100 to $50,000 per violation, with a maximum annual cap of $1.9 million per violation category (updated for inflation in 2023). Criminal penalties, pursued by the DOJ, can reach $250,000 and 10 years’ imprisonment.
GDPR fines operate on a two-tier structure. Less severe violations carry fines up to €10 million or 2% of global annual turnover, whichever is higher. Violations of core principles, lawfulness of processing, data subject rights, transfers to third countries can trigger fines up to €20 million or 4% of global annual turnover. By early 2026, cumulative GDPR fines had exceeded €7.1 billion since the regulation came into force.
Data Protection Officer (DPO) Requirements
HIPAA does not require a Data Protection Officer. Covered entities are expected to designate a Privacy Officer and a Security Officer, but these are internal roles without the formal independence that GDPR mandates.
Under GDPR Article 37, certain organisations must appoint a DPO: public authorities, organisations engaged in large-scale systematic monitoring of individuals, and organisations processing special category data on a large scale. For healthcare SaaS vendors processing EU patient data at scale, this threshold is frequently met.
Privacy Rights and Data Subject Access
GDPR grants data subjects a comprehensive set of rights: access, rectification, erasure, restriction of processing, data portability, and the right to object. These must be responded to within one month in most cases, with a limited extension to three months for complex requests.
HIPAA grants patients the right to access their own PHI, request corrections, and receive an accounting of disclosures. These are meaningful rights, but narrower than GDPR’s framework. HIPAA does not, for instance, grant patients data portability in the GDPR sense, nor does it provide a general right to object to processing.
The Right to Be Forgotten: GDPR vs HIPAA
This is where the two frameworks create a genuine compliance conflict. Under GDPR Article 17, individuals can request erasure of their personal data under certain conditions. A European patient treated by a U.S. provider might, in principle, request deletion of all records relating to their treatment.
HIPAA, however, requires covered entities to retain medical records for at least six years from the date of creation or last use, whichever is later. Deleting records on request could place an organisation in HIPAA violation, even if refusing to delete them constitutes a GDPR violation.
Insider Note: Organisations caught between GDPR erasure requests and HIPAA retention requirements should document their legal basis for retaining the records and respond to the GDPR request explaining why erasure cannot be fulfilled. GDPR Article 17(3) includes an explicit carve-out for legal obligations requiring retention; this is the mechanism to rely on, but the documentation must be in place before the request arrives.
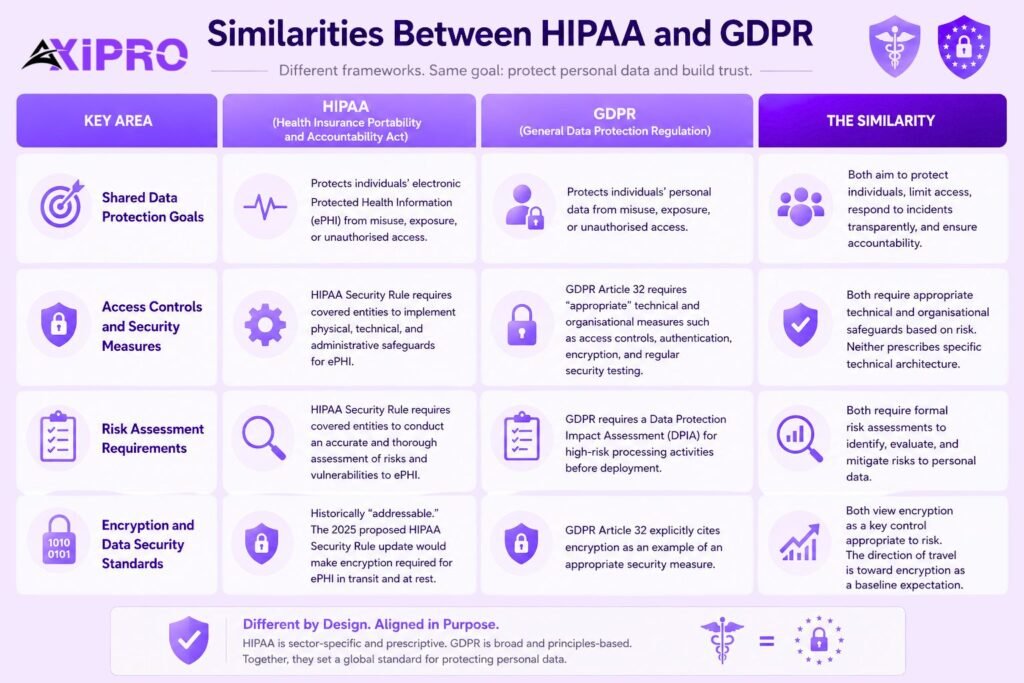
Similarities Between HIPAA and GDPR
Shared Data Protection Goals
Both HIPAA and GDPR exist to protect individuals from the misuse, exposure, or unauthorised access to sensitive personal data. They take different routes, one sector-specific and prescriptive, the other broad and principles-based, but the destination is the same: organisations must treat personal data with care, limit access to those who need it, respond to failures transparently, and maintain accountability for their data practices.
Access Controls and Security Measures
Both frameworks require appropriate technical and organisational safeguards. The HIPAA Security Rule requires covered entities to implement physical, technical, and administrative controls for ePHI. GDPR Article 32 requires “appropriate” technical and organisational measures, which in practice means access controls, authentication, encryption, and regular security testing. Neither regulation prescribes a specific technical architecture; both expect organisations to assess risk and implement proportionate controls.
Risk Assessment Requirements
Both HIPAA and GDPR require formal risk assessments. The HIPAA Security Rule requires covered entities to conduct an accurate and thorough assessment of risks and vulnerabilities to ePHI. GDPR’s Data Protection Impact Assessment (DPIA) requirement, triggered for high-risk processing activities, follows the same logic. Before deploying a new healthcare application processing EU patient data, a DPIA is not a best practice, it is mandatory.
Encryption and Data Security Standards
Neither regulation originally mandated encryption as an absolute requirement. Both framed it as a control appropriate to the risk. The 2025 proposed HIPAA Security Rule update would make encryption required for ePHI in transit and at rest, eliminating the previous “addressable” flexibility. GDPR Article 32 cites encryption explicitly as an example of an appropriate security measure. The direction of travel under both frameworks is toward encryption as a baseline expectation.
GDPR vs HIPAA Compliance Requirements Explained
HIPAA Compliance Requirements Overview
HIPAA compliance centres on three rules.
- The Privacy Rule governs permissible uses and disclosures of PHI, minimum necessary standards, and patient rights.
- The Security Rule establishes technical, physical, and administrative safeguards for ePHI.
- The Breach Notification Rule governs timelines and procedures when PHI is compromised.
Organisations demonstrate compliance through documented policies and procedures, regular risk assessments, employee training, access controls, audit logging, and Business Associate Agreements with all third parties handling PHI. There is no formal HIPAA certification; compliance is demonstrated through documentation and internal controls, which OCR evaluates during investigations and compliance reviews.
GDPR Compliance Requirements Overview
GDPR compliance requires organisations to: identify a lawful basis for each processing activity; maintain Records of Processing Activities (RoPA); implement data subject rights mechanisms across all relevant systems; appoint a DPO where required; complete DPIAs for high-risk processing; execute Data Processing Agreements (DPAs) with all processors; establish breach notification workflows; and address cross-border data transfer obligations using an approved mechanism such as Standard Contractual Clauses (SCCs) or the EU-U.S. Data Privacy Framework (DPF).
Can an Organization Be Subject to Both HIPAA and GDPR?
Yes, and this situation is increasingly common.
When Dual Compliance Is Required
A U.S. hospital actively marketing telemedicine services to patients in Europe triggers both regimes. A health-tech SaaS company selling software to EU hospitals and U.S. clinics must satisfy both. A global pharmaceutical company running clinical trials across the United States and the EU falls under both. The key question is: does the organisation handle PHI from U.S. covered entities, and does it also process personal data of EU residents?
Challenges of Achieving Dual Compliance
The most significant friction points are consent, retention, and the right to erasure. GDPR demands explicit consent as the legal basis for health data processing in many contexts; HIPAA permits processing without consent for treatment and operations. GDPR grants the right to erasure; HIPAA mandates six-year retention. GDPR requires 72-hour breach notification; HIPAA currently allows 60 days (though the proposed rule would close this gap). Each of these conflicts requires deliberate resolution, not a single document that attempts to satisfy both simultaneously.
Tips for Meeting Both HIPAA and GDPR Requirements
Use GDPR’s stricter requirements as the floor wherever the standards diverge. Implement 72-hour breach notification regardless of which framework technically applies. Treat all patient data as requiring explicit consent, even where HIPAA permits treatment-based exceptions. Use both a BAA and a DPA with processors handling data subject to both frameworks; these are different agreements serving different legal purposes. Document the retention justification clearly for any records that cannot be erased on GDPR request, invoking HIPAA’s retention obligation as the legal basis under GDPR Article 17(3).
Pro Tip: Map your Data Flows
Map your data flows against both frameworks simultaneously, rather than sequentially. A single data inventory annotated against HIPAA's PHI definition and GDPR's personal data categories will surface the exact points of overlap and conflict, and it is far easier to build controls around those collision points upfront than to retrofit them after a dual-framework audit.
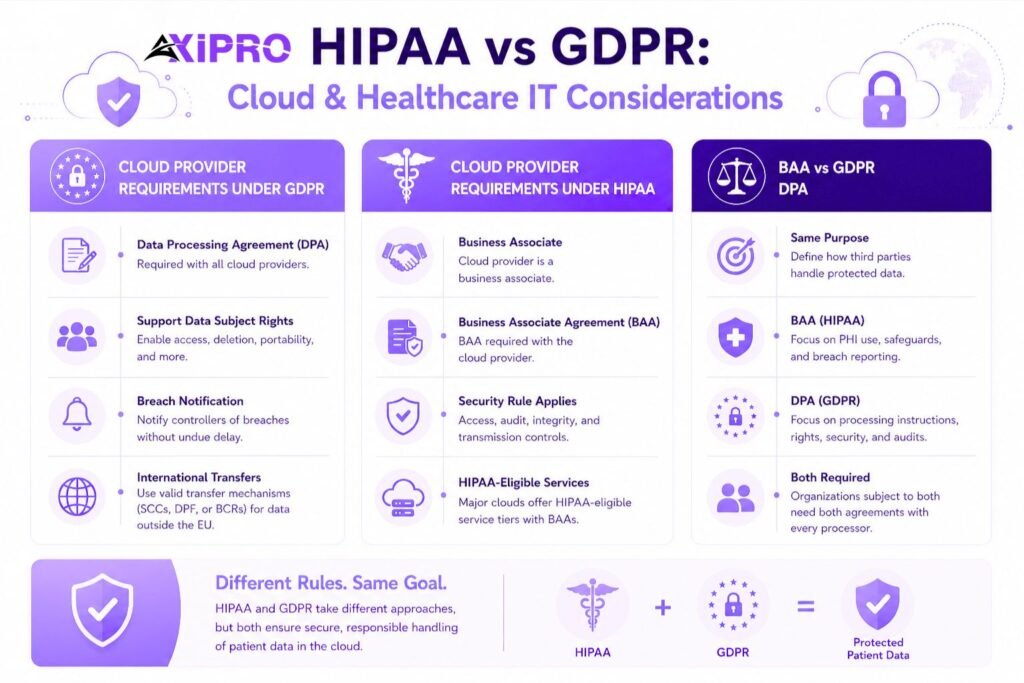
HIPAA vs GDPR: Cloud and Healthcare IT Considerations
Cloud Provider Requirements Under GDPR
Under GDPR, cloud providers acting as data processors must execute a Data Processing Agreement with their clients. The DPA must specify the nature and purpose of processing, the categories of data and data subjects involved, the duration of processing, and the obligations and rights of the controller. Cloud providers must also support data subject rights requests and notify controllers of breaches without undue delay. For data stored or processed outside the EU, the appropriate transfer mechanism, SCCs, the DPF, or Binding Corporate Rules, must be in place.
Cloud Provider Requirements Under HIPAA
Under HIPAA, a cloud service provider storing or processing ePHI is a business associate, regardless of whether it can actually view or access that data. The covered entity or business associate must execute a BAA with the cloud provider. The Security Rule’s requirements apply in full: access controls, transmission security, audit controls, and integrity controls. AWS, Microsoft Azure, and Google Cloud all offer HIPAA-eligible service tiers with associated BAA templates.
Business Associate Agreements vs GDPR Data Processing Agreements
A BAA and a DPA serve analogous purposes, establishing terms under which a third party handles protected data, but they are distinct documents with different legal requirements. A BAA is tailored to HIPAA: it governs permissible uses and disclosures of PHI, requires appropriate safeguards, and mandates breach reporting. A DPA is tailored to GDPR Article 28: it covers processing instructions, security measures, sub-processor management, support for data subject rights, and audit rights. For organisations subject to both frameworks, both agreements are required with every relevant processor.
2025–2026 Regulatory Updates: What Has Changed?
Recent HIPAA Security Rule Updates
In January 2025, HHS published a comprehensive Notice of Proposed Rulemaking to overhaul the HIPAA Security Rule, the first major update since 2013. The proposals would eliminate the distinction between “required” and “addressable” implementation specifications, making every specification mandatory. Encryption of ePHI at rest and in transit would become explicitly required, as would multi-factor authentication (MFA) for all systems involving ePHI. Covered entities would also need to maintain a written technology asset inventory and network map, updated at least annually.
The proposed rule would reduce the breach notification timeline for large breaches (500 or more individuals) from 60 days to 72 hours. The OCR confirmed finalization remains on its regulatory agenda for mid-2026, with a 240-day compliance period following final publication. Healthcare IT teams should treat the proposed changes as directionally final and begin gap assessments now.
Recent GDPR Enforcement Developments
GDPR enforcement has accelerated substantially since 2023. By early 2026, cumulative fines exceeded €7.1 billion. In 2025 alone, regulators issued approximately €1.2 billion in fines. Ireland’s DPC fined TikTok €530 million for unlawfully transferring EU user data to China. France’s CNIL issued a €325 million fine against Google across its entities. The EDPB’s 2025 coordinated enforcement action focused on the right to erasure, with 32 supervisory authorities participating and over 760 controllers investigated.
The EDPB has also clarified that large language models and AI systems rarely meet GDPR’s standards for anonymisation, placing any AI tool processing EU patient data squarely within scope. The EU AI Act’s August 2026 compliance deadline for high-risk AI systems introduces an additional compliance layer for healthcare AI vendors already navigating GDPR obligations.
Worth Knowing: The 2025 HIPAA Security Rule NPRM
The 2025 HIPAA Security Rule NPRM also proposes requirements for business continuity and disaster recovery planning, including annual testing of contingency plans. For healthcare IT teams, this significantly raises the bar for operational resilience.
In Summary
HIPAA and GDPR approach data protection from different angles. HIPAA is narrowly focused on the healthcare sector, U.S. jurisdiction, and specific entity types, with detailed prescriptions for PHI safeguards. GDPR is broadly focused, with a near-universal jurisdictional reach, all personal data, with principles-based obligations designed to scale across industries and technologies.
Where they overlap, as they do for any organisation handling health data on both sides of the Atlantic, GDPR’s requirements tend to be stricter in most dimensions. The practical path to dual compliance is not to find a single framework that satisfies both, but to understand their differences precisely enough to address each on its own terms, and to build controls that can satisfy both simultaneously where the standards permit.
Frequently Asked Questions (FAQ) About HIPAA vs GDPR
Is GDPR Stricter Than HIPAA?
In most respects, yes. GDPR’s maximum fine, up to 4% of global annual turnover, significantly exceeds HIPAA’s $1.9 million annual cap per violation category. GDPR’s consent requirements are more demanding, its data subject rights framework is broader, and its scope extends across all sectors and industries. HIPAA is more prescriptive in its specific technical requirements for healthcare entities, but GDPR’s overall compliance burden is typically greater for organisations subject to both frameworks.
Does HIPAA Apply Outside the United States?
No. HIPAA applies to covered entities and business associates operating within the United States. The nationality of the patient is irrelevant to HIPAA jurisdiction. A French citizen receiving treatment at a New York hospital has their health data protected by HIPAA, but that fact does not trigger GDPR for the hospital; only the organisation’s deliberate conduct toward EU residents in the EU context would do that.
Can a U.S. Hospital Be Subject to GDPR?
Yes, if it actively offers services to or monitors EU residents. A hospital marketing telemedicine services in Europe, maintaining a website in European languages, or accepting payments in euros is likely within GDPR’s extraterritorial scope under Article 3. Any organisation with deliberate commercial activity directed at EU residents should assess GDPR applicability carefully.
What Is the Scope Difference Between HIPAA and GDPR?
HIPAA is sector-specific (healthcare) and jurisdiction-specific (United States). GDPR is sector-agnostic and applies wherever EU residents’ personal data is processed. HIPAA protects only PHI; GDPR protects all personal data, with health data as a special category commanding heightened protection. GDPR’s scope is broader by design.
How Do Breach Notification Requirements Differ Under HIPAA and GDPR?
Current HIPAA rules require notification within 60 calendar days of discovering a breach, with media notification for large-scale incidents. The proposed 2025 HIPAA Security Rule update would require large breaches to be reported to HHS within 72 hours. GDPR requires supervisory authority notification within 72 hours of becoming aware of a breach, with no minimum size threshold, and requires direct notification to affected individuals when the breach poses a high risk to their rights.
What Happens If You Violate Both HIPAA and GDPR?
The penalties stack. A U.S. healthcare organisation suffering a breach that affects both U.S. patients and EU residents could face HIPAA civil monetary penalties from OCR and GDPR fines from the relevant DPA simultaneously. These are independent enforcement actions, pursued by separate authorities under separate legal frameworks. There is no mechanism for offsetting one penalty against the other.
How Do HIPAA and GDPR Affect SaaS Companies?
SaaS companies are business associates under HIPAA if they handle ePHI on behalf of covered entities, regardless of how the service is branded or whether the company identifies as a healthcare company. They are data processors under GDPR if they process personal data on behalf of EU data controllers. In both cases, the appropriate agreement (BAA for HIPAA, DPA for GDPR) is required, and appropriate security controls must be in place. SaaS companies serving healthcare clients globally will routinely need to satisfy both frameworks simultaneously.
Are GDPR and HIPAA Interchangeable?
No. They share a common value, protecting individuals’ sensitive data, but differ fundamentally in scope, legal mechanisms, enforcement, and the rights they confer. HIPAA compliance does not constitute GDPR compliance, and GDPR compliance does not exempt an organisation from HIPAA requirements. For organisations operating under both frameworks, the only compliant path is to address each on its own terms while identifying practical efficiencies where they genuinely overlap.