Most ISO 27001 auditors will tell you the same thing: background checks are one of the most common controls organisations claim to have, and one of the most common controls that falls apart when you ask for evidence. The control itself, Annex A 6.1 (Screening), is short. The discipline of doing it properly across every hire, contractor, and supplier with sensitive access is anything but.
This guide walks through what Annex A 6.1 requires under the 2022 version of the standard, what changed from 2013, how to design a screening process that holds up under audit, and how to apply the control sensibly in small businesses, startups, and AI-first companies where the headcount is low but the data exposure is high.
What Are ISO 27001 Background Checks?
ISO 27001 background checks are pre-employment and ongoing verification activities used to confirm that anyone with access to an organisation’s information assets is who they claim to be, holds the qualifications they say they hold, and presents no known risk that the role would amplify.
The checks are not punitive. They are a control: a way to reduce the probability that a person granted access to sensitive systems turns out to be someone the organisation would never have hired had it asked the right questions up front.
What Does ISO 27001 Say About Background Checks?
The 2022 version of the standard places the requirement in Annex A 6.1, Screening, under the People Controls theme. The control text is brief and worth reading in full:
“Background verification checks on all candidates to become personnel should be carried out prior to joining the organisation and on an ongoing basis taking into consideration applicable laws, regulations and ethics, and be proportional to the business requirements, the classification of the information to be accessed and the perceived risks.”
Three phrases in that sentence carry most of the weight.
“All candidates to become personnel” is broader than employees alone.
“On an ongoing basis” means screening does not end at hire.
“Proportional” gives organisations room to scale checks to risk — and also takes that room away from anyone who wants to apply identical checks to everyone regardless of role.
ISO 27001:2022 Annex A 6.1 Screening Explained
The control sits in the People Controls section (A.6.1 through A.6.8), which addresses the human factor of information security across the employee lifecycle. Annex A 6.1 is specifically the pre-access gate. By the time a new hire or contractor touches a production system, the screening required for their role should already be complete and documented.
In practice, this means three things: there must be a written screening policy; the policy must be applied consistently; and evidence of completed checks must exist for every person in scope, not just senior or technical roles.
Who Needs to Comply with Annex A 6.1?
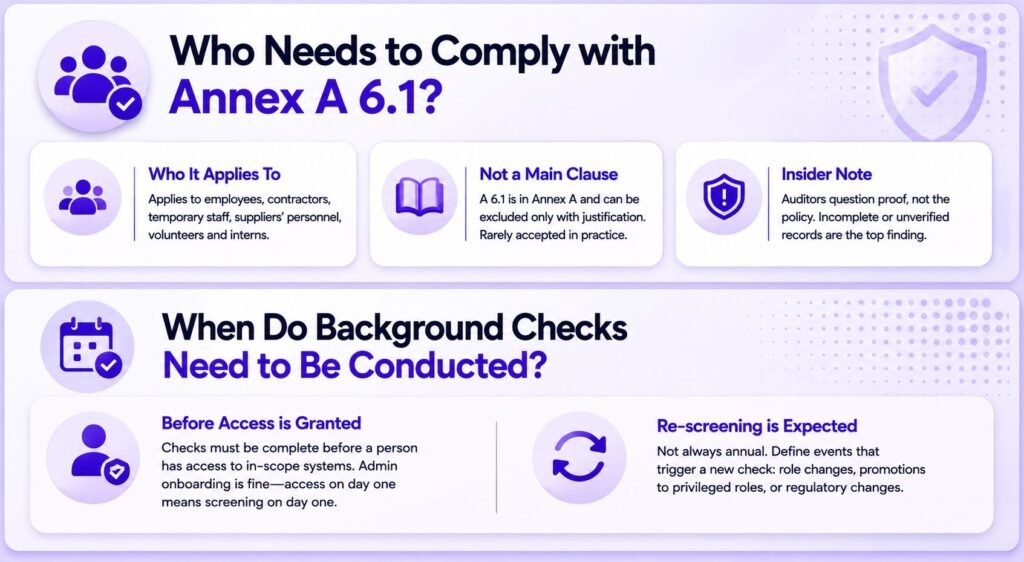
Any organisation pursuing or maintaining ISO 27001 certification needs to evaluate this control. It applies to full-time employees, part-time staff, fixed-term contractors, casual or temporary workers, and selected suppliers whose personnel will be granted access to information systems or facilities. Volunteers and interns are typically in scope as well if they handle anything classified above public.
A 6.1 is not a clause from the main body of the standard (clauses 4 through 10), which means organisations can technically exclude it through the Statement of Applicability if they can justify why it is not relevant. In practice, that justification is almost impossible to make for any organisation with employees or contractors handling customer or production data, and auditors are unlikely to accept it.
Insider Note: Auditors rarely challenge whether you do background checks — they challenge whether you can prove you did them consistently. The most common audit finding under A 6.1 is not a missing policy; it is a screening file with a check listed but no completion date, no result, and no evidence that the result was reviewed before access was granted.
When Do Background Checks Need to Be Conducted?
The default is before access is granted. The standard refers to checks being completed prior to joining the organisation, but for ISO 27001 purposes the practical line is whether the person has access to in-scope systems. If you onboard someone administratively two weeks before they touch any sensitive data, that is fine. If you grant production access on day one, screening must be complete on day one.
Re-screening is also expected on an ongoing basis. This does not mean annual criminal record checks for every employee. Still, it does mean defining the events that trigger a fresh check: role changes that increase access, promotions into privileged positions, or significant changes in the regulatory environment.
Why Background Checks Matter for ISO 27001 Compliance
The control exists because access is the precondition for almost every information security failure. According to the Verizon 2024 Data Breach Investigations Report, 68% of breaches involved a non-malicious human element — and that figure excludes deliberate insider misuse, which is tracked separately. The people inside the perimeter are not the only risk, but they are the most consistent one.
What Impact Does Employee Access Have on Data Security?
A breach does not require a sophisticated attacker. It requires someone with credentials to do something they should not have been able to do, whether through error, manipulation, or intent. The narrower the gate at hiring, the smaller the population of people who can later become a problem. Background checks do not eliminate insider risk, but they raise the cost of getting a job in your organisation under false pretences, which is the entire point.
How Background Check Results Help You Manage Risk and Stay Compliant
Screening results feed directly into the risk management process required elsewhere in ISO 27001. A failed identity check or an undisclosed serious conviction relevant to the role is not just an HR matter — it is a risk decision the organisation must document. As part of any thorough ISO 27001 gap analysis, auditors will look for evidence that screening outcomes were considered, that decisions were defensible, and that the process did not quietly wave people through when results were inconvenient.
What Do ISO 27001 Background Checks Cover?
The standard does not prescribe a fixed list. It expects the organisation to define what is appropriate, document the rationale, and apply the checks consistently for roles at equivalent risk levels.
Key Verifications Included in Annex A 6.1 Screening
A defensible baseline for most roles typically includes verification of identity (a government-issued document such as a passport or driving licence), confirmation of right to work in the relevant jurisdiction, verification of claimed academic and professional qualifications, employment history covering the most recent years, and two independent references (one professional, one personal or character).
The CV should be reviewed against the verified record. Gaps and inconsistencies are not automatically disqualifying, but they should be explained, and the explanation should be on file. For roles with access to financial systems, payment data, or regulated information, a basic criminal record check is standard. In the UK, this is a Basic DBS check; equivalents exist in most jurisdictions.
Enhanced Vetting Under Annex A 6.1
Roles with significant privileged access, board-level visibility, or contact with vulnerable populations warrant deeper checks. Enhanced vetting can include credit checks (where lawful and relevant), sanctions and politically exposed persons (PEP) screening, open-source and social media review, and Standard or Enhanced DBS checks (or equivalent) where the role legally qualifies.
Enhanced vetting is not a default. It must be justified by the role and the information classification, and applied consistently to every person in that tier—not selectively.
Handling Incomplete Verifications
Not every check will produce a clean, complete result. References go unreturned. Old employers no longer exist. Qualifications are awarded by institutions that have since closed. The standard does not require perfection; it requires that gaps are identified, alternatives are attempted, and unresolved gaps are documented with a risk decision before access is granted. A screening file that says “reference not obtained, alternative reference accepted, approved by [name]” is fine. A screening file that simply leaves the field blank is not.
Pro Tip: Tier your roles before you design your checks.
Create three or four tiers based on the sensitivity of information accessed and the level of system privilege, define the mandatory and optional checks for each tier, and map every job description to a tier. This is the artefact auditors want to see — and it also stops well-meaning managers from quietly skipping checks on hires they happen to like.
How to Perform ISO 27001 Background Checks
The mechanics matter less than the consistency. Auditors are looking for a process, evidence the process was followed, and a way to demonstrate that exceptions were rare and approved.
Develop a Formal Screening Policy
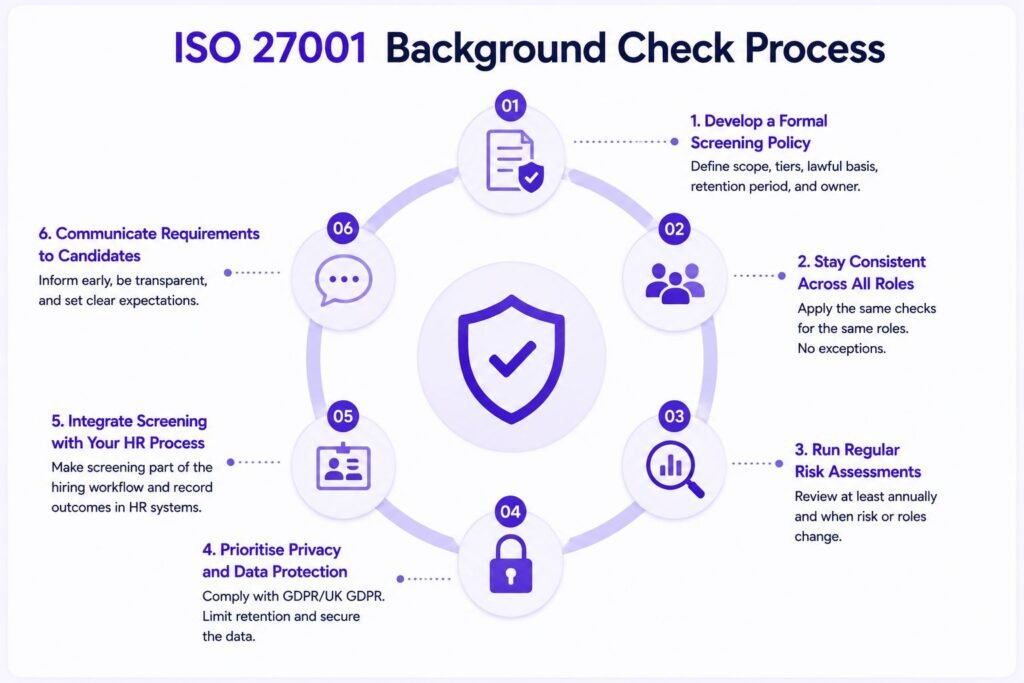
The policy is the foundation. It should state the scope (who is covered), the tiers (what level of check applies to what role), the lawful basis for processing the data, the retention period for screening records, and the named owner of the process. It should reference applicable employment law, data protection law, and any sector-specific regulation.
Organisations that have identified gaps in their current documentation can benefit from engaging internal audit services to benchmark what they have against what the standard expects.
Stay Consistent Across All Roles
Two people hired into equivalent roles should go through equivalent checks. Inconsistency is the fastest route to both a discrimination complaint and an audit finding.
If a check is mandatory for the role, it is mandatory for everyone in that role — no exceptions for referrals, contractors brought in at short notice, or founders who think the rule doesn’t apply to them.
Run Regular Risk Assessments
Roles change, regulations change, and the threat landscape changes. Review the screening policy at least annually, and trigger an interim review when the organisation adds new categories of data, enters a new regulated market, or significantly changes its access model.
Prioritise Privacy and Data Protection
Background checks involve personal data, and in many jurisdictions, special category data such as criminal convictions. Under GDPR compliance frameworks — including the UK GDPR and the Data Protection Act 2018 — criminal offence data is governed by Article 10 and Schedule 1, and it requires a specific lawful basis, not just consent.
The Information Commissioner’s Office has been clear that consent is rarely the right basis in an employment context, because the power imbalance undermines the “freely given” requirement.
Candidates must be told in advance what will be checked, why, how long the data will be kept, and what their rights are.
Records should be retained only as long as necessary — typically the duration of employment plus a defined retention period — and unsuccessful candidates’ data should be deleted within six to twelve months unless a specific legal basis justifies longer.
Integrate Screening with Your HR Process
Screening should be a step in the standard hiring workflow, not a parallel exercise managed by IT or security in isolation. The HR system should record the tier, the checks required, the completion status, and the date access was approved. Where a third-party screening provider is used, the HR record should still capture the outcome — not just a reference to the vendor’s portal.
Communicate Background Check Requirements to Candidates
Candidates should know at the application stage that the role requires screening and what the screening involves. This avoids late-stage withdrawal of offers, gives candidates the opportunity to disclose anything that might come up, and helps establish the lawful basis for processing the data. Transparency here is not just good practice — it is a legal requirement in most jurisdictions.
Applicability to Small Businesses, Tech Startups, and AI Companies
Smaller organisations sometimes assume Annex A 6.1 is overkill at their scale. It is not. The control is proportionate by design, but it is still required — and small organisations often have weaker compensating controls, which makes screening more important rather than less.
ISO 27001 Background Checks for Small Businesses
For a 15-person professional services firm, a baseline tier covering identity, right to work, qualification verification, and two references is usually sufficient for non-privileged roles. Anyone with administrative access to client data, finance systems, or production environments should additionally undergo a Basic DBS check (or local equivalent) and a more detailed reference review. The key is proportionality — scaling checks to actual risk rather than defaulting to the same level for everyone or applying nothing at all.
ISO 27001 Background Checks for Tech Startups
Tech startups frequently grant production access broadly because the team is small and the work is fluid. This makes the privileged-access tier larger in proportion than at a larger firm. A pragmatic baseline is to treat every engineer with production access as a privileged hire and apply enhanced checks accordingly. Founders and senior hires should not be exempt — the control applies to everyone, and an unscreened founder is exactly the kind of finding that lingers in audit reports and becomes a case study in what not to do.
ISO 27001 Background Checks for AI Companies
AI companies face a specific variant of the problem. Training data and model weights can be the most valuable assets in the organisation, and the engineers, researchers, and annotators with access to them often work across model development, evaluation, and deployment in ways that blur the usual access boundaries.
Screening should account for the full range of people who can read training data, modify model code, or export weights — including contracted research partners and annotation vendors. Confidentiality and IP assignment terms in the contract are necessary but not sufficient; the screening control sits upstream of them.
Worth Knowing: Insider threat research
Insider threat research — including data summarised in Wikipedia's overview of insider threats and explored in depth by the Cybersecurity and Infrastructure Security Agency (CISA) — consistently finds that insider incidents are most damaging when the actor had been given elevated access without commensurate vetting. The cost of the check is trivial compared to the cost of the incident.
ISO 27001 Background Check Policy: What to Include
A screening policy does not need to be long. It needs to be specific, evidence-based, and consistently applied.
How to Write an Annex A 6.1 Screening Policy
A workable structure has seven sections.
- Purpose and scope state what the policy covers and who it applies to.
- Roles and responsibilities name the owner (typically the HR lead, with security sign-off).
- Tiers and checks define the screening levels and what each includes.
- Process describes the workflow from offer to access approval.
- Records and retention specify what is kept, where, and for how long.
- Legal basis and candidate rights set out the data protection position.
- Exceptions and approvals state who can authorise a deviation and how it must be recorded.
Key Considerations When Documenting Your Background Check Process
The policy should reference but not duplicate other documents: the data protection notice given to candidates, the supplier vetting policy, and the access control policy. It should name a review cadence — typically annual — and a trigger list for interim reviews.
It should be approved at the right level of seniority and stored where the auditor can find it without being asked twice. Being aware of the common pitfalls in ISO 27001 documentation at this stage will save significant remediation effort later.
Ownership of Annex A 6.1
The control is most often owned by the HR manager, with information security or compliance providing oversight. This works because HR holds the candidate relationship, the lawful basis, and the records — while security and compliance hold the tiering logic, the risk decisions, and the access approval.
Both functions should be visible in the policy, and neither should be able to approve access without the other’s input, where the role sits in an elevated tier.
What Changed from ISO 27001:2013 to ISO 27001:2022
In the 2013 version, screening sat at Annex A 7.1.1 within a 14-domain structure. The 2022 update consolidated the 114 controls of 2013 into 93 controls under four themes (Organisational, People, Physical, Technological), and screening moved to A 6.1 within the People theme.
The substantive requirement has not changed dramatically. The control text was tightened, the requirement for ongoing screening was made more explicit, and the proportionality language was strengthened.
Organisations certified under 2013 and transitioning to 2022 should expect their existing screening process to map across without major rework — but they should refresh the policy to reference the new control number and confirm that ongoing-screening triggers are explicitly documented rather than implied.
Related ISO 27001:2022 Controls Relevant to Background Checks
Screening does not stand alone. Several other Annex A controls connect to it directly, and understanding those relationships helps when mapping evidence across your ISMS documentation.
A 6.2 — Terms and Conditions of Employment
Employment contracts must state the information security responsibilities of the role. Screening confirms suitability for the role; the contract documents what the role then requires of the person filling it. Both need to exist, and both need to be in place before access is granted.
A 6.3 — Information Security Awareness, Education, and Training
Screening establishes a baseline of trust at hire. Training maintains and builds on it through the employment relationship. Both are required by the standard, and neither replaces the other — a well-screened employee who receives no security awareness training is still a risk.
A 6.6 — Confidentiality or Non-Disclosure Agreements
NDAs and confidentiality terms apply to everyone in scope of screening, including contractors and selected suppliers. The screening record and the signed NDA together evidence that the organisation has done what it can to protect information at the human layer.
A 5.15 — Access Control
Access control assumes the person being granted access has been vetted appropriately. Annex A 5.15 and A 6.1 are paired controls in practice: one defines who can have access, the other confirms the person is suitable to be that who.
An access control policy that grants privileged access without reference to screening status is incomplete regardless of how sophisticated the technical controls are.
Frequently Asked Questions: ISO 27001 Background Checks
Are Background Checks Mandatory for ISO 27001 Certification?
A 6.1 can technically be excluded through the Statement of Applicability, but in practice, it almost never is. Auditors will expect a documented justification for exclusion, and most organisations with employees handling in-scope data cannot make that justification credibly. Treat the control as mandatory unless you have a very specific and documented reason why it does not apply.
What Types of Roles Require Background Checks Under ISO 27001?
Every role with access to in-scope information or systems. The level of check varies with the risk tier, but the requirement to screen does not skip categories of staff. There is no carve-out for short-term contractors, interns, or senior leadership — if anything, those groups often warrant closer attention.
How Often Should ISO 27001 Background Checks Be Repeated?
There is no fixed interval mandated by the standard. The control requires ongoing screening, but this can be event-driven — role changes, promotions to privileged access, changes in regulatory requirements — rather than purely time-driven.
Some organisations re-verify identity and right to work annually; others rely on defined trigger events. Either approach is acceptable provided it is documented and applied consistently.
Do ISO 27001 Background Checks Apply to Contractors and Third Parties?
Yes, for any contractor or third-party personnel granted access to in-scope information or systems. The depth of the check can be delegated to the supplier under contract, but the obligation to confirm that screening was completed sits with the certified organisation. “Our supplier handles that” is not sufficient without evidence that the supplier actually did it.
How Do You Document Background Checks for an ISO 27001 Audit?
Maintain a screening register that records, for each person in scope: the role tier, the checks required, the date each check was completed, the outcome, the name of the reviewer, and the date access was approved.
The underlying evidence — signed reference letters, DBS certificates, qualification verifications — should be stored securely with appropriate access controls and retention rules applied.
What Happens If a Background Check Returns Adverse Information?
Adverse findings should never trigger automatic disqualification. The standard, and the Rehabilitation of Offenders Act 1974 in the UK along with comparable laws elsewhere, requires that adverse information is assessed for relevance to the role. A historical conviction unrelated to the responsibilities of the position is rarely a basis for refusal. A pattern of dishonesty in a role with financial access is a different matter. The decision, the reasoning, and the approval should all be documented.
Important: Blanket policies that exclude all candidates with any adverse finding are unlawful in most jurisdictions and are an audit finding waiting to happen. The control requires a defensible, individual assessment — not a blanket filter.
Closing Note
Annex A 6.1 is a short control that asks something straightforward: confirm the people you are about to trust are people worth trusting, document what you checked, and keep doing it as roles and risks change.
The organisations that pass this control cleanly are not the ones with the most exhaustive checks. They are the ones who decided what proportionate means for them, wrote it down, and applied it the same way to every hire.