/

  / Personal Data Protection Law in Bahrain, UAE, and Saudi Arabia

Personal Data Protection Law in Bahrain, UAE, and Saudi Arabia

Three Gulf states now run three different data protection regimes.

Saudi Arabia’s regulator has already issued dozens of enforcement decisions. Bahrain has had a working statute since 2019, and the UAE has a federal law on the books but is still waiting on the executive regulations that will give it teeth. For any company operating across the region, the practical question is no longer whether these laws apply but how far apart they sit, and where compliance built for one falls short of another.

This is a structured comparison of the personal data protection laws in Bahrain, UAE, and Saudi Arabia: what each one demands, where they converge on familiar GDPR principles, and the specific points where treating them as interchangeable will get you fined.
Personal Data Protection Law in Bahrain, UAE, and Saudi Arabia

The Three Laws at a Glance

Bahrain moved first. Law No. 30 of 2018, the Personal Data Protection Law (PDPL), came into force on August 1, 2019, making it the first comprehensive standalone data protection statute in the Gulf Cooperation Council. It is supplemented by ten ministerial resolutions issued in 2022 that cover transfers, security measures, and notification procedures.

The UAE followed with Federal Decree-Law No. 45 of 2021, effective January 2, 2022 — the country’s first federally applicable, GDPR-style law, issued alongside Federal Decree-Law No. 44 of 2021, which created the UAE Data Office as the federal regulator. The catch is that the executive regulations meant to flesh out timelines and penalties have still not been published, which leaves parts of the regime in a holding pattern.

Saudi Arabia’s Personal Data Protection Law, issued by Royal Decree M/19 in September 2021 and amended in March 2023, is the strictest and the most actively enforced of the three. It came into force on September 14, 2023, and a one-year grace period ended on September 14, 2024. Since then, every organization processing the personal data of people in the Kingdom has been fully on the hook.

Worth knowing: Saudi Arabia's PDPL

Saudi Arabia's PDPL protects a person's data not only during their lifetime but after death. That post-mortem protection is unusual among global privacy laws and means retention and disclosure decisions cannot assume an individual's rights simply lapse when they die.

Who the Laws Actually Reach

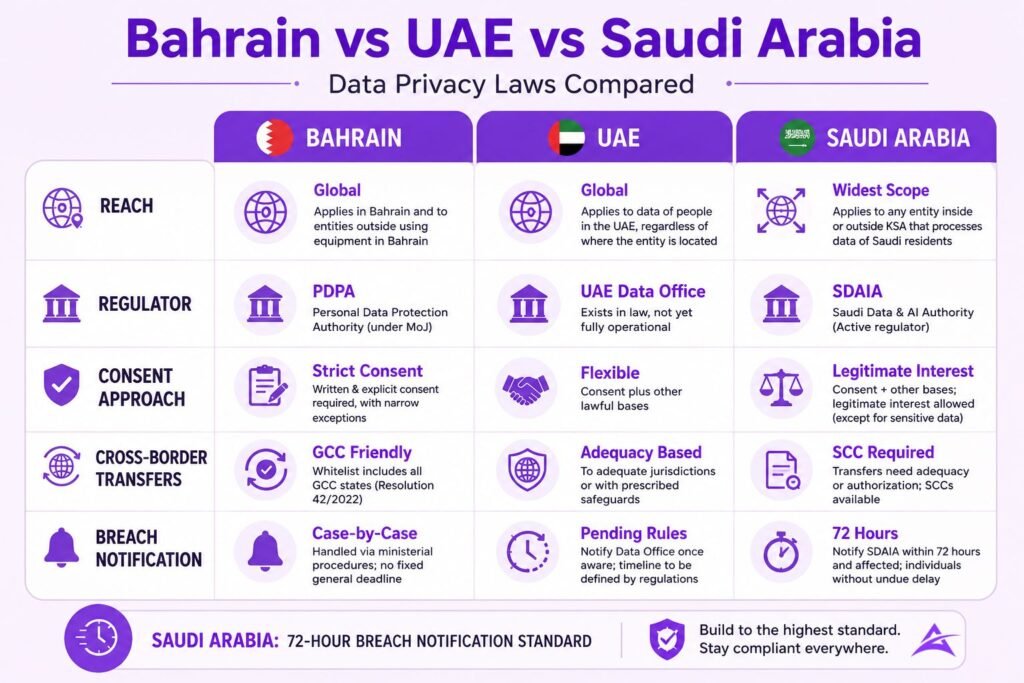
All three statutes reach beyond their own borders. Bahrain’s PDPL applies to anyone residing or doing business in Bahrain, and to entities outside the country that process personal data using equipment located inside it. The UAE law applies to the processing of data belonging to people in the UAE, regardless of where the controller or processor is based. Saudi Arabia goes furthest, applying to any entity inside or outside the Kingdom that processes the personal data of Saudi residents — a scope that pulls in international businesses that may never have considered themselves subject to Gulf regulation.

The big structural difference is the UAE’s free zones. The federal PDPL does not apply inside zones that maintain their own data protection regimes, most notably the Dubai International Finance Centre (DIFC) and the Abu Dhabi Global Market (ADGM), each of which runs its own established framework. A company in the DIFC answers to DIFC rules, not the federal law. That carve-out has no equivalent in Bahrain or Saudi Arabia, and it matters enormously for regional structuring decisions.

Ready for GCC data privacy compliance?

Talk to our experts and simplify Bahrain, UAE, and Saudi data privacy compliance.

The Regulators

Each country has its own supervisory authority, and they are at very different stages of maturity. Bahrain’s Personal Data Protection Authority (PDPA) operates under the Ministry of Justice, Islamic Affairs and Waqf and has full investigation, audit, and penalty powers. SDAIA — the Saudi Data and Artificial Intelligence Authority — is the current regulator in Saudi Arabia, with long-term supervision potentially moving to the National Data Management Office under the Kingdom’s wider data governance framework. SDAIA is visibly active: its enforcement committees issued 48 decisions confirming PDPL violations across the 2025 and 2026 review cycles, a level of regulatory output that should get the attention of any compliance team operating in the region.

The UAE is the outlier. The UAE Data Office exists in law but is not yet fully operational, and the Telecommunications and Digital Government Regulatory Authority was tasked with providing administrative support during the office’s early years. In practice this means data subjects in the UAE currently lack a clear federal route to lodge a complaint, and enforcement guidance is still maturing. That ambiguity cuts both ways: it reduces immediate enforcement risk, but it also makes it harder to know exactly what compliance looks like.
PDPL Bahrain UAE Saudi Arabia

Lawful Basis, Consent, and Core Principles

Consent sits at the center of all three regimes, but Bahrain leans on it hardest. Bahrain’s PDPL sets a default rule that personal data may not be processed without the data subject’s written and explicit consent, with a narrow set of alternative bases such as contract performance, legal obligation, and vital interests. Saudi Arabia and the UAE both recognize consent alongside other grounds, and Saudi Arabia’s amended law added legitimate interest as a basis — though it cannot be used for sensitive data and controllers are warned against treating consent as a convenient fallback when a more specific ground applies.

Beneath the lawful-basis question, the three laws share the principles that anyone familiar with the same GDPR-shaped foundation will recognize: lawfulness, fairness and transparency, purpose limitation, data minimization, accuracy, storage limitation, and security. The vocabulary and structure track the European model closely, and deliberately so. That means a mature GDPR program is a strong starting point, not a finished one — the architecture transfers, but the local rules introduce enough variation to demand dedicated attention.


Data Subject Rights

The rights packages are broadly similar across the three jurisdictions, but the enforcement emphasis differs. Individuals in all three countries can access their data, request correction, and object to certain processing. Saudi Arabia’s PDPL spells out the most comprehensive set — including access, correction, deletion, objection, and portability — and SDAIA has flagged failure to honor these requests as one of its most common enforcement findings, which means it is not a theoretical obligation. Bahrain grants access, correction, and a specific right to object to direct marketing such as behavioral targeting and SMS or email advertising. The UAE law likewise provides for access, correction, erasure, restriction, portability, and objection, though the procedural mechanics depend in part on the awaited executive regulations.

For organizations receiving high volumes of data subject requests across all three markets, the practical challenge is building workflows that satisfy each regime’s specific framing — not just a single generic process dressed up in three languages.


Registration, DPO, and Record-Keeping

This is where the day-to-day compliance burden diverges most visibly. Bahrain requires controllers to submit prior notifications or authorization requests to the PDPA for certain processing activities, and it maintains a register of accredited data protection officers — referred to in the law as Data Protection Guardians. Saudi Arabia requires controllers to register on the National Data Governance Platform, maintain records of processing activities, and appoint a DPO where they carry out large-scale or sensitive processing, per SDAIA’s dedicated rules on the role. The UAE requires the appointment of a DPO in defined circumstances and the keeping of processing records, with detail again deferred to the pending regulations.

Insider note: Bahrain quietly solved a problem the other two have not. Its adequacy list under Resolution 42/2022 includes all other GCC states, so transfers from Bahrain to Saudi Arabia, the UAE, Qatar, Kuwait, and Oman proceed without prior PDPA authorization. For a regional operation, routing certain intra-Gulf data flows through a Bahrain entity can remove an approval step that Saudi Arabia’s regime would otherwise require.


Cross-Border Transfers

Transfer rules are where the three laws feel least alike in practice. Bahrain prohibits transfers outside the Kingdom without the data subject’s specific consent unless the destination appears on a ministerial whitelist or a special authorization is issued — and as noted above, the whitelist already covers the rest of the GCC. Saudi Arabia restricts transfers under Article 29, permitting them only to countries SDAIA deems adequate or under explicit authorization; SDAIA issued standard contractual clauses and dedicated transfer regulations in September 2024 to provide compliant mechanisms for transfers that cannot rely on adequacy. The UAE law also restricts transfers to jurisdictions with adequate protection or under prescribed safeguards, with the specifics once more tied to the pending regulations.

The practical implication is that a single transfer mechanism — whether that is an SCC, a whitelist reliance, or a consent capture — will not work uniformly across all three. Each transfer route needs to be mapped and validated against the rules of the specific originating jurisdiction.


Breach Notification

This is the single clearest divergence across the three regimes, and the one most likely to trip up a unified incident response policy. Saudi Arabia imposes a hard deadline: controllers must notify SDAIA within 72 hours of becoming aware of a breach that poses a risk to data or data subjects, and must inform affected individuals without undue delay where the risk is serious. The UAE PDPL requires notification to the Data Office once a controller becomes aware of a breach, but a precise statutory timeline awaits the executive regulations, leaving the practical standard somewhat open. Bahrain does not set a single fixed general deadline equivalent to Saudi Arabia’s 72-hour rule, handling notification instead through its ministerial procedures — though failure to notify where required carries its own penalty.

Pro tip: Build your Incident Response

Build your incident response plan to the Saudi standard and apply it everywhere. A documented 72-hour clock with predefined breach-classification criteria and clear internal ownership satisfies the strictest regime in the region, and it gives you a defensible process in the UAE and Bahrain even while their procedural detail keeps shifting.

Penalties

The financial exposure differs by an order of magnitude across the three. Bahrain’s penalties top out at BHD 20,000 for serious violations such as processing without a lawful basis or unauthorized cross-border transfers, with failure to notify a breach drawing fines up to BHD 10,000, and imprisonment available for certain offenses. Saudi Arabia carries the heaviest sanctions: general violations attract fines up to SAR 5 million, doubled for repeat offenses, while disclosing or publishing sensitive personal data with intent to harm can bring imprisonment of up to two years and a fine of up to SAR 3 million. The UAE’s penalty structure is set to be defined in the executive regulations, and commentary widely anticipates administrative fines in the range of AED 50,000 to AED 5 million.

The gap between Bahrain’s ceiling and Saudi Arabia’s is not marginal — it reflects a deliberate regulatory choice to make non-compliance genuinely expensive. For large organizations, the reputational and operational consequences of an enforcement action in any of the three markets are likely to exceed the fines themselves, but the Saudi penalty structure removes any temptation to treat compliance as a low-stakes calculation.

Comparison of Major Provisions

Provision

Bahrain

UAE

Saudi Arabia

Legislation

PDPL, Law No. 30 of 2018

Federal Decree-Law No. 45 of 2021

PDPL, Royal Decree M/19 (2021, amended 2023)

In force

August 1, 2019

January 2, 2022

September 14, 2023

Regulator

Personal Data Protection Authority (PDPA)

UAE Data Office (not yet fully operational)

SDAIA

Default lawful basis

Explicit written consent

Consent plus alternatives

Consent plus alternatives including legitimate interest (non-sensitive)

Breach notification deadline

No single fixed deadline; ministerial procedures apply

Prompt notification; precise timeline pending regulations

72 hours to SDAIA; individuals notified without undue delay

Cross-border transfers

Whitelist (covers GCC) or consent or authorization

Adequacy or safeguards; detail pending regulations

SDAIA adequacy or SCCs or authorization

DPO requirement

Accredited Data Protection Guardian; mandatory for licensed financial institutions

Required in defined circumstances; detail pending regulations

Required for large-scale or sensitive processing

Maximum fine

BHD 20,000

Anticipated AED 50,000–5 million (pending regulations)

SAR 5 million (doubled for repeat offenses)

Free-zone carve-out

None

Yes — DIFC and ADGM operate separate regimes

None

Post-mortem data protection

No equivalent provision

No equivalent provision

Yes — rights extend beyond the data subject’s death

Building One Program Across Three Jurisdictions

The temptation is to pick the strictest law, comply with it, and assume the rest follow. That instinct is broadly right but incomplete. Saudi Arabia is the high-water mark on enforcement, breach timing, and penalties, so building to its 72-hour notification rule, registration requirements, and DPO expectations covers a great deal of ground. What it does not cover is the structural quirks: Bahrain’s consent-first default and whitelist transfer mechanism, and the UAE’s free-zone carve-out that may put part of your operation under DIFC or ADGM rules entirely.

A workable approach starts with a multi-jurisdictional gap assessment that maps where personal data actually flows between the three countries and out of the region. From there, a unified framework should adopt the strictest common requirement as the baseline, then layer country-specific controls on top: a Bahrain whitelist check before intra-GCC routing, a DIFC or ADGM determination for any UAE entity, and SDAIA registration and SCC mechanics for Saudi transfers. Vendor contracts need processor clauses that satisfy all three, and staff handling data in any of the markets need training that reflects local rules rather than a single generic module. The frameworks rhyme, but the details bite.

Underpinning all of this is a documentation and accountability structure that can demonstrate compliance to three different regulators with three different priorities. ISO 27001 certification provides a strong technical and organizational security baseline that is recognized across the region and maps naturally onto the security obligations in all three laws — it will not substitute for legal compliance, but it gives regulators and counterparties something concrete to point to, and it structures the internal controls that make compliance sustainable rather than reactive.

Ready for GCC data privacy compliance?

Talk to our experts and simplify Bahrain, UAE, and Saudi data privacy compliance.

The Bottom Line

Bahrain, the UAE, and Saudi Arabia have each built data protection laws on the same GDPR-shaped foundation, which makes a single coherent program achievable. The risk lies in the gaps between them: Saudi Arabia enforcing hard today, the UAE still waiting on the regulations that will define its edges, and Bahrain running its own consent and transfer logic. Treat the strictest regime as your floor, then account for the structural differences each country adds, and you have a defensible position across all three. Treat them as one law, and you will be compliant with none of them.

Frequently Asked Questions

Which is stricter: Bahrain, UAE, or Saudi Arabia's data protection law?

Saudi Arabia’s PDPL is the strictest in practice. It is fully enforced, carries the highest penalties, imposes a firm 72-hour breach notification deadline, and is backed by an active regulator that has already issued dozens of enforcement decisions. Bahrain has a mature and functioning regime, while the UAE is still developing the executive regulations that will complete its framework.

Yes. All three have extraterritorial reach. A company anywhere in the world that processes the personal data of people in Saudi Arabia, the UAE, or Bahrain can fall within scope, particularly if it offers goods or services to, or monitors the behavior of, individuals in those countries. The extraterritorial logic mirrors the GDPR’s Article 3 approach and should be taken seriously by any organization with Gulf-based customers or users.

No, but it is central, and Bahrain in particular treats explicit written consent as the default. All three laws recognize alternative bases such as contract performance, legal obligation, and vital interests, and Saudi Arabia’s amended law also allows legitimate interest for non-sensitive data. Controllers should identify the most appropriate lawful basis for each processing activity rather than defaulting to consent across the board.

They share the GDPR’s core architecture: lawful bases, data subject rights, breach notification, accountability, and transfer restrictions. The main differences are substantially lower maximum fines in Bahrain, the use of regulator-issued adequacy decisions and authorization mechanisms for transfers rather than the EU’s adequacy framework, and varying degrees of enforcement maturity across the three regulators.

Not universally. Saudi Arabia and the UAE require a DPO in defined circumstances, typically large-scale or sensitive processing. Bahrain maintains a register of accredited Data Protection Guardians, and recent financial-sector directives have made appointment mandatory for licensed institutions. Organizations operating across all three markets should assess the DPO requirement independently in each jurisdiction rather than applying a single determination.

Not automatically, but Bahrain makes it easier than the others. Bahrain’s adequacy list covers the other GCC states, so transfers from Bahrain into the region avoid prior authorization. Transfers out of Saudi Arabia still require SDAIA adequacy determination, SCCs, or specific authorization. UAE transfers depend on safeguards detailed in its pending regulations. For now, Bahrain’s whitelist mechanism is the most streamlined intra-GCC transfer route available.

Axipro Author

Picture of Pedro Dias

Pedro Dias

Pedro has been writing online for over 10 years. With experience in all things programming, cyber security, and compliance, he is our editor-in-chief at Axipro.

Blog Highlights

Explore More Articles

Vanta can tell you a control is failing within the hour. It cannot rewrite your access review process, decide which systems belong in audit scope, or explain to a CPA why a test that shows red is actually fine. That work falls to people, and choosing the right ones is the difference between a 6-week path to audit readiness and a 6-month slog that ends with your Vanta subscription renewing before you have a report. This guide ranks the 7 best Vanta deployment services for 2026, explains what each one is good at, and covers what most comparison pages skip: how long this really takes, what it costs, and how to spot a partner who’ll hand you a half-configured platform and disappear. What Is a Vanta Deployment Service? A Vanta deployment service is a hands-on engagement where a specialist firm sets up, configures, and operationalizes Vanta so your company reaches audit readiness for one or more compliance frameworks. Vanta itself is a compliance automation and trust management platform: it connects to your cloud, identity provider, code repositories, HR system, and endpoints, then runs automated tests and maps the evidence to frameworks such as SOC 2, ISO 27001, HIPAA, and GDPR. The platform automates evidence collection and continuous monitoring. It doesn’t put controls in place for you. A deployment partner handles the judgment work around the tool: scoping, gap analysis, control mapping, policy writing, risk assessment, remediation of failing tests, and coordination with the audit firm. The best partners also stay on after the audit, because a Vanta instance nobody owns degrades fast. Worth Knowing: Vanta is a software vendor, not an auditor. Vanta is a software vendor, not an auditor. Your SOC 2 report still comes from a licensed CPA firm under AICPA attestation standards, and your ISO 27001 certificate comes from an accredited certification body. A deployment partner sits between the platform and the auditor. 1. Axipro Best for: SaaS and technology companies that want Vanta deployed, controls implemented, and the audit delivered by one accountable team, fast. Axipro is an authorized Vanta partner and a Drata Elite Partner, so its team works inside both leading compliance automation platforms every day. Founded in 2023, it has served 200+ clients from offices in the US, UK, and Bahrain, with a 100% audit success rate across 200+ certified clients. What puts Axipro first is scope. Most Vanta partners configure the platform and leave control implementation to you. Axipro’s Achievement Plan covers the whole path: kick-off and Vanta setup, gap analysis, a full policy and procedure suite, risk assessment and treatment, control implementation, vulnerability scanning, an internal audit, and external audit facilitation with an independent auditor. Clients get a dedicated infosec team over Slack, and the Achievement Plan comes with guaranteed certification. The other reason is speed. Axipro typically reaches SOC 2 readiness in around four weeks and ISO 27001 certification readiness in as little as six. It supports 20+ frameworks, including SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CMMC, ISO 42001, and the EU AI Act, plus Gulf frameworks such as NCA ECC and SAMA CSF that most US-only partners cannot cover. Teams that want to test the relationship first can start with the free 30-day Compliance Accelerator Plan, which includes Vanta setup, gap analysis, and policy documentation, and continue into ongoing vCISO and continuous monitoring through the Trust Assurance Plan after certification. Watch for: Axipro is built for companies that want the work done for them. Teams that want a light-touch coaching engagement and plan to run the program in-house will use only part of what it offers. 2. Control and Function Best for: US SaaS companies of roughly 10 to 60 people that want SOC 2 and ISO 27001 run as one fixed-price project. Control and Function is a Denver-based consultancy built around fixed-scope, fixed-price readiness for small SaaS teams that have no compliance department. Its sweet spot is the dual-framework engagement: building SOC 2 and ISO 27001 from one shared control set rather than running two projects back to back. It also covers HIPAA for healthtech and maps ed-tech requirements such as FERPA and HECVAT. The firm is platform-neutral, so it works inside Vanta rather than reselling it, and it is explicit about handing off cleanly to an independent auditor. It’s also one of the few firms here that publishes prices, with readiness coaching starting around $8,000 and full readiness around $15,000. Watch for: The framework range is narrower than larger partners. Companies that need PCI DSS, CMMC, or international frameworks will need a second provider. 3. Neutral Partners Best for: Growing companies that need managed GRC across SOC 2, ISO 27001, CMMC, and FedRAMP without hiring an internal compliance team. Neutral Partners, based in Miami, runs a managed GRC model. It builds and documents the compliance program, tests it through internal audits, and then hands off to the relevant independent assessor: a CPA firm for SOC 2, a certification body for ISO 27001, or a C3PAO for CMMC. It never issues the certificate itself, which keeps the independence question simple. Its framework coverage leans toward regulated and government-adjacent work, including CMMC, FedRAMP, PCI DSS, HIPAA, and HITRUST. That makes it worth a look for defense suppliers and companies selling to the public sector. Watch for: Vanta isn’t its main focus. Ask for recent Vanta deployment examples in your framework before signing. 4. Kobalt.io Best for: Small and mid-sized businesses that want Vanta plus managed security operations. Canada-based Kobalt.io markets itself as one of Vanta’s leading global service partners. Its Vanta practice covers policy and control development inside the platform, custom control mapping where standard controls do not fit, and an applicability review of Vanta’s tests. The broader appeal is its managed security services, which suit companies that want compliance and security operations from the same provider. 5. AuditPeak Best for: Startups that want a readiness and audit-preparation partner focused narrowly on SOC 2. AuditPeak focuses on SOC 2 audit readiness for early-stage companies working in

Compliance software collects the evidence. A consultant builds the system that evidence is meant to prove. That’s the real difference in the ISO 27001 consultant vs software decision, and most teams only figure it out after they’ve bought one and realized they still need the other. Below, we compare what each route covers, where it breaks down, and what it costs you in time, money, and your team’s hours. Short version: software on its own works for a small group of companies. For most SaaS and tech scale-ups trying to get an enterprise deal over the line, consultant-led implementation on a compliance platform is the faster and safer path to a certificate. Quick Answer: Consultant, Software, or Both? Software-only works if you already have an in-house security lead who’s taken a company through ISO/IEC 27001 before and has the time to own the project. Consultant-only still makes sense if you run mostly on-premise or legacy systems that platforms barely integrate with. For everyone else, which means most cloud-native companies under a few hundred people, a hybrid works best: a platform to handle evidence and monitoring, and a consultant to build the management system and stand behind it in front of an auditor. Here’s why. What an ISO 27001 Consultant Handles ISO/IEC 27001:2022 is a management system standard. Clauses 4 to 10 cover how you run information security, and Annex A lists 93 controls you pick from based on risk. Almost none of it is box-ticking. Most of it comes down to judgment calls about your business, and that’s what you’re paying a consultant for. Scoping, Gap Analysis and Risk Assessment Scope is the first decision you make, and the most expensive one to get wrong. Go too wide and you’ll spend months on controls for systems no customer asks about. Go too narrow and the certificate won’t get through the procurement review it was supposed to pass. A consultant scopes around the deals you’re trying to close, runs a gap analysis, and builds a risk assessment based on your real assets and threats. That’s the document auditors dig into hardest. ISMS Documentation and Policy Writing The standard asks for a specific set of documents: the ISMS scope, information security policy, risk assessment and treatment methodology, Statement of Applicability, risk treatment plan, and evidence of competence, monitoring, internal audit, and management review. A consultant writes these around how your company works day to day, instead of how a template imagines it works. Auditors check whether you follow your own procedures, so a mismatch shows up fast. Internal Audit and Certification Audit Support You need an internal audit before certification, and Clause 9.2 says the auditor has to be objective and impartial. In a small company, the people who built the ISMS can’t credibly audit it, so most teams outsource it through ISO 27001 internal audit services. A good consultant also gets your team ready for the Stage 1 and Stage 2 audits, joins the conversations that matter, and handles corrective actions if the auditor raises nonconformities.  What ISO 27001 Compliance Software Handles Compliance automation platforms, often called GRC platforms, have changed how cloud-native companies get certified. They’re very good at the repetitive, evidence-heavy side of the work. Automated Evidence Collection and Continuous Control Monitoring The platform plugs into your cloud provider, identity provider, code repos, HR system, and device management tools, then pulls evidence on its own. It’ll flag an unencrypted storage bucket, an ex-employee who still has access, or a laptop without disk encryption. For technical controls, that saves weeks of screenshots and spreadsheet tracking. Policy Templates and Annex A Control Mapping Most platforms come with a policy library and map each control to the ISO 27001 clauses and Annex A. You get a starting point and a clear view of which controls have evidence and which don’t. Auditor Access and Ongoing Compliance Tracking Auditors can log in and review evidence themselves, which cuts down fieldwork. After you’re certified, dashboards show when controls slip between surveillance audits, so you aren’t rebuilding evidence from scratch every year. Where Each Approach Falls Short Neither route covers everything by itself. The good news is that the ways each one fails are predictable, so you can plan around them. Limits of Compliance Automation Platforms A platform can tell you a control is failing. It can’t decide your scope, run your risk assessment, write a policy that matches your operations, convince your CTO to change the offboarding process, or explain to an auditor why you excluded a control from your Statement of Applicability. Templates can also make you feel further along than you are. A dashboard at 90% can hide an ISMS that won’t survive Stage 1, because the missing 10% is the management system itself. Insider Note: The Stage 1 problem we see most on software-only projects is a risk assessment copied straight from the platform’s default risk library. The risks are generic, the scores are almost identical, and nothing ties back to the company’s own assets. Auditors notice within minutes, and it weakens the Statement of Applicability that’s built on it. The other problem is ownership. Software assumes someone inside the company will drive the project. At most startups that’s a CTO or ops lead who already has a full-time job, and the subscription renews whether the work gets done or not. Limits of a Consultant-Only Approach A consultant working without automation spends billable days on things a platform does for free, like chasing screenshots, updating evidence trackers, and collecting the same proof again before every surveillance audit. You pay more and wait longer. You also end up with a program that’s only accurate on the day it’s handed over. Once the engagement ends, the evidence goes stale and year-two surveillance turns into a scramble. ISO 27001 Consultant vs Software: Side-by-Side Comparison Factor Consultant only Software only Hybrid (consultant + platform) Time to audit readiness 3 to 6+ months Highly variable; depends on internal expertise As little as 6 weeks for well-scoped

Uzbekistan regulates artificial intelligence through two documents. The first is Law ZRU-1115, signed on 21 January 2026. It amends existing legislation to define AI, stops anyone from basing decisions about people’s rights on AI output alone, and fines companies that process personal data unlawfully with AI. The second is the set of Ethical Rules approved by Order No. 3787, in force since 17 June 2026, which spell out what developers, implementers, and users actually have to do. Uzbekistan hasn’t passed a standalone AI act, and its rules don’t sort systems into risk tiers or require conformity assessments. The framework is short and blunt, and it’s already enforceable. Below we walk through what each document requires, who it applies to, how it stacks up against the EU AI Act, and what a company using AI in Uzbekistan should do next. Uzbekistan AI Regulation at a Glance (TL;DR) Instrument Date What it does Who it binds Law ZRU-1115 Signed 21 January 2026 Defines AI in law, sets general rules for AI-built information resources and systems, bans legally significant decisions based only on AI, adds fines for unlawful AI processing of personal data State bodies, organizations, website owners, anyone processing personal data with AI Order No. 3787 (Ethical Rules) Registered 14 March 2026, in force 17 June 2026 Sets eight mandatory ethical principles and lists rights and obligations for developers, implementers, and users Individuals and companies developing, implementing, or using AI in Uzbekistan Law No. 1125 (Personal Data amendments) Adopted 26 March 2026 Limits data localization to biometric, genetic, and local telecom user data, and allows cross-border transfers under conditions Personal data operators, including AI providers AI Strategy until 2030 (RP-358) 14 October 2024 Sets national targets for AI adoption, infrastructure, and skills Government bodies What Is Law ZRU-1115? The law’s official title is a mouthful: “On making additions and changes to certain legislative acts of the Republic of Uzbekistan in connection with the regulation of relations arising from the use of artificial intelligence.” Put simply, it’s an amending law. Instead of creating a new AI code, it writes AI into laws that were already on the books. When It Was Signed and When It Took Effect The Legislative Chamber of the Oliy Majlis adopted the bill on 12 August 2025, and the Senate approved it on 1 November 2025. President Shavkat Mirziyoyev signed it on 21 January 2026. You can read the official text in Lex.uz, Uzbekistan’s national legislation database. The law set out the principles and the penalties. The day-to-day detail arrived later with the Ethical Rules, which came into force on 17 June 2026. For compliance planning, treat mid-June 2026 as the point when the whole framework started applying. Why Uzbekistan Amended Existing Laws Instead of Passing a Standalone AI Act Uzbekistan wants more AI, not less. Its national strategy sets numeric targets for adoption, investment, and local computing capacity, and a heavy EU-style act would have worked against them. So lawmakers kept it light. They defined AI, drew two hard lines (human control over decisions that affect people’s rights, and protection of personal data), and left the Ministry of Digital Technologies to fill in the rest through secondary rules. Businesses get less legal certainty, and the government gets to move faster. Which Laws ZRU-1115 Changes For businesses, two amendments matter most. The Law “On Informatization” (ZRU-560-II, 2003) now contains a legal definition of AI, a new article on using AI in information resources and systems, duties for website owners, and updated powers for the ministry in charge. The Code on Administrative Liability now includes an offense for processing and spreading personal data unlawfully using AI. The Legal Definition of Artificial Intelligence in Uzbekistan Under the amended Law “On Informatization,” AI is a set of technological solutions that imitate human cognitive functions, including learning on their own and solving problems, and that produce results on specific tasks comparable to what a person could do. That’s deliberately broad. It covers generative AI, machine learning classifiers, recommendation engines, and most agentic systems. The Ethical Rules add a narrower term, the AI system: software built on AI that can find, collect, store, analyze, process, evaluate, and use data, and make decisions on its own based on that data. If your product makes a decision from data, or shapes one, assume it counts. Key Rules Introduced by Law ZRU-1115 General Principles for Using AI in Information Systems and Resources The new article in the Law “On Informatization” starts from harm. Information resources created with AI, and information systems running on AI, must not harm people’s life, health, freedom, honor, or dignity, or violate their other inalienable rights. The standard is short and open-ended. It gives regulators something to enforce against without saying in advance what counts as harm. Principle-based rules like this deserve to be taken seriously precisely because the edges are undefined. Human Oversight: No Decisions on Rights and Freedoms Based Solely on AI Most coverage leads with this provision, and it’s easy to see why. When someone makes a legally significant decision that affects human rights and freedoms, they can’t rely only on conclusions produced by AI systems or AI-built information resources. AI can feed into the decision, but a person has to make it. That applies to loan denials, benefit eligibility, hiring rejections, licensing outcomes, and disciplinary action. In each case, someone needs to look at the AI output and own the final call. Insider Note: In AI governance engagements, teams rarely struggle to show that a review step exists. What they struggle to show is that the reviewer could disagree, and sometimes did. If a human clicks “approve” on every AI recommendation and nobody ever records an override, auditors will see automation with a signature on top. Build the override path and log when people use it, starting on day one. Powers of the Authorized State Body (Ministry of Digital Technologies) ZRU-1115 makes the Ministry of Digital Technologies the authorized state body for AI. Among its new jobs, it’s