Here are real numbers to anchor on: Axipro delivers ISO 42001 readiness for $4,000 if you’re under 50 employees and $5,500 if you’re over, and the GRC platform plus accredited audit adds roughly $4,000 to $7,000 on top. A mid-sized tech firm lands at around $10,000 to $15,000 all-in for year one. A small team comes in under $10,000.
If you’ve been researching this topic, those figures probably look wrong to you. Published cost guides quote $85,000 to $320,000 for mid-market ISO 42001 certification. This article explains the gap: those guides price a traditional consulting-led engagement, where consultants bill day rates to build everything by hand. Automation-supported delivery, where a GRC platform collects the evidence and a fixed-fee team does the thinking, produces a completely different number. We break down both models phase by phase so you can budget against the delivery model you actually intend to buy.
Let Axipro help you build a business continuity plan that's practical, compliant, and audit-ready.
Schedule Your Free Assessment Today
What ISO 42001 Consulting Includes for Mid-Sized Tech Firms
ISO/IEC 42001 is the first certifiable international standard for an AI Management System (AIMS). Published in December 2023, it applies the familiar ISO management system structure to AI governance: scoped policies, AI risk and impact assessments, Annex A controls, a Statement of Applicability, internal audits, and a two-stage certification audit by an accredited certification body.
Scope of Consulting Engagements
A typical engagement covers five things: scoping the AIMS and building an AI system inventory, running a gap analysis against the standard, designing and documenting the management system, supporting control rollout, and preparing for the Stage 1 and Stage 2 audits. Under the traditional model, consultants hand-build each phase and bill for the hours. Under the automation-supported model, a fixed-fee readiness package covers the same ground while the platform does the mechanical work.
Typical Deliverables from an ISO 42001 Consultant
Expect a defined AIMS scope statement, an AI system inventory and risk register, AI impact assessments for in-scope systems, a policy and procedure set mapped to Annex A, a Statement of Applicability, training materials, an internal audit report, and audit-day support. If a proposal can’t name its deliverables this concretely, that tells you something about how well the consultant knows the standard.
How Mid-Sized Tech Firms Differ from Startups and Enterprises
Mid-sized firms sit in an awkward middle. They run more AI systems across more teams than a 15-person startup, so scoping, interviews, and evidence collection all take longer, and fixed-fee providers price them in a higher tier as a result. Unlike enterprises, though, they rarely need multi-site audit sampling or a dedicated AI governance function, so the six-figure quotes written for enterprises don’t apply to them either.
Average Cost of ISO 42001 Consulting
Typical Price Range for Mid-Sized Tech Firms
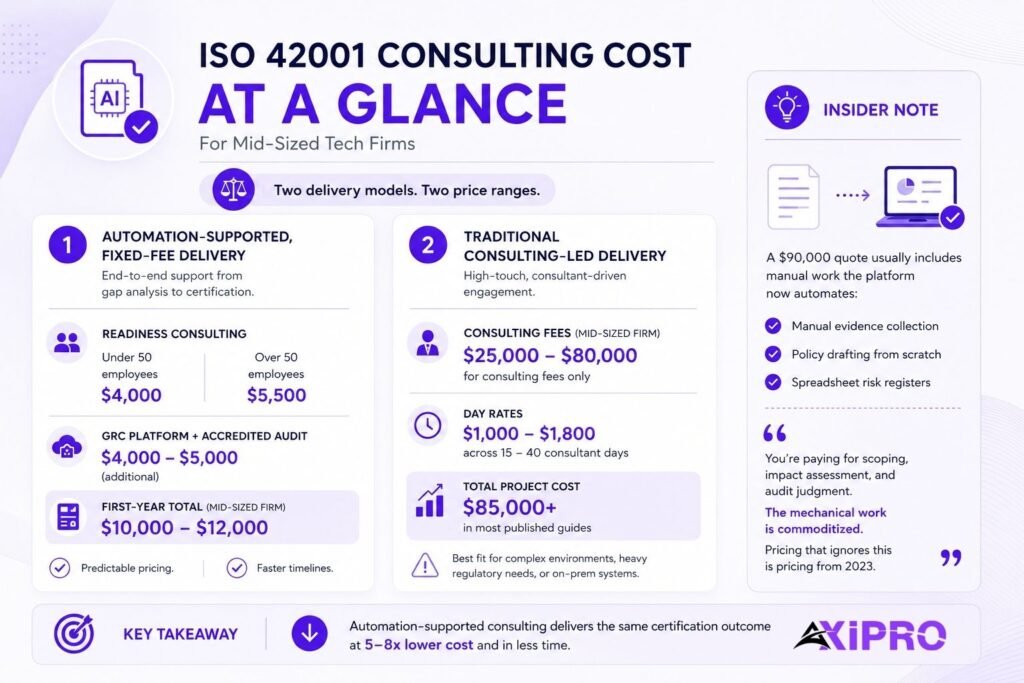
Two delivery models, two price ranges.
Automation-supported, fixed-fee delivery: readiness consulting at $4,000 for companies under 50 employees and $5,500 for companies over 50, covering the engagement from gap analysis through certification support. The GRC platform and accredited audit add roughly $4,000 to $5,000, so a mid-sized firm’s first-year total comes to around $10,000 to $12,000.
Traditional consulting-led delivery: $25,000 to $80,000 in consulting fees alone for a mid-sized firm, built on day rates of $1,000 to $1,800 across 15 to 40 consultant days. This is the model behind the $85,000-plus totals in most published guides. It still makes sense in a few situations: on-prem infrastructure the platforms can’t see, heavy regulatory overlays, or a board that wants a named Big Four partner on the engagement.
The market is young enough that quotes for identical scope can differ by a factor of five. ISO 42001 certificates only started appearing in volume in 2024, and plenty of consultants quoting today have never taken a client through a Stage 2 audit.
Insider Note: When a mid-sized firm shows us a $90,000 quote for ISO 42001, the line items usually reveal hand-built work the platform now automates: manual evidence collection, policy drafting from scratch, spreadsheet-based risk registers. What you’re actually paying a consultant for is scoping, impact assessment methodology, and audit judgment. The mechanical work has been commoditized, and pricing that ignores this is pricing from 2023.
Hourly vs Project-Based Consulting Rates
Experienced AI governance consultants charge $150 to $300 per hour in the North American and UK markets. Hourly billing works for targeted needs: reviewing an impact assessment methodology, answering auditor questions, validating a control design. For a full implementation it’s a false economy, since open-ended hours remove any incentive to compress the work. Fixed-fee delivery flips that incentive, and that’s a big part of why it prices so much lower.
Fixed-Fee vs Retainer Engagement Models
| Model | Typical cost | Best for | Watch out for |
|---|---|---|---|
| Fixed-fee readiness package | $4,000 (under 50 employees) / $5,500 (over 50) | First certification with defined scope | Packages that exclude audit facilitation |
| Traditional fixed-fee project | $25,000 to $80,000 | Complex scopes, heavy regulatory overlay | Paying consulting rates for automatable work |
| Monthly retainer | $2,000 to $8,000/month | Spreading work over 6 to 12 months | Engagements that drift without a certification date |
| Hourly / ad hoc | $150 to $300/hour | Targeted reviews, audit-day support | Costs compounding on open-ended work |
| Fractional AI governance officer | $3,000 to $10,000/month | Post-certification ownership without a hire | Thin coverage if the fractional lead is overloaded |
Fixed-fee is the right default for a first certification. It moves delivery risk to the provider and forces both sides to agree scope upfront. Fractional arrangements earn their keep after certification, once the work shifts from building the AIMS to running it.
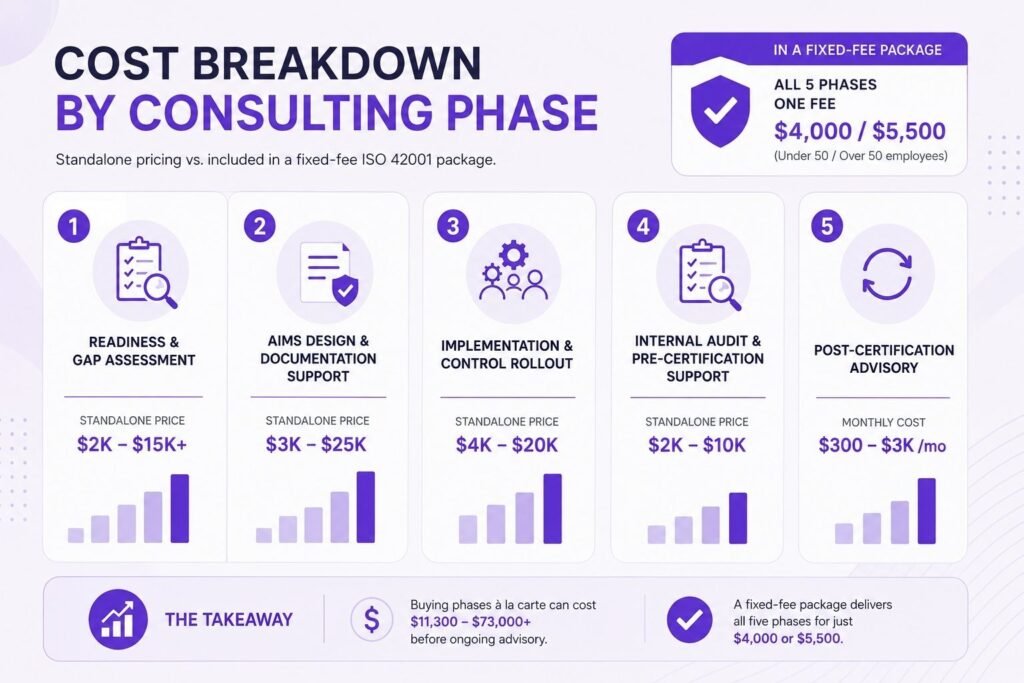
Cost Breakdown by Consulting Phase
The figures below show what each phase costs when you buy it separately from a traditional consultancy. Inside a fixed-fee package, all five phases sit within the single $4,000 or $5,500 engagement fee, and that’s exactly why the totals diverge so sharply.
Readiness and Gap Assessment Fees
Standalone price: $2,000 to $15,000, often more than an entire fixed-fee engagement. Either way, this is the highest-value work relative to its cost. The AI system inventory and gap analysis determine everything that follows, including whether you need the rest of the engagement at all.
AIMS Design and Documentation Support
Standalone price: $3,000 to $25,000 for the AI policy, risk methodology, impact assessment templates, lifecycle procedures, supplier controls, and Statement of Applicability. Platform policy templates adapted by a practitioner collapse most of this cost. Documentation written from a blank page is where traditional engagements burn the most billable days.
Implementation and Control Rollout
Standalone price: $4,000 to $20,000. The consultant supports training, model documentation practices, human oversight mechanisms, logging, and third-party AI supplier management. Your internal team does most of the actual work in this phase no matter which model you pick, so the real cost here is employee hours rather than fees.
Internal Audit and Pre-Certification Support
Standalone price: $2,000 to $10,000. ISO 42001 requires an internal audit that’s independent of the people who built the system, and that’s why most mid-sized firms outsource it. Axipro includes the internal audit within its end-to-end plans; bought alone, internal audit support starts from $1,000 for narrow scopes.
Post-Certification Advisory Costs
A few hundred dollars to $3,000 per month, depending on how much you keep in-house. Surveillance audits arrive annually, the AI inventory keeps changing, and impact assessments need refreshing whenever models or use cases change. Maintenance plans that bundle vCISO support and surveillance audit prep sit at the low end of that range. Standalone advisory retainers from traditional firms sit at the top.
Factors That Influence ISO 42001 Consulting Costs for Mid-Sized Tech Firms
Number of AI Systems and Use Cases in Scope
Scope is the single biggest cost driver at any company size. Each in-scope AI system needs an inventory entry, a risk assessment, an impact assessment, and lifecycle evidence. Ten systems cost meaningfully more to certify than three, and that shows up as more internal hours and more audit days even when the readiness fee is fixed.
Pro Tip: Certify a deliberately narrow scope first.
Certify a deliberately narrow scope first. Define the AIMS around your customer-facing AI products rather than every internal tool that touches a model, get certified, then expand scope at the first surveillance audit. Scope discipline is what keeps audit days, and therefore audit fees, at the bottom of the range.
Existing Maturity (ISO 27001, SOC 2, NIST AI RMF)
ISO 42001 shares its management system skeleton with ISO 27001: risk process, document control, internal audit, management review. Firms with a live ISO 27001 program typically cut ISO 42001 implementation effort by 40 to 60 percent, since they’re extending existing machinery instead of building it. SOC 2 helps less but still counts. Prior alignment with the NIST AI Risk Management Framework shortens the AI-specific work too, because the risk thinking is already done.
Company Headcount and Number of Business Units
Fixed-fee providers price on headcount because it’s a fair proxy for effort, and the under-50 and over-50 tiers reflect that. Structure matters more than the raw number, though. A 300-person firm with one product line certifies faster than a 120-person firm with four business units each running its own AI experiments, because every extra unit adds interviews, evidence owners, and coordination overhead.
Geographic Footprint and Multi-Site Operations
Multiple offices raise audit costs. Certification bodies sample sites during Stage 2 and surveillance audits, and controls have to demonstrably operate the same way everywhere. A firm with offices across the US, UK, and the Gulf should expect the audit component to run 15 to 30 percent above single-site equivalents.
Regulatory Exposure (EU AI Act, Sector-Specific Rules)
The EU AI Act’s main obligations entered into application on 2 August 2026, and enforcement now runs at national and EU level, even as the Commission’s Digital Omnibus proposal would tie the high-risk rules to the availability of harmonized standards. If your product qualifies as a high-risk AI system, you face conformity work that overlaps with ISO 42001 but goes beyond it, and providers price that extra work in.
Important: ISO 42001 certification doesn’t equal EU AI Act compliance. The standard is a management system framework; the Act imposes product-level legal requirements on specific systems. A consultant selling certification as an AI Act compliance solution is either confused or overselling, and both should worry you.
In-House GRC Capacity vs Full Outsourcing
A firm with a competent GRC lead who can own evidence collection and policy adaptation needs 30 to 50 percent fewer external hours than a firm outsourcing everything. Under a fixed-fee model this mostly changes how fast the engagement moves rather than what it costs, which is one more point in favor of fixed fees.
Consulting Cost vs Total ISO 42001 Investment
Consulting Fees as a Percentage of Total Certification Budget
Under the traditional model, consulting eats 30 to 50 percent of the total budget. Under the automation-supported model you can see the split in the sticker prices: a $5,500 readiness fee against roughly $4,000 to $5,000 in platform and audit costs, so consulting is about half of a much smaller total.
How Consulting Costs Compare to Audit and GRC Platform Costs
| Cost component | Automation-supported (mid-market) | Traditional consulting-led (mid-market) |
|---|---|---|
| Consulting / readiness | $5,500 ($4,000 under 50 employees) | $25,000 to $80,000 |
| GRC platform + accredited audit | $4,000 to $5,000 combined | $25,000 to $70,000 combined |
| Internal staff time | 150 to 400 hours | 300 to 800 hours |
| Indicative first-year total | ~$10,000 to $12,000 | $60,000 to $150,000 |
The gap between the columns is real, not padding. Narrow, well-prepared scopes need fewer audit days, and audit days are what certification bodies actually sell. In either model, the certification body must be independent of your consultant. Anyone offering to both implement and certify your AIMS is offering something accreditation rules don’t permit, and a certificate from an unaccredited body carries little weight in enterprise procurement.
Hidden Costs Mid-Sized Firms Often Overlook
Three costs surprise mid-market buyers most often. First, internal time: engineers and product owners spend real hours producing evidence, and that time has a payroll cost even though no invoice arrives. Second, the operating window. The AIMS has to run long enough to generate audit evidence before Stage 2, which stretches the calendar past the point where fees stop. Our breakdown of how long ISO 42001 certification takes covers why that window, not documentation, is usually the long pole. Third, surveillance: annual surveillance audits and program upkeep continue every year the certificate lives.
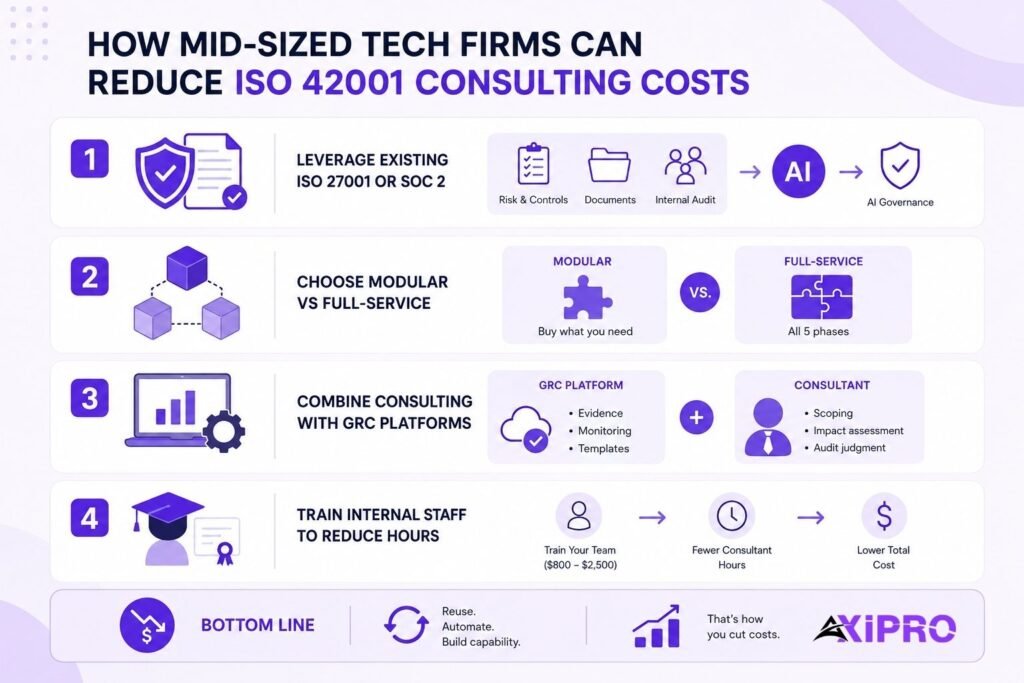
How Mid-Sized Tech Firms Can Reduce ISO 42001 Consulting Costs
Leveraging Existing ISO 27001 or SOC 2 Programs
Reuse is the biggest lever you have. Extend your existing risk methodology, document control, internal audit program, and management review to cover AI rather than duplicating them. If you’re weighing both frameworks, read our ISO 27001 certification cost breakdown, because bundling the two with one implementation partner and one audit firm commonly saves 20 to 30 percent against running them separately.
Choosing Modular vs Full-Service Consulting
When full-service delivery costs $4,000 to $5,500, the case for buying phases piecemeal mostly disappears. A standalone gap assessment from a traditional firm can cost more than an entire fixed-fee engagement. Modular buying still makes sense if you only need one independent piece, typically the internal audit. If you want to understand what each phase involves before committing either way, our step-by-step ISO 42001 implementation guide maps the full sequence.
Combining Consulting with GRC Automation Platforms
This stopped being a cost-reduction tactic a while ago. It’s the baseline now. GRC platforms such as Drata and Vanta ship ISO 42001 frameworks with automated evidence collection and pre-built policy templates, and the pricing difference between the two columns in the table above is mostly this. The platform handles evidence and monitoring; the consultant handles scoping, impact assessments, and audit judgment. Paying consulting day rates for work the platform automates is the single most common budgeting mistake in this market.
Training Internal Staff to Reduce Consultant Hours
Sending one person through an ISO 42001 lead implementer or lead auditor course costs $800 to $2,500. At traditional day rates that training pays back within the first engagement. Under a fixed-fee model its value shows up afterward, in keeping the AIMS running between audits and shrinking the post-certification support you need.
Let Axipro help you build a business continuity plan that's practical, compliant, and audit-ready.
Schedule Your Free Assessment Today
When Hiring an ISO 42001 Consultant Is Worth the Cost
Speed to Certification vs DIY Approaches
A supported mid-market engagement typically reaches certification readiness in 6 to 12 weeks of active work, with the full calendar to certificate running 4 to 8 months once you count the evidence window and audit scheduling. DIY efforts routinely take 9 to 15 months, mostly lost to scoping mistakes, rewritten documentation, and evidence gaps discovered at Stage 1. At a $4,000 to $5,500 readiness fee, the support pays for itself in calendar time alone if a deal is waiting on the certificate.
Reducing Audit Failure Risk
The expensive failure mode isn’t a failed audit. It’s a delayed one. Major nonconformities at Stage 2 trigger remediation, re-audit fees, and a slipped certificate date. Experienced implementers know where auditors probe and build the evidence trail accordingly, and a provider that’s confident in its process can put a certification guarantee behind the engagement.
Worth Knowing: Stage 1 Finding
The most common Stage 1 finding we see on AI management systems is an AI impact assessment that’s really an information security risk assessment with the word AI inserted. Auditors check whether the assessment considers affected individuals and societal impact, not just organizational risk, and a copied-over ISO 27001 methodology fails that test.
ROI for Sales, Procurement, and Enterprise Deals
ISO 42001 requests now show up in security questionnaires and RFPs that never mentioned AI before 2025, particularly from EU and regulated-industry buyers. When total certification cost sits around $10,000 to $12,000, a single unblocked enterprise deal covers it many times over. That arithmetic, not regulatory fear, is what drives most of the mid-market certifications we see.
How to Choose the Right ISO 42001 Consultant for a Mid-Sized Tech Firm
Qualifications and AI Governance Experience
Look for three things together: management system implementation experience (ISO 27001 pedigree counts), genuine AI literacy (can they discuss model lifecycle risks for your specific stack, not generically), and at least one completed ISO 42001 certification. Two of three is workable if the price reflects it. One of three means you’re funding their training.
Questions to Ask Before Signing an Engagement
Ask how many ISO 42001 certifications they’ve delivered end to end, which certification bodies they’ve worked with, whether the platform subscription and audit facilitation sit inside or outside the quoted fee, who actually does the work (partner or junior staff), and how they handle scope changes mid-engagement. Ask for a reference from a certified client of similar size.
Red Flags in Consulting Proposals
Walk away from proposals that certify through an affiliated certification body, quote a price without asking about your AI inventory, or bundle vague “AI Act compliance” into scope without naming which obligations. And judge cheap quotes by their deliverables rather than their price tag. A $4,000 fixed fee backed by a named deliverables list, a platform, and completed certifications is a delivery model. A $4,000 quote with none of those is a template dump, and auditors have learned to spot them.
The honest summary: ISO 42001 doesn’t have one average cost. It has two. Traditional consulting-led delivery runs $25,000 to $80,000 in fees for a mid-sized tech firm, with first-year totals of $60,000 to $150,000. Automation-supported fixed-fee delivery runs $4,000 for companies under 50 employees and $5,500 over 50, with the platform and accredited audit adding $4,000 to $5,000, for a total around $10,000 to $12,000. Which number applies to you comes down to scope discipline, existing ISO 27001 maturity, and whether you insist on paying day rates for automatable work. If you want a scoped quote rather than a range, Axipro’s ISO 42001 consulting and implementation services run from standalone readiness assessments to end-to-end delivery with guaranteed certification on the Achievement Plan.
Frequently Asked Questions
What is the average hourly rate for an ISO 42001 consultant?
Experienced AI governance consultants charge $150 to $300 per hour in the US and UK markets in 2026. Most certification work has moved to fixed-fee packages, which start at $4,000 for companies under 50 employees and $5,500 above that, so hourly billing is now mainly for targeted reviews and audit-day support rather than full implementations.
How long does a typical mid-sized consulting engagement last?
Six to twelve weeks of active implementation work, inside a 4 to 8 month calendar from kickoff to certificate. The constraint is rarely the consulting itself. The AIMS has to operate long enough to generate the evidence auditors need at Stage 2, and firms with an existing ISO 27001 program land at the short end.
Can we use the same consultant for ISO 27001 and ISO 42001?
Yes, and you usually should. The standards share the same management system structure, so one partner can integrate the two programs, reuse documentation, and coordinate combined audits. Bundling both frameworks commonly saves 20 to 30 percent against separate engagements.
Do consultants guarantee certification success?
Implementation is one-time, but the certificate creates recurring costs: annual surveillance audits, recertification every three years, and program upkeep. Many mid-sized firms cover this with a light monthly maintenance plan rather than staffing AI governance internally, at a fraction of the original implementation fee per year.