
ISO 14001:2026 took effect on April 15, 2026, and it carries the first genuinely new clause the environmental standard has seen in over a decade. Any checklist built against the 2015 edition is now partly out of date. The structure auditors examine has shifted to the ISO Harmonized Structure, climate change is written into the requirements rather than bolted on through an amendment, and a new change management clause gives certification bodies a fresh place to record findings.
This guide breaks down what an ISO 14001 certification audit checklist needs to cover now, clause by clause, and how to use it without turning your environmental management system into a paperwork exercise.
What Is an ISO 14001 Audit Checklist?
An ISO 14001 audit checklist is a structured set of questions and verification points an auditor works through to confirm an environmental management system (EMS) meets the requirements of the standard. It maps each clause to specific evidence: documents, records, interviews, and observed practice. The checklist is the auditor’s working tool, not the audit itself.
A good checklist prompts the auditor to look for objective evidence rather than tick boxes, and it leaves room to record where the documented system and actual practice diverge. That gap — between what the procedure says and what people actually do — is where most findings come from.
Why You Need an ISO 14001 Audit Checklist
Without a checklist, audits drift. Auditors skip clauses, linger on the areas they find interesting, and produce findings that are hard to compare year over year. A checklist enforces coverage and consistency, which matters most when more than one auditor works the program or when you want surveillance results that trend cleanly against the baseline.
It also protects you before the certification body arrives. A disciplined internal audit run against a checklist that mirrors the external audit surfaces the same nonconformities your registrar would — while you still have time to fix them. The checklist turns a once-a-year scramble into a repeatable process.
Worth knowing: ISO 19011
ISO 19011 is the international guideline for auditing management systems, and it is not a standard you can certify against. You cannot become "ISO 19011 certified." It exists to make your audit program competent and consistent — which is exactly what a third-party auditor checks when they review your internal audit records.
Types of ISO 14001 Audits
Not every audit serves the same purpose, and your checklist depth should match the audit type. The four you will encounter are internal, second-party, third-party certification, and the surveillance and recertification audits that follow.
Internal Audit
Sometimes called a first-party audit, this is conducted by or on behalf of the organization itself. It is a requirement of Clause 9.2, and it is the single most important audit you run, because it is the one you control. Internal audits should be planned across a program, cover the full EMS over the cycle, and use auditors who are competent and independent of the work they assess.
Second-Party Audit
A second-party audit is one organization auditing another it has a relationship with — most often a customer auditing a supplier or a company auditing its contractors. Under the 2026 revision, with its sharper focus on externally provided processes, products, and services, expect more of these as larger buyers push environmental criteria down their supply chains.
Third-Party Certification Audit
This is the audit that earns the certificate. An accredited certification body assesses your EMS against ISO 14001 in two stages.
- Stage 1 is a readiness review that checks whether the system exists, is documented, and is ready to be assessed.
- Stage 2 verifies that the EMS is fully implemented, effective, and producing the results it claims. Certification follows only once any major nonconformities are closed.
Surveillance and Recertification Audits
ISO management system certificates run on a three-year cycle governed by ISO/IEC 17021-1. After initial certification, the body conducts annual surveillance audits in years two and three to confirm the system is still operating, then a recertification audit before the certificate expires. Surveillance audits are narrower than the full assessment, but they are not a formality — and many organizations will fold their move to ISO 14001:2026 into a surveillance or recertification visit to keep cost and disruption down.
ISO 14001 Audit Checklist: Clause-by-Clause Breakdown
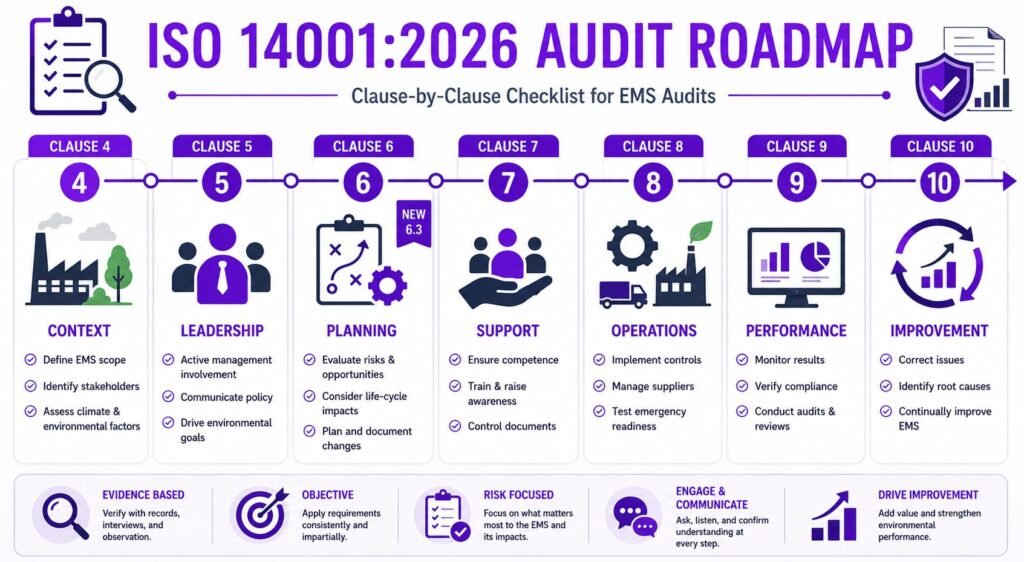
ISO 14001:2026 follows the ISO Harmonized Structure, the common framework shared with ISO 9001, ISO 45001, and ISO/IEC 27001. The familiar Plan-Do-Check-Act cycle still runs underneath it. Clauses 1 through 3 cover scope, references, and terms. The auditable requirements live in Clauses 4 through 10, and that is where your checklist does its work.
Clause 4: Context of the Organization
Verify that internal and external issues, interested parties, and the EMS scope are identified and documented. This is where the 2026 revision lands hardest. Context analysis must now explicitly weigh environmental conditions — including climate change, biodiversity, pollution levels, and the availability of natural resources. A context review that mentions only commercial and regulatory factors will draw a finding.
Clause 5: Leadership and Commitment
Check for evidence that top management is involved in substance, not ceremony. The environmental policy must be documented, communicated, and appropriate to the organization. Auditors look for real engagement: leaders who can speak to the policy, the objectives, and how environmental performance feeds into business decisions. The 2026 wording tightens leadership accountability, so a policy signed once and forgotten will not hold up.
Clause 6: Planning and Risk Assessment
This clause covers environmental aspects and impacts, compliance obligations, risks and opportunities, and objectives. It generates more nonconformities than almost any other. The life cycle perspective in Clause 6.1.2 is strengthened, with clearer expectations on upstream and downstream impacts. The headline change is Clause 6.3, Planning of Changes — the only entirely new clause in the revision. It requires a structured, planned approach to changes that affect the EMS, such as new products, site relocations, supplier changes, or process redesigns.
Insider note: Clause 6.3 is where auditors will probe hardest in 2026 transition audits, because most organizations have no formal change management process for their EMS yet. You do not need a standalone procedure. You do need to show that a planned change was evaluated for environmental impact before it happened, with evidence to prove it. Pull two or three recent changes and walk them through your process before the auditor asks you to.
Clause 7: Support (Resources, Competence, Communication)
Confirm that resources, competence, awareness, communication, and documented information are all controlled. Check training records against defined competence requirements, verify that staff understand their role in the EMS, and test document control by asking whether the version in use is the current one. Documented information is a frequent source of minor findings — usually because a procedure was updated and the working copy was not.
Clause 8: Operational Control
For each significant environmental aspect, the checklist should confirm that operational controls exist, are followed, and produce the intended results. The 2026 revision broadens Clause 8.1 from outsourced processes to externally provided processes, products, and services, thereby pulling suppliers more firmly into scope. Emergency preparedness and response also sit here, and the revision now separates genuine emergencies from abnormal operating conditions. The real test is the gap between the documented control and what you observe on the floor.
Clause 9: Performance Evaluation and Monitoring
Verify monitoring, measurement, analysis, and evaluation — including the evaluation of compliance, internal audit, and management review. Evaluation of compliance under Clause 9.1.2 is one of the most commonly cited nonconformities. Identifying your legal obligations is not the same as demonstrating that you know your compliance status, and auditors expect to see how you confirm it.
Clause 10: Improvement and Corrective Actions
Check that nonconformities are identified, corrected, and prevented from recurring, and that continual improvement is real. The content here is largely unchanged in 2026, with some consolidation and renumbering. The common failure is closing corrective actions without genuine root cause analysis, so problems reappear at the next audit. Look for tools like the five whys, evidence that actions were tracked to completion, and proof that effectiveness was verified rather than assumed.
Pro Tip: Add two columns to your legal register
Add two columns to your legal register — one for current compliance status, and one stating how you know it (for example, "monthly discharge inspection" or "quarterly permit review"). Then record results where you conform, not only where you fall short. Selective recording — capturing only the gaps — signals to an auditor that the evaluation was not systematic, and that observation alone can trigger a finding.
Core Components of an ISO 14001 Audit Checklist
Beyond the clause structure, a working checklist pulls specific artifacts into view. It should confirm the environmental policy is current and genuinely drives objectives, and that environmental aspects and impacts have been identified across normal, abnormal, and emergency conditions using a documented significance method. Inadequate aspect identification is one of the most common nonconformity triggers, so this deserves real attention.
It should verify legal and regulatory compliance — with evidence of how compliance status is confirmed — and that objectives, targets, and environmental programs are measurable and resourced. Cover roles, responsibilities, and authorities, along with competence, training, and awareness backed by records that match defined requirements.
The remaining components are the ones auditors lean on hardest for evidence: documented information and record control, operational controls and emergency preparedness, and monitoring, measurement, analysis, and evaluation. Finally, the checklist must reach the EMS’s own self-policing: internal audit records and management review records, and nonconformity and corrective action tracking. A weak internal audit program is the single most common root cause behind findings raised at certification — so this section is not optional.
Auditing ISO 14001 and ISO 45001 Together
Most sites that hold ISO 14001 also hold ISO 45001, and often ISO 9001 as well. Since all three now follow the ISO Harmonized Structure, one integrated audit checklist is the sensible default. Clauses 4, 5, 7, 9 and 10 ask near-identical questions of each system: context, leadership, competence, document control, internal audit, management review, corrective action. Audit them once, record the evidence once, and tag each finding with the standards it affects.
The differences sit in Clauses 6 and 8, and that is where an integrated checklist needs separate rows. Under ISO 14001 you are checking environmental aspects, compliance obligations and the new Clause 6.3 planning of changes. Under ISO 45001 you are checking hazard identification, worker consultation and OH&S risk. In Clause 8, environmental emergency preparedness and OH&S incident response share a procedure on paper far more often than they share a drill log. Keep the operational control rows separate per standard, even if the people you interview are the same.
Two practical rules keep integrated audits honest. First, give the legal register one row per obligation with a column for the standard it belongs to, so a review that covered health and safety permits cannot be mistaken for one that covered environmental ones. Second, write findings against the specific clause of the specific standard. “Clause 9.1.2 nonconformity” means nothing on an integrated report until you say which 9.1.2. The ISO 9001:2026 changes follow the same structure, so a checklist built this way extends to a three-standard audit without rework.
How to Use the ISO 14001 Audit Checklist Effectively
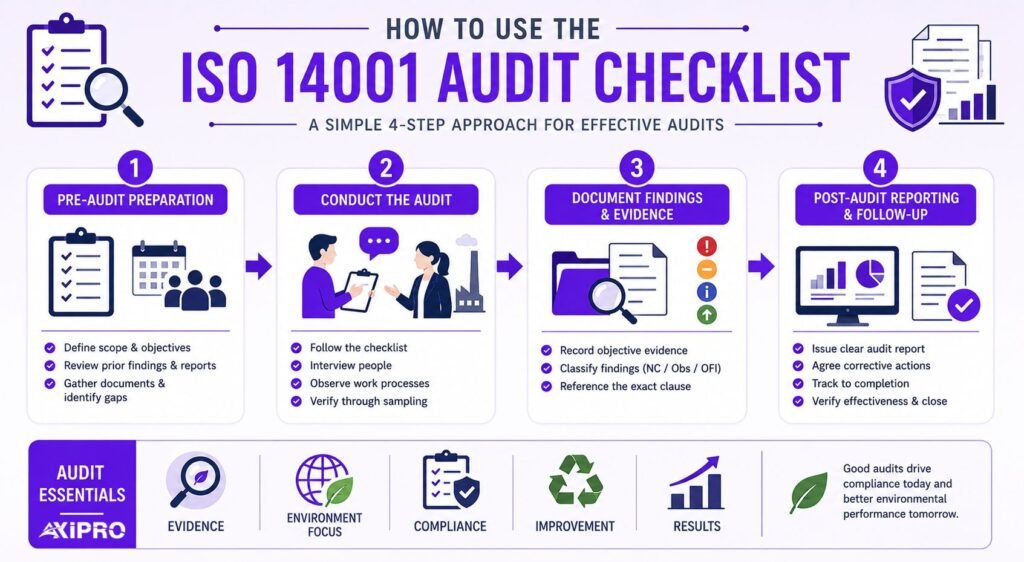
Pre-audit preparation sets the tone. Define the scope and objectives, schedule the right people, and review prior findings, previous audit reports, and the documents you will need. A gap analysis against the standard before you start tells you where to dig.
Conducting the on-site audit means following the checklist while staying alert to what it does not anticipate. Interview people, watch the work, and trace claims back to evidence. Sample across shifts and sites rather than accepting a single tidy example.
Documenting findings and evidence is where audits earn their value. Record objective evidence for every finding, and draw evidence from more than one source per point. Classify each finding clearly — as a major nonconformity, minor nonconformity, observation, or opportunity for improvement — and reference the exact clause.
Post-audit reporting closes the loop. Issue a written report, agree corrections and corrective actions with the responsible managers, and track them to completion. A finding without a verified, effective corrective action is just a note that will reappear next year.
ISO 14001 Audit Checklist Template
A usable template gives each clause its own row or section, with columns for the requirement, the question, the evidence reviewed, the finding type, and a notes field. Leave space to record the source of evidence and the responsible owner. The best templates are organized by clause so they map directly to the structure a certification body uses, which makes year-over-year comparison straightforward.
Whatever format you choose, the 2026 version must include rows for Clause 6.3 change management and the expanded environmental conditions under Clause 4 — or it will miss the parts most likely to generate findings during transition.
Download the ISO 14001:2026 Internal Audit Checklist
The template below is the one we use to prepare clients for Stage 1 and Stage 2. It covers every requirement in Clauses 4 through 10 of ISO 14001:2026, one row per requirement, written as an audit question rather than as the text of the standard. That is deliberate. The standard’s own wording is copyrighted, and a “shall” statement copied into a checklist invites a yes-or-no answer. A question forces the auditor to name the evidence.
Each row has six columns: the 2026 clause reference, the matching 2015 clause where one exists, the audit question, the evidence to look for, the finding type, and the owner. The 2015 mapping column matters during the transition period, because most certified organizations will run at least one internal audit while their documentation still references the old numbering. The integrated rows for ISO 45001 and ISO 9001 described above follow the same format.
Open the ISO 14001:2026 Internal Audit Checklist in Google Sheets below and make a copy to use it.
A sample of what the rows look like:
Clause (2026) | Clause (2015) | Audit question | Evidence to look for |
|---|---|---|---|
4.1 | 4.1 | Does the context analysis identify environmental conditions, including climate change, that can affect or be affected by the organization? | Context review or SWOT with environmental conditions listed; review date within the last cycle |
6.3 | New | Were recent changes affecting the EMS evaluated for environmental impact before implementation? | Change records for two or three recent changes; evidence the evaluation preceded the change |
8.1 | 8.1 | Are environmental requirements communicated to externally provided processes, products and services, and is conformance checked? | Supplier requirements, contract clauses, evaluation records |
9.1.2 | 9.1.2 | For each compliance obligation, is the current compliance status recorded and is the method of confirming it stated? | Legal register with status and method columns; results recorded where conforming, not only where not |
Common Mistakes to Avoid When Using an ISO 14001 Audit Checklist
The most damaging mistake is treating the checklist as the audit. A checklist worked mechanically — with no follow-up questions and no observation of actual practice — produces a clean report and a system full of hidden gaps. Auditors who only record nonconformities, and never note where the organization conforms, make the evaluation look unsystematic even when it was thorough.
Other recurring errors include incomplete aspect identification, internal audits that never cover the whole EMS across the cycle, management reviews that skip required inputs, and corrective actions closed without root cause analysis. Most ISO 14001 nonconformities are not design flaws. They come from gaps in implementation, inconsistent maintenance, thin documentation, and findings that were never properly fixed.
Tips for Auditors: Getting the Most Out of Your Checklist
Use the checklist as a floor, not a ceiling. It guarantees coverage, but the value comes from where you follow the evidence beyond it. Ask open questions and let people show you their work rather than confirming yours. Trace a single significant aspect all the way through — from identification to operational control to monitoring to review — because end-to-end tracing exposes the breaks that clause-by-clause questioning can miss.
Corroborate every finding from at least two sources, and write findings against the specific clause in plain language the auditee can act on. Stay current: an auditor still working from a 2015 mental model will miss Clause 6.3 and the broadened context requirements entirely.
Digital vs. Paper ISO 14001 Audit Checklists
Paper checklists are simple, need no setup, and work anywhere — which still matters in plants, remote sites, and areas with no connectivity. The cost shows up afterward, in manual transcription, version drift between copies, and the effort of trending results across audits.
Digital checklists — whether in a spreadsheet or dedicated audit software — capture evidence inline, enforce the current version, and make trending and corrective action tracking far easier. They carry a setup cost and depend on devices and access. For most programs running annual surveillance across the three-year cycle, the trending and version control alone justify going digital.
The Bottom Line
An ISO 14001 audit checklist is only as good as the standard it is built against — and as of April 2026, that standard is the new edition published by the International Organization for Standardization. Update your checklist for the Harmonized Structure, the integrated climate requirements, the broadened context analysis, and above all the new Clause 6.3 on planning of changes. Then use it the way it is meant to be used: as a tool that drives auditors toward evidence and honest findings, not a form that lets a weak EMS pass.
For broader context on building an environmental management system, the U.S. Environmental Protection Agency maintains useful public guidance, and the ISO 19011 auditing guidelines remain the reference for running a competent audit program.
The transition period runs three years from April 15, 2026, so certificates issued against the 2015 edition stop being valid around April 2029. Your certification body sets the exact date, and most will expect to see the 2026 clauses covered in at least one internal audit before the transition audit. If you have not yet moved your checklist across, the steps to ISO 14001 certification walk through where the transition fits in the cycle.
FAQs About ISO 14001 Audit Checklists
What should be included in an ISO 14001 internal audit checklist?
It should cover Clauses 4 through 10, with verification points for the environmental policy, aspects and impacts, compliance obligations, objectives, competence, operational controls, emergency preparedness, monitoring and evaluation, internal audit, management review, and corrective action. The 2026 version must add Clause 6.3 change management and the expanded environmental conditions under Clause 4.
Who is qualified to perform an ISO 14001 audit?
Internal audits require auditors who are competent and independent of the area they assess, with competence judged against the guidance in ISO 19011. Certification audits must be performed by an accredited certification body whose auditors meet the requirements of ISO/IEC 17021-1. A lead auditor qualification is the common credential for those running formal audits.
How often should ISO 14001 audits be conducted?
Internal audits run on a planned program that covers the whole EMS over time, typically across a year. Certification follows a three-year cycle: initial Stage 1 and Stage 2 assessments, annual surveillance audits in years two and three, then recertification before the certificate expires.
How long does an ISO 14001 audit take?
Duration depends on the size of the organization, the complexity of its processes, the number of sites, and the industry risk profile — with audit time calculated under ISO/IEC 17021-1 guidance. A small organization might face a Stage 2 audit of one to two days and shorter surveillance visits, while a large multi-site operation requires considerably more.
What is the difference between an internal and external ISO 14001 audit?
An internal audit is conducted by or for the organization itself to check and improve its own EMS. An external audit is conducted by an outside party — either a certification body awarding or maintaining the certificate, or a second party such as a customer assessing a supplier.
Can I use a free ISO 14001 audit checklist template?
Yes, a free template is a reasonable starting point, but treat it as a skeleton. Any generic template must be adapted to your significant environmental aspects, your compliance obligations, and your operations — and as of 2026 it must be updated for the new and revised clauses. An unedited template will leave gaps that produce findings.
What happens if nonconformities are found during the audit?
You analyze the cause, define corrections and corrective actions, and implement them. Certification bodies typically require this within a set window after the audit and then verify it. Major nonconformities must be closed before a certificate is granted or maintained. Minor nonconformities are usually verified at the next surveillance visit.
What is the difference between an ISO 14001 self-assessment checklist and an internal audit checklist?
A self-assessment is completed by the people who run the process, usually before the EMS is mature enough to audit, and it tells you whether something exists. An internal audit is carried out by someone independent of the area, and it tests whether the thing works and produces evidence. The questions can be identical. The difference is who answers them and what counts as proof.
Is an ISO 14001 gap analysis checklist the same as an audit checklist?
No. A gap analysis compares what you have against what the standard requires and produces a to-do list. An audit checklist assumes the system exists and tests whether it conforms and performs. Run the gap analysis first, build the system, then audit it. Using an audit checklist as a gap analysis tool tends to produce a long list of “nonconformities” against a system that was never designed yet.
Do I need to update my ISO 14001 checklist for the 2026 edition?
Yes, before your transition audit. At minimum, add rows for Clause 6.3 planning of changes, extend Clause 4 to cover environmental conditions including climate change, and widen Clause 8.1 from outsourced processes to all externally provided processes, products and services. Keep a 2015 clause column during the transition so findings from earlier audits still map.

