Global AI regulation is not converging. Four distinct regulatory models have hardened over the past two years: the EU’s single horizontal law, China’s fast-moving sequence of targeted rules, the American patchwork of state laws and voluntary frameworks, and the Gulf’s procurement-driven approach, where the state shapes the market by being its biggest customer. Anyone waiting for these to merge into one global rulebook will be waiting well past 2030.
That fragmentation, not any single law, is the defining trend in AI regulatory compliance. The practical question for 2026 through 2028 is no longer “which regulation applies to us” but “which regulatory model does each of our markets follow, and what carries over between them.” This article maps the four models, with extra time on the Gulf version because it gets far less coverage than it deserves. It also argues that ISO standards, led by ISO/IEC 42001, are becoming the only compliance credential that travels across all four.
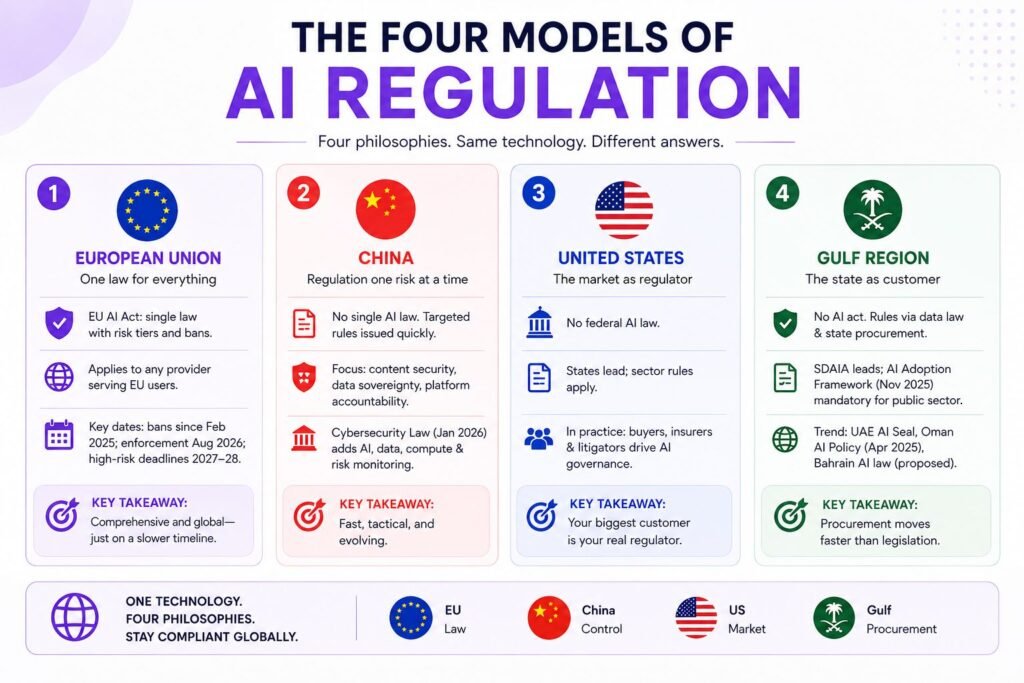
The Four Models of AI Regulation
Most trend pieces treat AI regulation as one global movement running at different speeds. It’s more useful to treat it as four philosophies that answer the same question in incompatible ways.
| European Union | China | United States | Gulf (KSA, UAE) | |
|---|---|---|---|---|
| Instrument | One horizontal law (EU AI Act) | Sequence of targeted departmental rules | State laws, voluntary frameworks, sector rules | Data law plus procurement requirements |
| Enforcer | Commission, national authorities, notified bodies | CAC and partner ministries | States, regulators, courts, buyers | SDAIA, NDMO, central banks, tender owners |
| Core concern | Fundamental rights, product safety | Content security, data sovereignty | Liability, consumer protection | National strategy, data sovereignty, state procurement |
| Speed | Slow to write, long lead times | Fast, iterative, hardening | Uneven, litigation-led | Fast: effective when a tender says so |
| What travels | Conformity assessment, technical files | Filings and labeling rarely reusable | Assurance reports, questionnaires | ISO certification as procurement signal |
The European Union: One Law for Everything
The EU chose a single horizontal statute, Regulation (EU) 2024/1689, better known as the EU AI Act. It classifies AI systems into risk tiers, bans a short list of practices outright, and attaches heavy obligations to high-risk systems: risk management, data governance, human oversight, technical documentation, and conformity assessment. It applies extraterritorially, so a Bahraini or American provider whose system reaches EU users is in scope.
The model’s strength is predictability, and its weakness is pace. Prohibitions have applied since February 2025 and general-purpose AI obligations since August 2025, with Commission enforcement beginning in August 2026. The 2026 digital omnibus agreement then deferred the main high-risk deadlines to December 2027 and August 2028. The EU writes slowly, publishes a timetable, and expects the world to plan around it.
China: Regulation One Risk at a Time
China has no single AI statute and doesn’t appear to want one yet. Instead, the Cyberspace Administration of China and partner ministries have issued targeted rules in rapid sequence: algorithmic recommendation provisions in 2022, deep synthesis rules in 2023, interim measures for generative AI services the same year, AI content labeling requirements in September 2025, and rules for anthropomorphic AI interaction services that took effect in July 2026. Each rule attacks one risk scenario, takes effect quickly, and gets refined through practice.
The direction of travel matters more than any single measure. China’s revised Cybersecurity Law, effective January 2026, wrote AI research, training data, computing infrastructure, and risk monitoring into a foundational statute for the first time. Soft guidance is hardening into binding law, and the organizing logic throughout is content security, data sovereignty, and platform accountability rather than individual rights. For foreign companies, the compliance burden is operational: filings, security assessments, and labeling obligations that arrive with short notice and almost no grace period.
The United States: The Market as Regulator
The US still has no federal AI statute, and the vacuum is being filled from two directions. States are legislating, with Colorado’s AI Act as the most complete example, and sector regulators are stretching existing consumer protection, employment, and financial rules to cover AI. The NIST AI Risk Management Framework sits underneath as the voluntary vocabulary everyone borrows.
In practice, the binding force in America is commercial. Enterprise buyers, insurers, and litigators enforce AI governance through security questionnaires, vendor reviews, and lawsuits long before any statute does. For a company selling into the US, the real regulator is the procurement team of your largest prospect.
The Gulf: The State as Customer
The Gulf model is the least covered and, for anyone selling into the region, the most misunderstood. Saudi Arabia has no horizontal AI act. It regulates AI through data law and through the state’s position as the dominant buyer in the economy. The Saudi Data and Artificial Intelligence Authority (SDAIA), established in 2019 and reporting directly to the Prime Minister, runs the show: it sets national strategy, publishes the frameworks, and steers what government tenders ask for, a far more hands-on role than most regulators play.
The load-bearing rules are the Personal Data Protection Law, enforced since September 2023, and its cross-border transfer regime. Around them sit SDAIA’s AI Ethics Principles, generative AI guidelines for government entities, and the AI Adoption Framework, published in November 2025 as a mandatory baseline for public sector bodies, with a four-tier risk classification and lifecycle auditing for high-impact systems. A draft Responsible AI Policy went through public consultation in May 2026, confirming that a formal, operational regime is coming. The Kingdom designated 2026 its Year of Artificial Intelligence, and the direction across the region matches: the UAE runs an AI Seal program and its central bank requires bias testing at financial institutions, Oman’s National AI Policy entered into force in April 2025, and Bahrain has a proposed AI law in progress.
The defining feature is speed through procurement. A requirement in a Saudi government tender takes effect the day the tender document is published, with no transition period and no parliamentary debate. High-risk use cases increasingly require self-assessments before tenders or go-lives. Regulation by purchase order moves faster than regulation by statute, and in state-led economies it reaches further too.
Worth Knowing: SDAIA & ISO 42001
SDAIA achieved ISO 42001 certification itself in July 2024, making it one of the first government AI authorities in the world to certify its own AI management system. When a regulator certifies itself against a standard, it's telling the market exactly what its procurement teams will ask for next.
What the Gulf Model Predicts for Everyone Else
Our prediction: the next twenty countries to get serious about AI governance will look more like Riyadh than Brussels. The Gulf template, a national AI authority, sovereign data rules, government-led adoption mandates, and procurement gates, can be stood up in two years without a legislature drafting a thousand-page act. It suits any state-led digital economy, which describes most of the emerging markets now writing AI strategy.
The evidence is already visible inside the region, with Oman and Bahrain following the same sequence Saudi Arabia and the UAE ran, and the pattern is spreading to parts of Southeast Asia and Africa. For compliance planning, that means procurement-driven, data-sovereignty-first regimes will govern a growing share of the world, and EU-style horizontal law won’t. Companies that only build for Brussels will keep getting surprised.
Let Axipro help you build a business continuity plan that's practical, compliant, and audit-ready.
Schedule Your Free Assessment Today
ISO Standards: The Portable Layer Across All Four Models
If the models won’t converge, the compliance question becomes: what carries over? The strongest answer available today is ISO/IEC 42001, the AI management system standard published in December 2023. A management system is regime-agnostic by design. It establishes governance, risk assessment, impact assessment, lifecycle controls, and continual improvement, which is the groundwork every one of the four models assumes you already have.
Each model rewards it differently. In the EU, ISO 42001 maps onto the AI Act’s governance obligations and gives you the organizational spine that conformity assessment hangs off. In the US, it functions as third-party assurance for buyers, the way ISO 27001 and SOC 2 already do. In the Gulf, it is a procurement signal endorsed by the regulator’s own certification, and increasingly a differentiator in competitive tenders. Even in China-adjacent supply chains, it works as a neutral baseline that no side objects to.
The standard is also growing a family.
- ISO/IEC 23894 covers AI risk management,
- ISO/IEC 42005 covers AI system impact assessments, and
- ISO/IEC 42006 sets requirements for the bodies that audit and certify AI management systems, which is professionalizing the certification market itself.
Together with ISO/IEC 27001 for information security, these form an integrated stack: one management system, one audit rhythm, multiple frameworks.
Our ISO 42001 implementation service is built around exactly that integration, because almost every 42001 client already holds or is pursuing 27001.
Important: ISO 42001 certification is not legal compliance in any jurisdiction. It doesn’t register your data processing in Saudi Arabia, file your algorithm in China, or complete your EU conformity assessment. Treat it as the chassis you bolt local requirements onto, not as a substitute for them. Vendors selling it as an “EU AI Act certificate” are selling something that doesn’t exist.
The Hardest Problem: Dual and Triple Exposure
The genuinely difficult compliance work of the next three years is not any single regime. It is the overlap. Picture a Riyadh SaaS company selling into the EU, or a London fintech entering Saudi Arabia. Building to the EU AI Act clears the bar on system governance in both places, but the Saudi side still fails without PDPL registration, transfer risk assessments, and the right SDAIA clauses in your contracts. The two regimes care about different things: Brussels wants proof of how the system is governed, Riyadh wants proof of where the data sits and who approved moving it. Neither accepts the other’s paperwork, so most companies end up doing the work twice.
Almost nobody has the internal capacity to run this. Axipro’s 2026 study of 3,519 AI-related LinkedIn job postings across eight EU countries found companies hiring roughly seven AI builder roles for every one AI governance role. The talent to operate even one regime in-house is scarce; the talent to operate three doesn’t meaningfully exist on the open market. That shortage, more than any deadline, will drive AI compliance hiring and outsourcing decisions through 2028.
The pattern we see with clients entering Saudi Arabia bears this out: model documentation is rarely what stalls a deal. PDPL registration and cross-border transfer assessments are, usually discovered mid-procurement when a tender checklist asks for evidence nobody knew was required.
Preparing for a Multi-Model World
Start by mapping your exposure by model, not by law: list your markets and buyers, then identify whether each one runs on horizontal law, iterative rules, market enforcement, or procurement gates. Then build the AI management system once, on ISO 42001, integrated with your existing ISO 27001 or SOC 2 program rather than parallel to it. Layer jurisdiction-specific controls on top: PDPL registration and transfer assessments for Saudi Arabia, technical documentation for the EU, questionnaire-ready assurance for the US.
And treat procurement requirements as your real deadlines. Legal compliance dates get deferred, as the EU just demonstrated, but a tender closes when it closes and an enterprise security review happens when your champion needs it to. Companies working across the GCC should start from the regional data and cybersecurity baselines, which is why we maintain dedicated guidance on GCC compliance frameworks like NCA ECC and SAMA CSF alongside the AI-specific work. On timelines, be realistic: for a company with an existing ISO 27001 system, ISO 42001 readiness typically takes 6 to 8 weeks; from a standing start it takes meaningfully longer, and certification body scheduling adds lead time that catches teams off guard.
Pro Tip: Selling to governments or large enterprises
If you sell to governments or large enterprises in the GCC, don't wait for a statute to tell you what to do. Pull the AI and data clauses from the last three tenders in your pipeline and treat them as your requirements document. Procurement language in the Gulf runs 12 to 18 months ahead of published regulation, and it's a more honest predictor of what you'll actually be asked to evidence.
The future of AI regulatory compliance is plural. The EU, China, the US, and the Gulf have each committed to a model, the models reward different things, and the Gulf’s procurement-led version is the template most of the world’s next adopters will copy. No single law will tell you what to do everywhere, but a well-built AI management system on ISO 42001, integrated with your existing security program and extended with local controls, is the closest thing to a passport this fragmented map allows. Build the portable layer first, and every border crossing after that gets cheaper.
Frequently Asked Questions
Will AI regulations become globally standardized?
No, not in any planning horizon that matters. The EU, China, the US, and the Gulf states have committed to structurally different regulatory models, and each is deepening its own approach rather than converging. What’s standardizing is the management-system layer underneath, where ISO/IEC 42001 is emerging as the common baseline that jurisdiction-specific rules layer on top of.
How does China regulate AI compared to the EU?
The EU passed one comprehensive, rights-focused law with published deadlines. China issues narrow, fast-moving rules one risk at a time, covering algorithms, deepfakes, generative AI, content labeling, and interactive AI services, coordinated by the Cyberspace Administration of China and anchored in content security and data sovereignty. China’s approach is faster to update and harder to plan around, and it’s currently hardening from guidance into binding law.
Does Saudi Arabia have an AI law?
Not a horizontal one. Saudi Arabia regulates AI through the Personal Data Protection Law, SDAIA frameworks like the AI Adoption Framework, and requirements embedded in government procurement. A draft Responsible AI Policy completed public consultation in May 2026, so a formal regime is taking shape, but today the binding obligations sit in data law and tender documents rather than an AI act.
Is ISO 42001 certification mandatory anywhere?
No jurisdiction currently mandates ISO 42001 by statute. In practice it’s becoming a de facto requirement in two places: GCC public sector procurement, where the regulator itself is certified and tenders increasingly ask for it, and enterprise vendor reviews, where it answers AI governance questions the same way ISO 27001 answers security ones. It’s voluntary on paper but increasingly decisive in deals.
Where should a company operating in both the EU and the Gulf start?
Start with the shared layer: an ISO 42001 management system integrated with your existing ISO 27001 or SOC 2 program. Then handle the Gulf-specific data obligations, PDPL registration and transfer risk assessments, before EU technical documentation, because they surface earlier in deals and have no EU equivalent you can reuse. Sequencing this way means every artifact you build serves at least two regimes.